In August 2026, TP-Link disclosed two vulnerabilities (CVE-2026-15315 and CVE-2026-15316) in its Tapo cameras, discovered by OPSWAT researchers. One of them was an authentication bypass that could allow an attacker on the same local network to gain administrative access without knowing the camera owner's credentials. But that was only part of the story.
Our researchers uncovered something even more significant: a way to turn unauthorized administrative access into operating system command execution, potentially leading to a complete compromise of the affected camera.
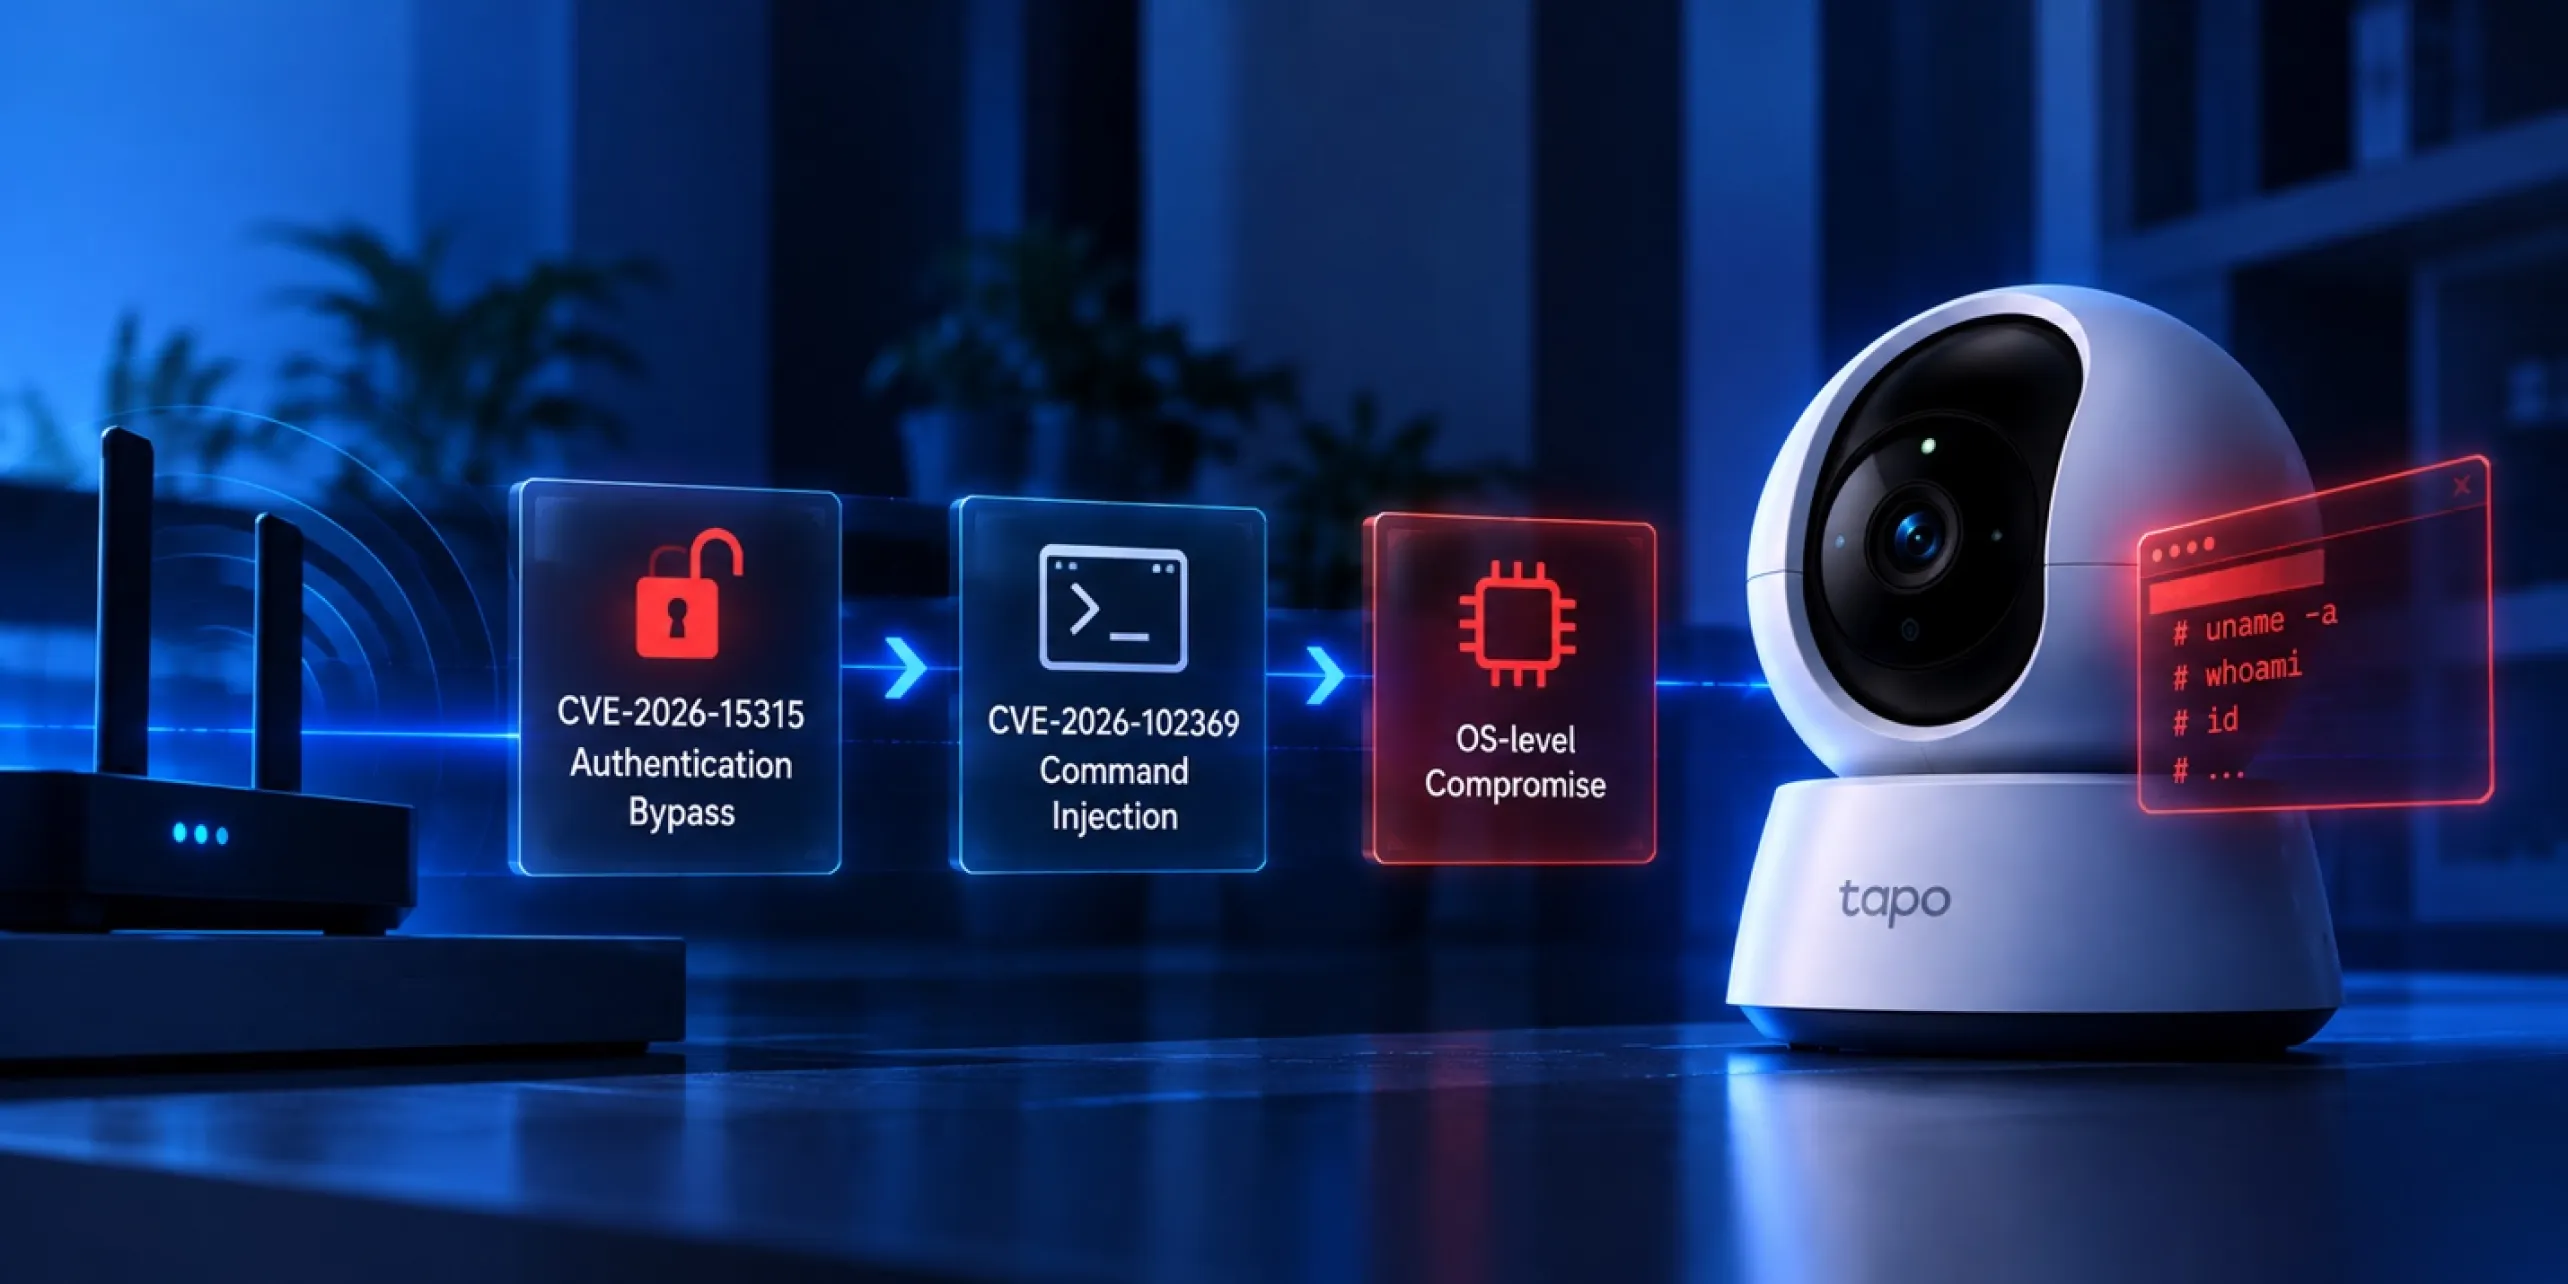
On October 1, 2026, TP-Link officially published four additional CVEs from the same research, bringing the total to six disclosed vulnerabilities. Among them, CVE-2026-102369, a command injection vulnerability in the camera's MacTool handler, represents the missing piece of the exploit chain. When combined with the previously disclosed authentication bypass, it demonstrates how an unauthenticated attacker on the same local network could compromise the camera at the operating system level.
These vulnerabilities were discovered by Khoi Tran, under the mentorship of Thai Do from OPSWAT Unit 515.
Building on our previous disclosure of CVE-2026-15315 and CVE-2026-15316, this article introduces the four newly disclosed vulnerabilities, takes a closer look at the command injection vulnerability, and reveals the complete exploit chain behind our TP-Link Tapo camera research.
Four Additional CVEs: Uncovering Deeper Security Risks in TP-Link Tapo Cameras
The newly disclosed vulnerabilities, identified during our research, affect TP-Link Tapo C200 V5 and Tapo C120 V1 cameras, revealing security weaknesses across Wi-Fi onboarding interfaces and privileged diagnostic functionality. While the findings vary in severity and impact, they demonstrate how missing authentication controls and insufficient input validation can expose critical device functions to unauthorized access and potentially lead to more serious security consequences.
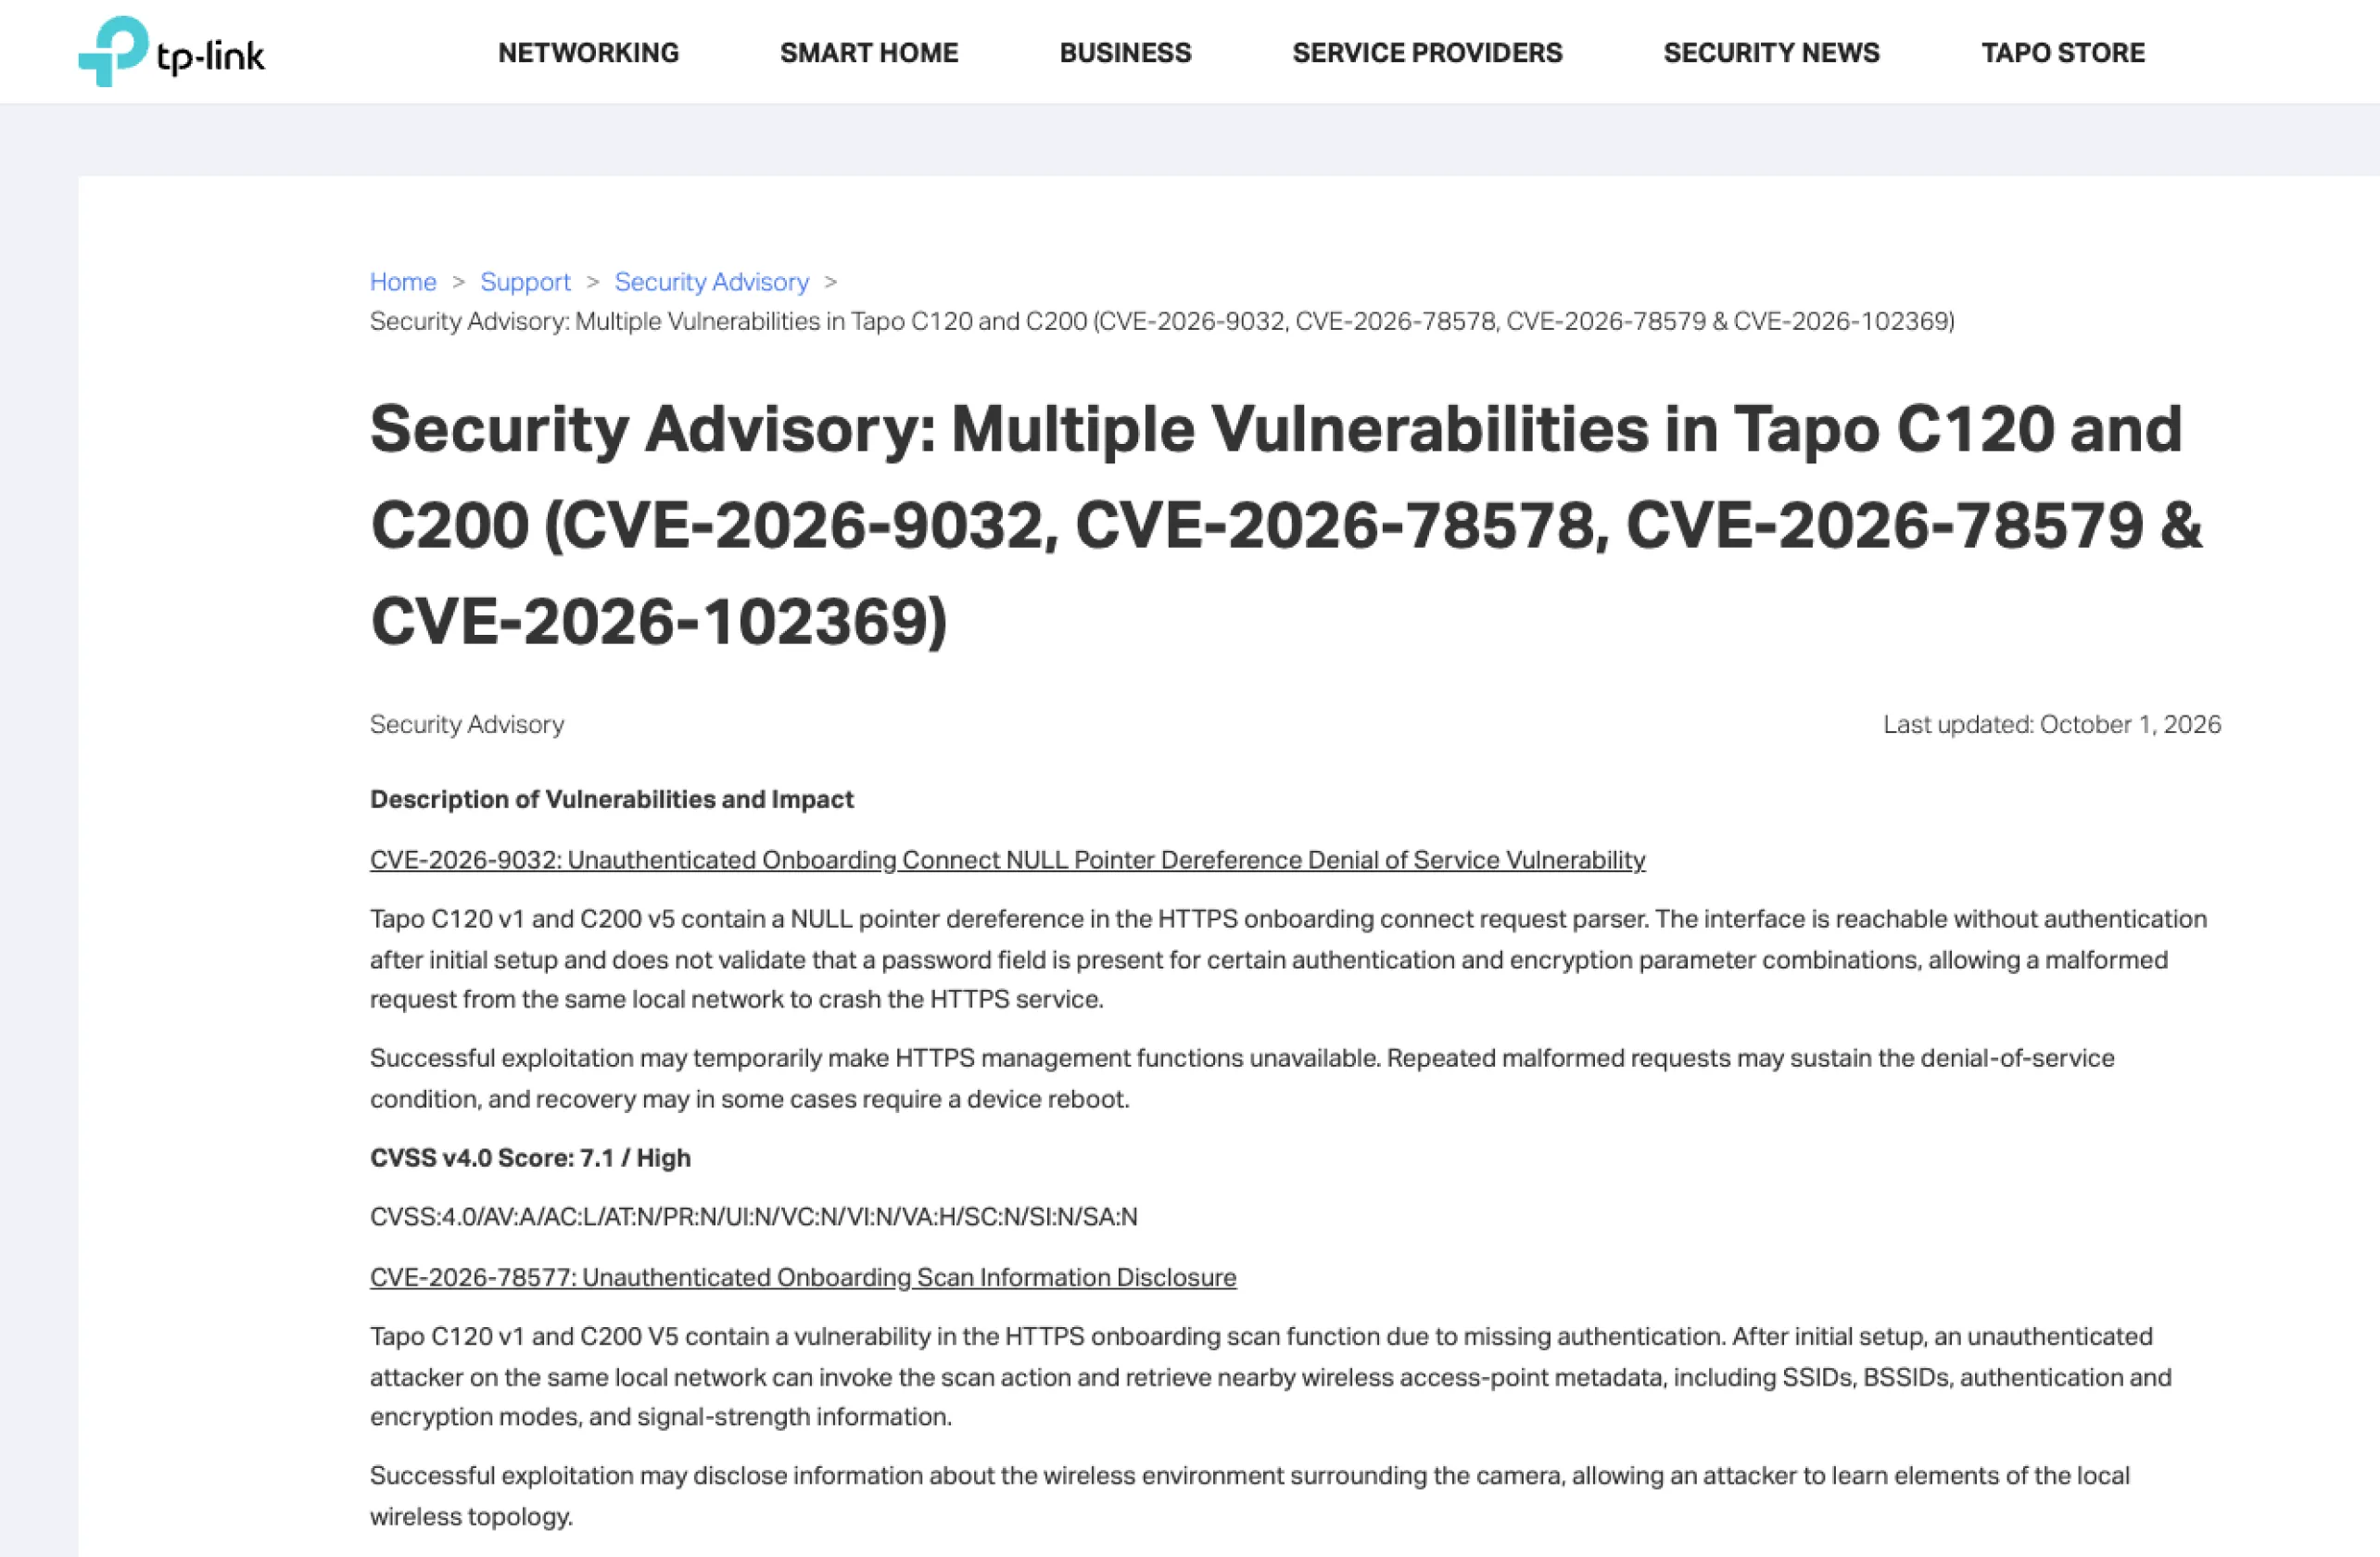
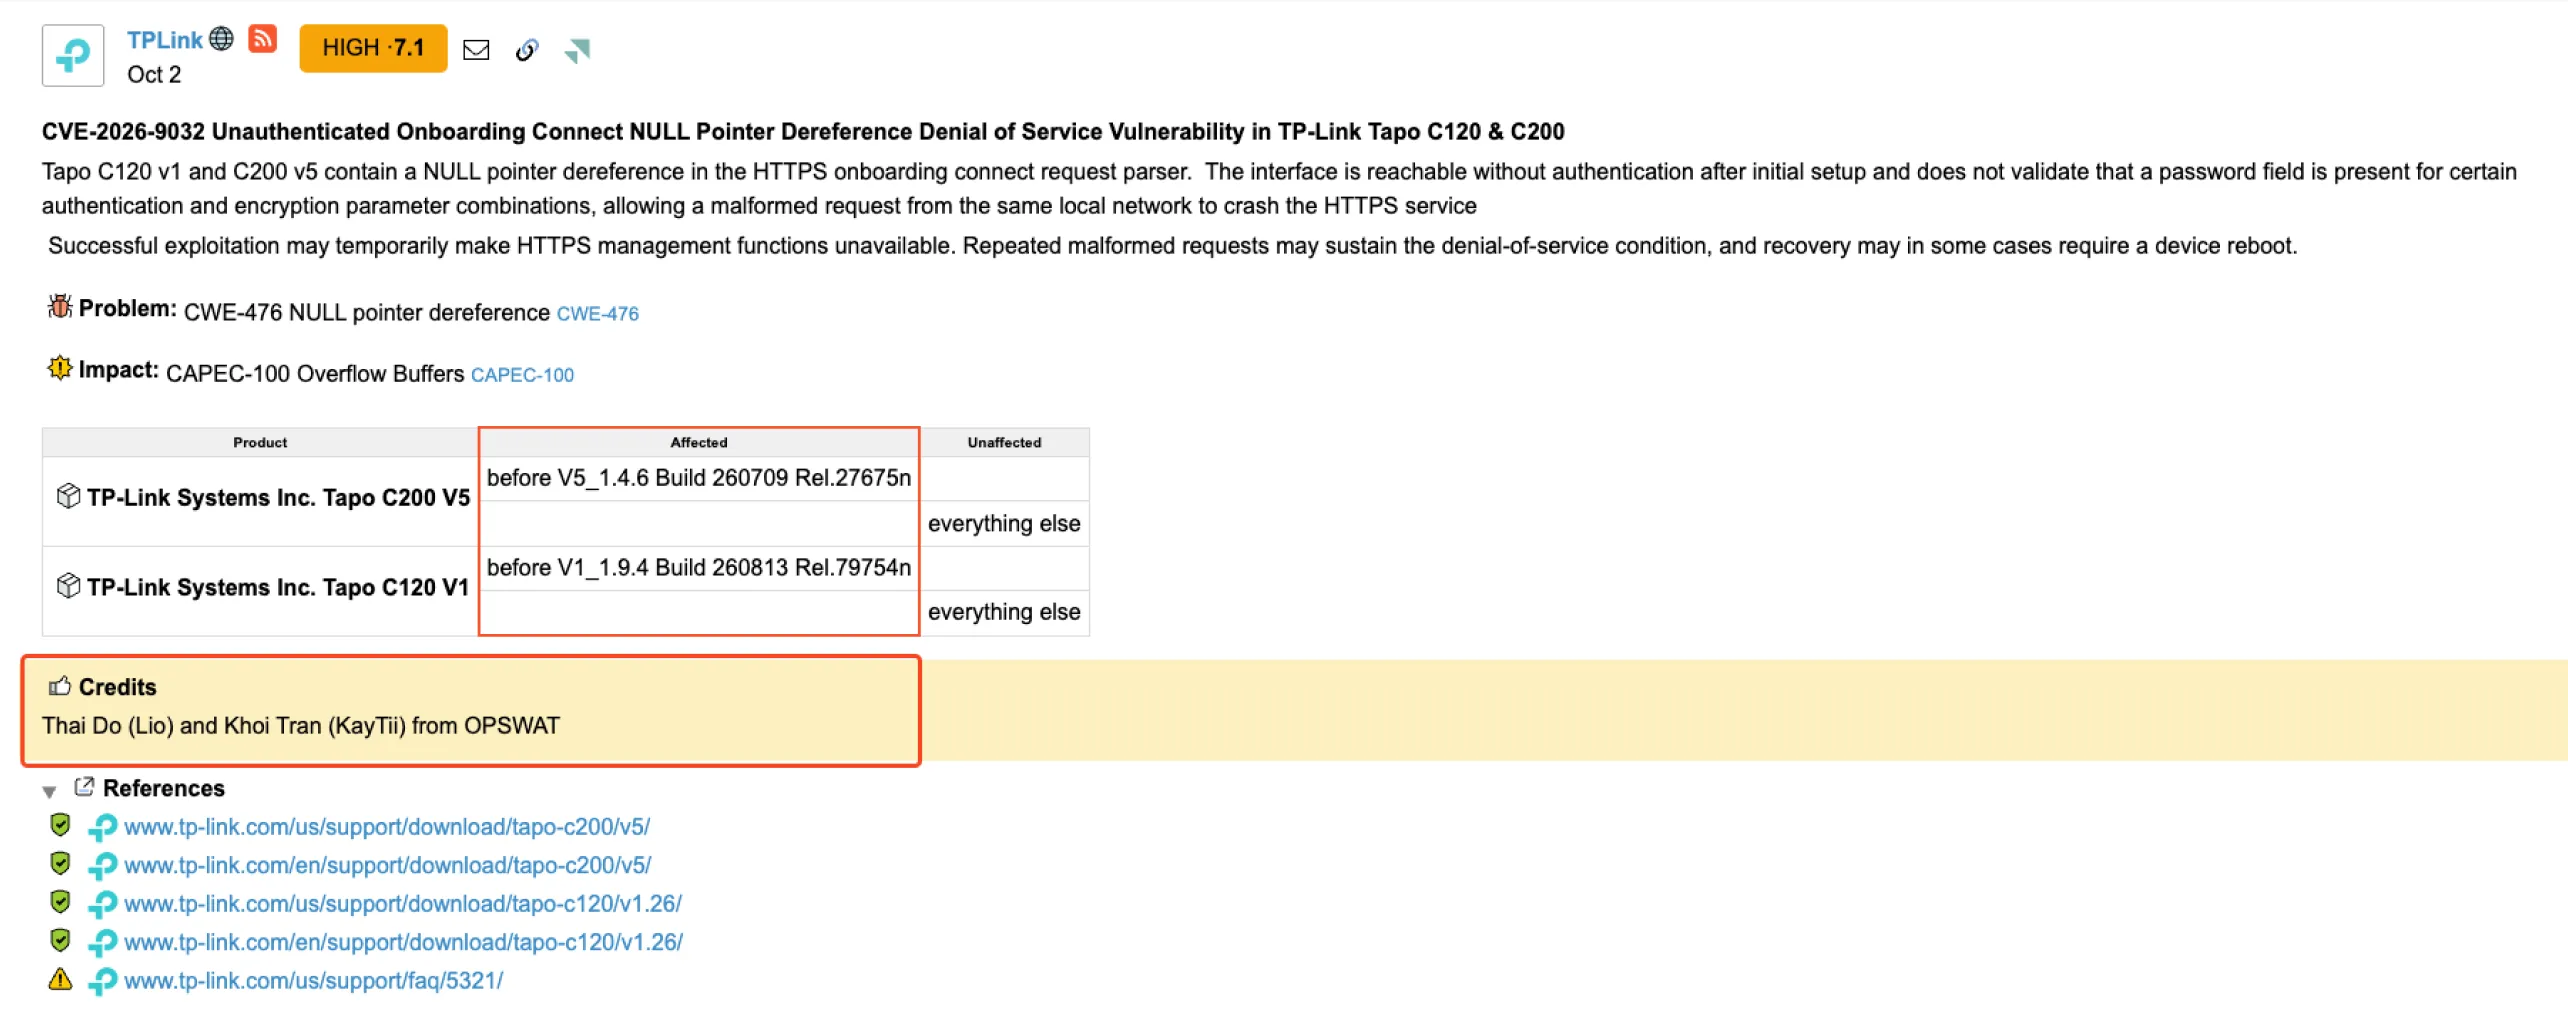
Two of the vulnerabilities directly threaten device availability. CVE-2026-9032 (High, CVSS 7.1) involves a NULL pointer dereference in the HTTPS onboarding interface, allowing an unauthenticated attacker to crash the camera's HTTPS service. Meanwhile, CVE-2026-78578 (High, CVSS 7.1) exposes a missing authentication check in the Wi-Fi configuration functionality, enabling unauthorized changes that could disconnect the camera from its intended network.
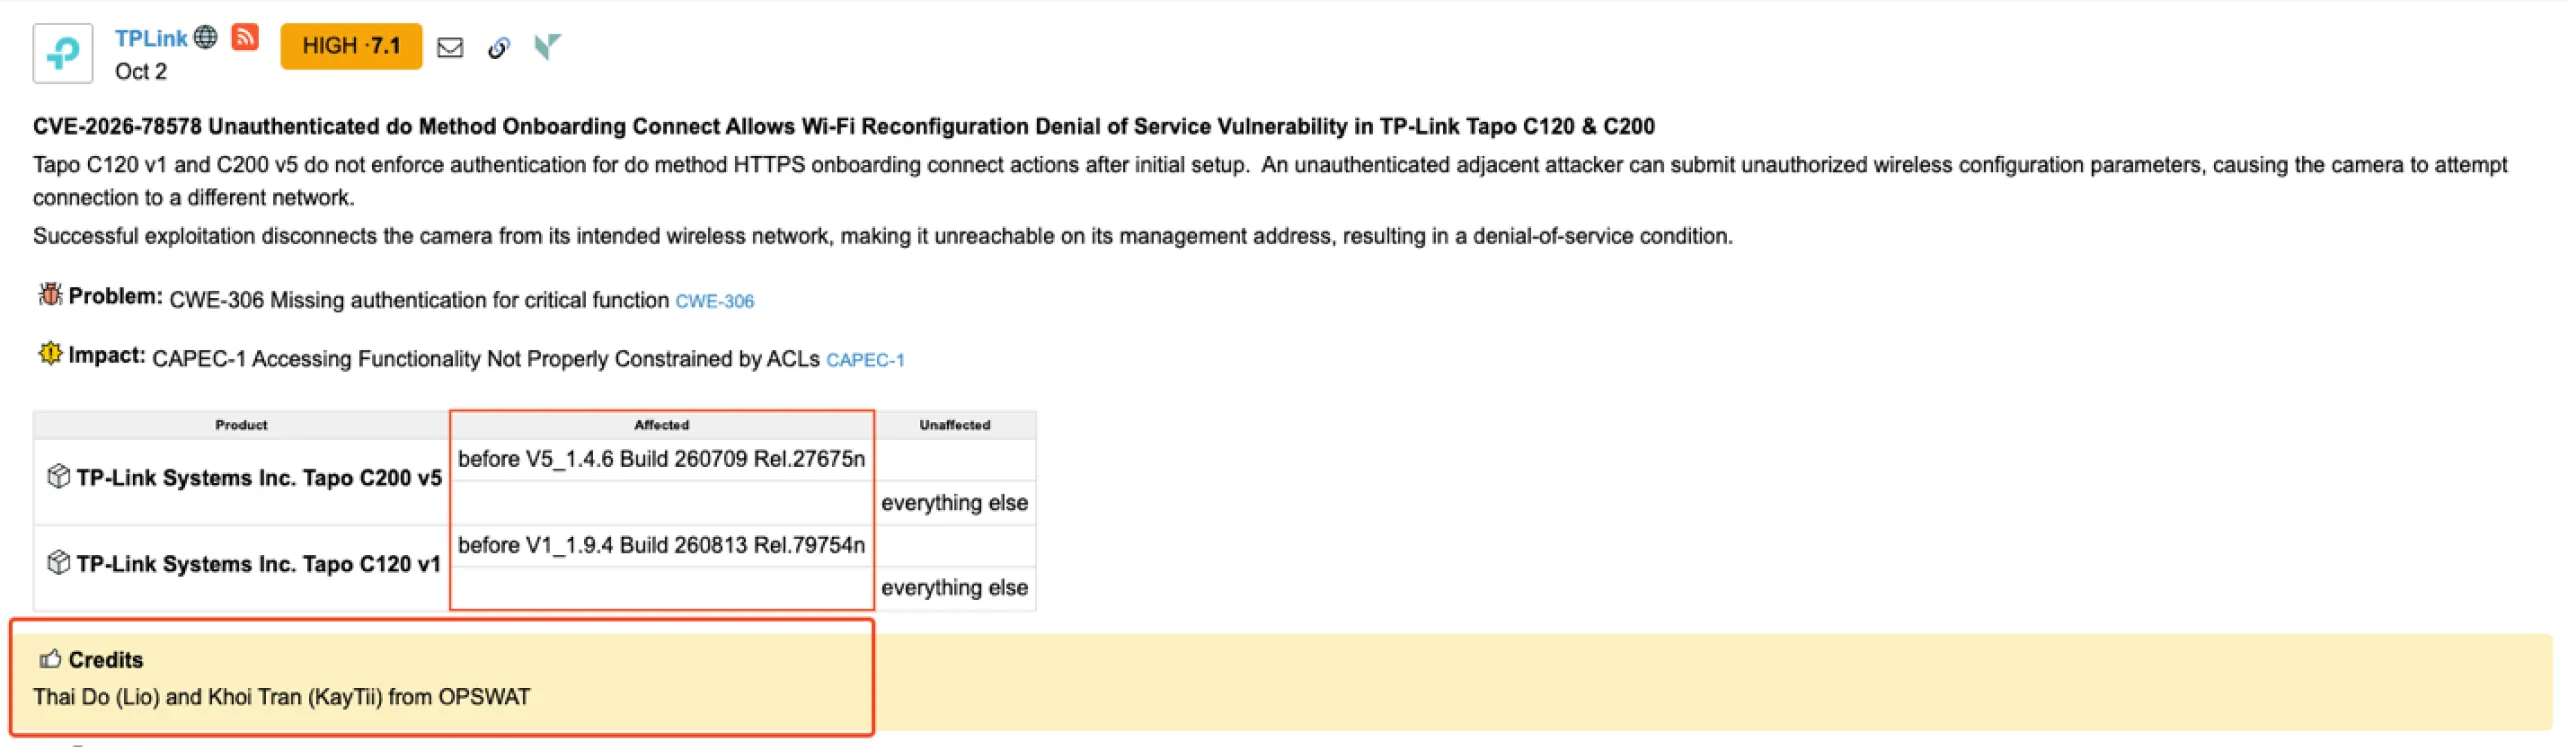
Beyond service disruption, CVE-2026-78577 (Medium, CVSS 5.3) introduces an information disclosure risk. Due to missing authentication in the Wi-Fi scanning functionality, an attacker could retrieve information about nearby wireless networks, including SSIDs, BSSIDs, and security configurations, potentially revealing details of the surrounding network environment.
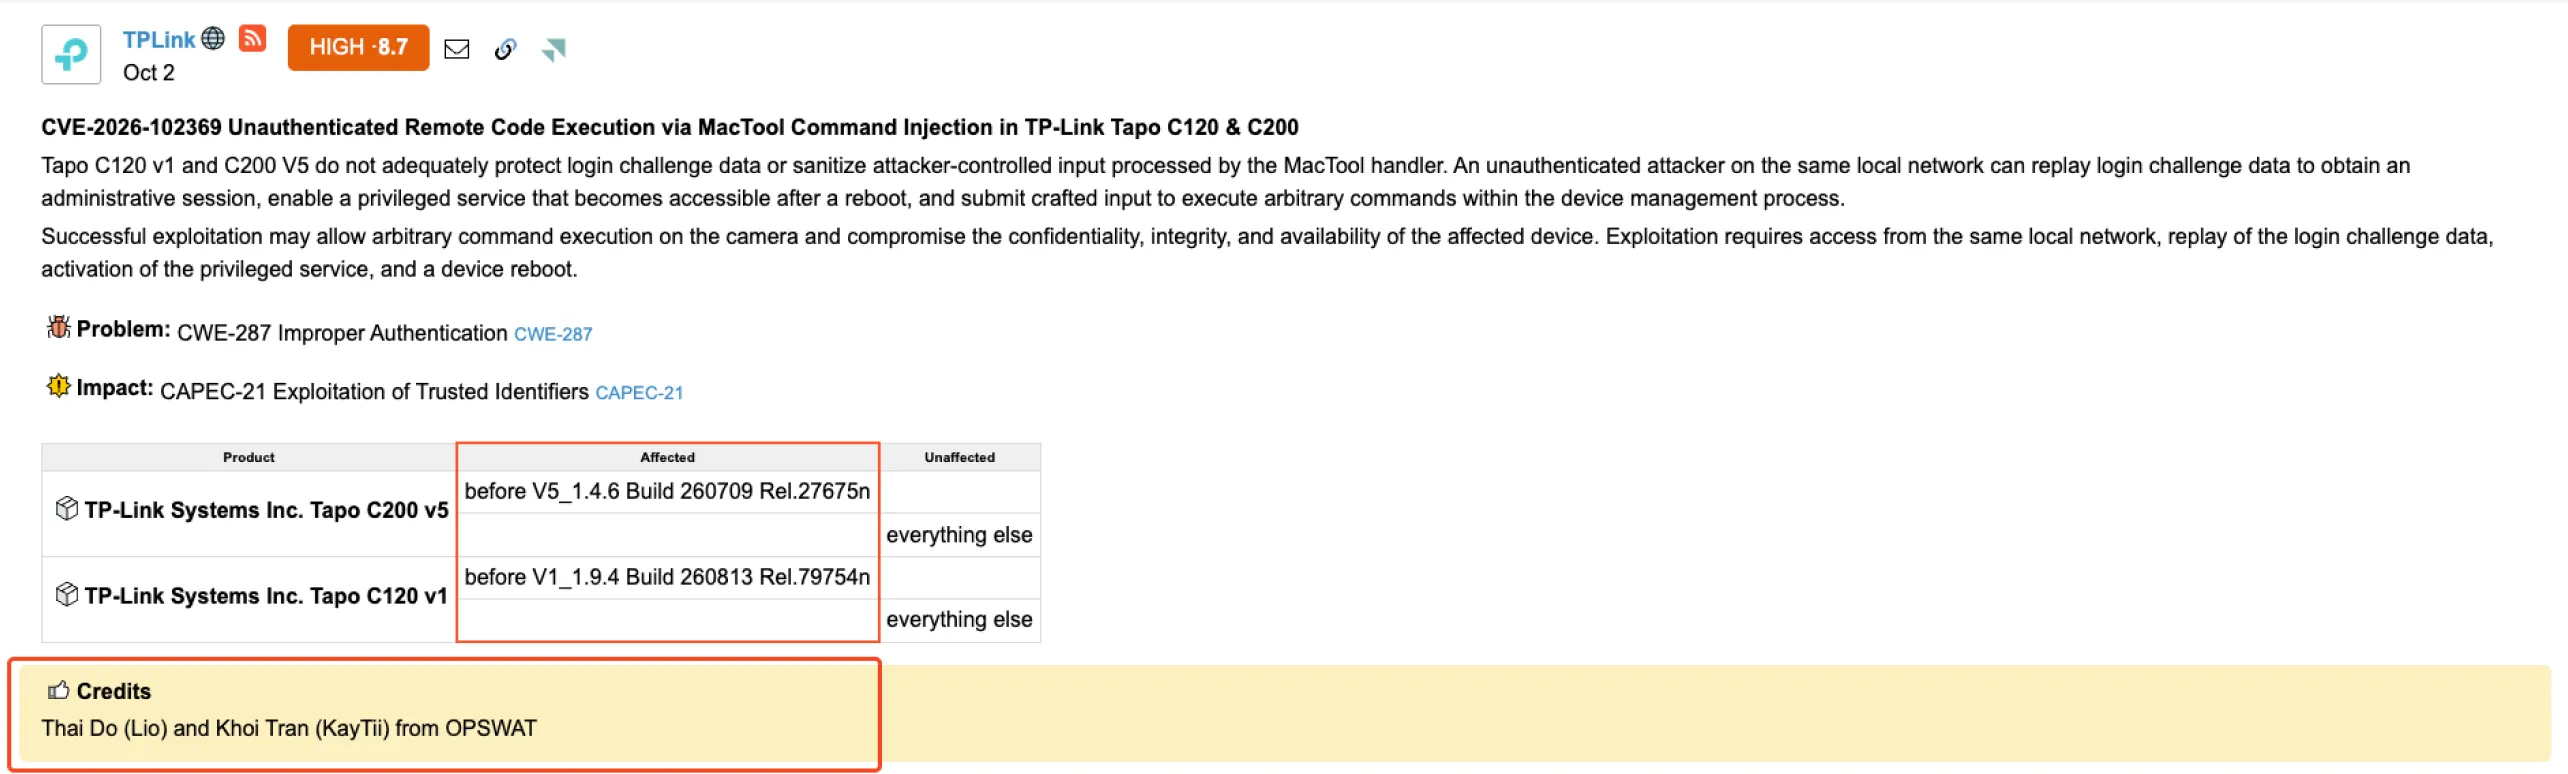
However, the most significant discovery lies deeper within the camera's diagnostic functionality. CVE-2026-102369 (High, CVSS 8.7) is a command injection vulnerability in the MacTool handler of the TMPD service, where improperly handled input results in arbitrary operating system command execution. Unlike the other findings, which primarily affect connectivity, availability, or information disclosure, this vulnerability creates a pathway to compromise the camera at the operating system level.
The following section takes a closer look at CVE-2026-102369 and its critical role in the exploit chain uncovered by OPSWAT researchers. To minimize the risk of misuse, we have intentionally omitted detailed exploitation steps and exploit code.
CVE-2026-102369: Command Injection in TP-Link's MacTool Diagnostic Service
The vulnerability resides in TMPD, a factory diagnostic service found in TP-Link Tapo C200 and C120 cameras. Through its MacTool interface, TMPD provides manufacturing and maintenance capabilities, including hardware diagnostics, device configuration, and file transfers using the Trivial File Transfer Protocol (TFTP). While these functions are intended for legitimate device maintenance, improper handling of external input within this privileged service introduces a significant security risk.
During firmware analysis, Khoi and Thai discovered that the MacTool handler processes TFTP file-transfer requests by incorporating user-controlled parameters directly into command strings without adequate input validation. These constructed commands are subsequently passed to a system-level function that invokes the underlying operating system shell. As a result, specially crafted input can be interpreted as executable shell instructions rather than ordinary file-transfer parameters, allowing an attacker with access to the service to execute arbitrary operating system commands.
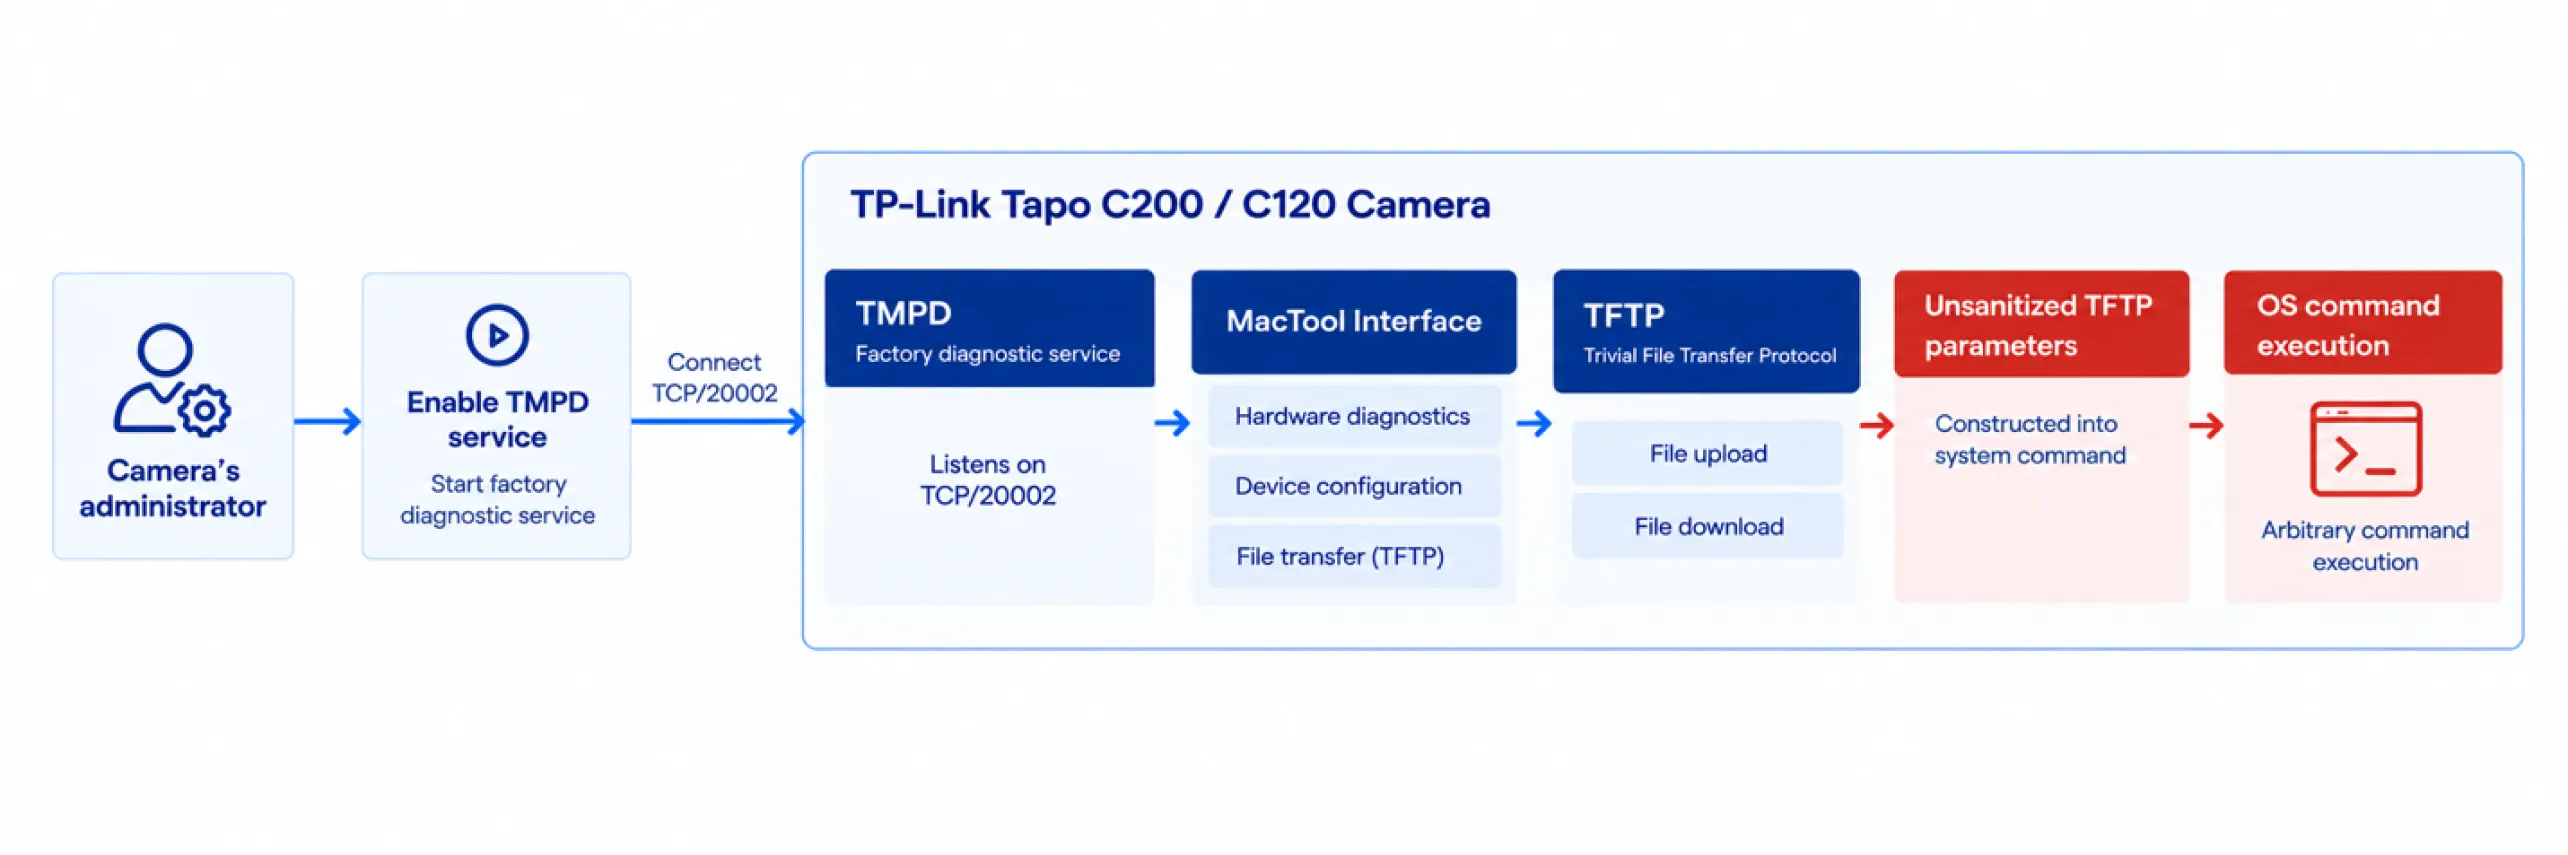
More significantly, Khoi and Thai demonstrated how CVE-2026-102369 can be chained with the previously disclosed authentication bypass (CVE-2026-15315). An unauthenticated attacker on the same local network could exploit the authentication bypass to gain administrative access, enable the diagnostic service, and, following a device reboot, leverage the command injection vulnerability to achieve OS-level command execution.
To demonstrate the security impact, OPSWAT Unit 515 successfully validated the complete exploit chain in a controlled laboratory environment, as shown in the following video.
To prevent potential misuse, OPSWAT has intentionally omitted exploit code, payloads, and detailed reproduction steps from this publication.
Beyond the Camera: The Broader Threat of OS-Level Compromise
An authentication bypass can expose live camera feeds, recordings, and administrative functions, posing serious risks to user privacy and device security. However, the immediate impact is primarily limited to the camera and the data it handles.
OS-level compromise takes this threat significantly further. Attackers could gain full control of the device, deploy malware, establish persistent access, and potentially weaponize the compromised camera to launch attacks against other systems it can reach over the network. This could include scanning for vulnerable devices or targeting internal services, extending the security impact far beyond the camera itself.
补救措施
TP-Link has released firmware updates addressing all vulnerabilities reported by our researchers in the affected Tapo C200 V5 and Tapo C120 V1 cameras. OPSWAT recommends that users update their devices to the latest firmware and follow the remediation guidance provided in the official TP-Link security advisory.
Beyond firmware updates, organizations should restrict access to camera management interfaces and implement network segmentation to limit unnecessary communication between IoT devices and sensitive systems. These measures help reduce exposure and contain the impact of potential compromises.
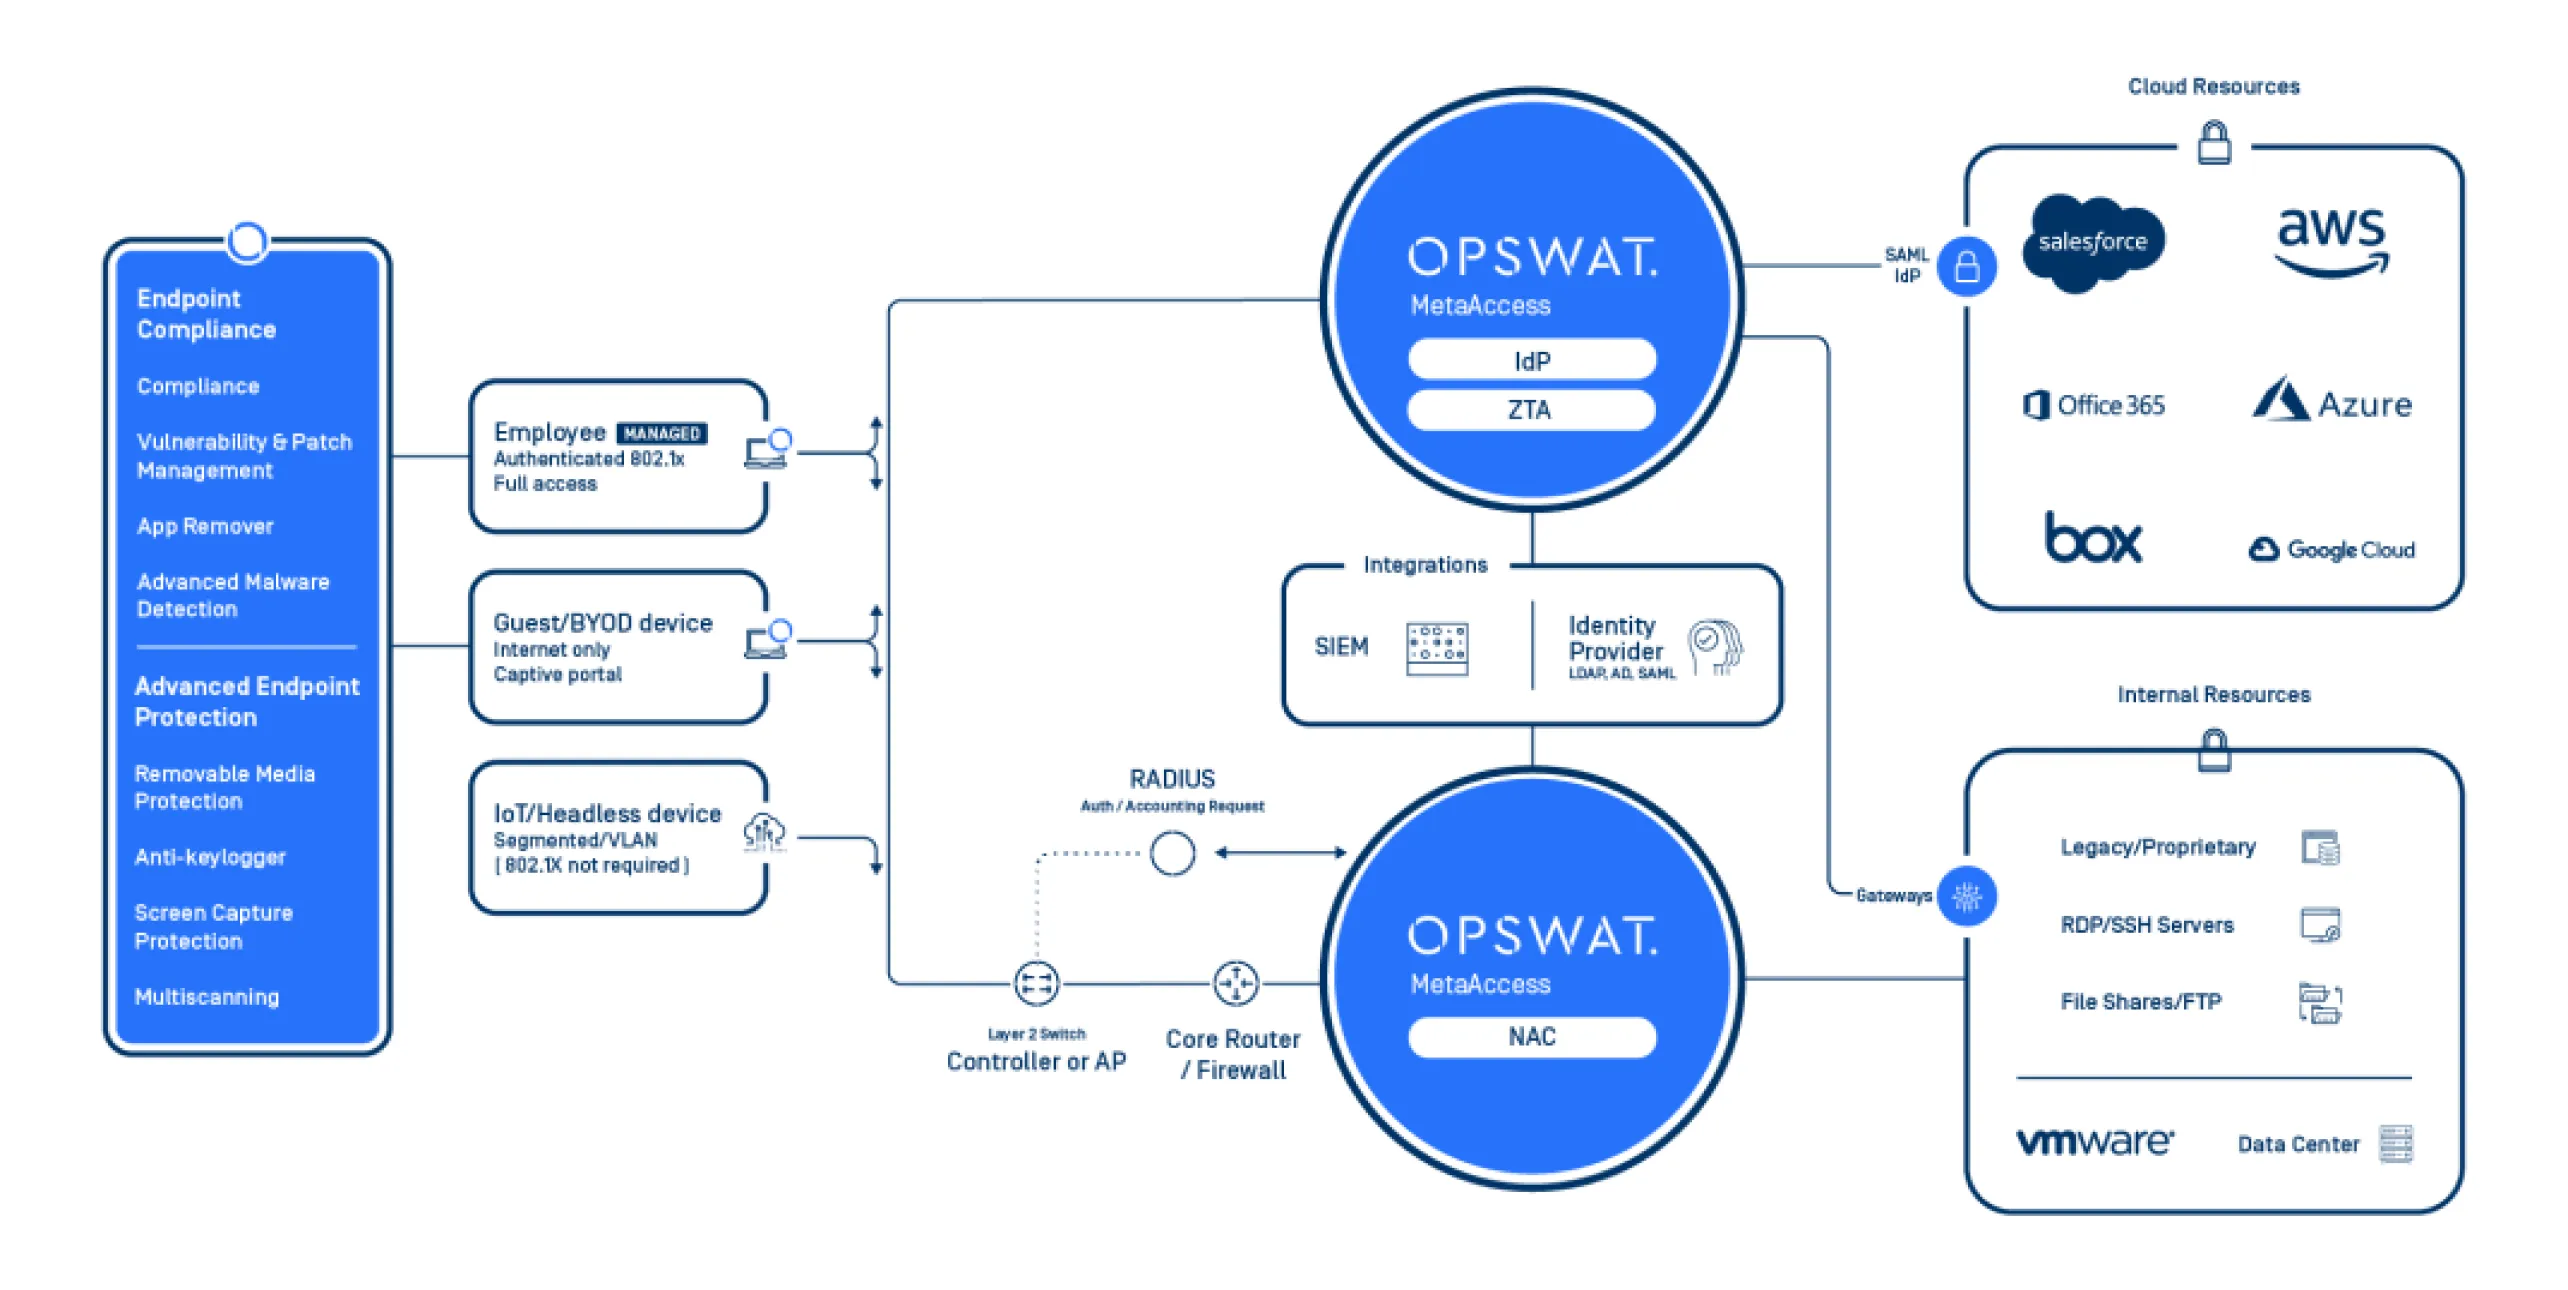
At OPSWAT, our “Trust no file. Trust no device.” philosophy reinforces a Zero Trust approach in which no connected device is inherently trusted. Through the MetaDefender Platform and its MetaDefender NAC capabilities, organizations can discover and identify IoT devices, enforce granular network access policies, and segment devices such as IP cameras using VLANs and access control lists (ACLs). By limiting the systems a compromised device can reach, organizations can reduce the potential impact of exploitation and prevent a single device compromise from escalating into a broader network security incident.
Advancing Security Research with OPSWAT Unit 515
The discovery of six CVEs, including an exploit chain leading to OS-level compromise, marks a significant outcome of OPSWAT Unit 515’s research. Beyond identifying individual vulnerabilities, the investigation demonstrates the importance of understanding how security weaknesses can be combined to create more sophisticated attack scenarios.
OPSWAT Unit 515 is OPSWAT's elite red team, specializing in advanced penetration testing, zero-day vulnerability research, and real-world attack simulations. Through proactive security research, Unit 515 continues to uncover previously unknown vulnerabilities, investigate complex attack techniques, and demonstrate their real-world security impact.
Learn more about OPSWAT Unit 515 and our ongoing efforts to advance offensive security research and strengthen cybersecurity across connected technologies and critical infrastructure.